WO2011125828A1 - 書類管理システム、判定装置、データ出力制御装置、書類管理方法、書類管理プログラム - Google Patents
書類管理システム、判定装置、データ出力制御装置、書類管理方法、書類管理プログラム Download PDFInfo
- Publication number
- WO2011125828A1 WO2011125828A1 PCT/JP2011/058191 JP2011058191W WO2011125828A1 WO 2011125828 A1 WO2011125828 A1 WO 2011125828A1 JP 2011058191 W JP2011058191 W JP 2011058191W WO 2011125828 A1 WO2011125828 A1 WO 2011125828A1
- Authority
- WO
- WIPO (PCT)
- Prior art keywords
- information
- document
- data
- management
- policy
- Prior art date
- Legal status (The legal status is an assumption and is not a legal conclusion. Google has not performed a legal analysis and makes no representation as to the accuracy of the status listed.)
- Ceased
Links
Images




Classifications
-
- G—PHYSICS
- G06—COMPUTING OR CALCULATING; COUNTING
- G06Q—INFORMATION AND COMMUNICATION TECHNOLOGY [ICT] SPECIALLY ADAPTED FOR ADMINISTRATIVE, COMMERCIAL, FINANCIAL, MANAGERIAL OR SUPERVISORY PURPOSES; SYSTEMS OR METHODS SPECIALLY ADAPTED FOR ADMINISTRATIVE, COMMERCIAL, FINANCIAL, MANAGERIAL OR SUPERVISORY PURPOSES, NOT OTHERWISE PROVIDED FOR
- G06Q10/00—Administration; Management
- G06Q10/10—Office automation; Time management
-
- G—PHYSICS
- G06—COMPUTING OR CALCULATING; COUNTING
- G06F—ELECTRIC DIGITAL DATA PROCESSING
- G06F21/00—Security arrangements for protecting computers, components thereof, programs or data against unauthorised activity
- G06F21/60—Protecting data
- G06F21/62—Protecting access to data via a platform, e.g. using keys or access control rules
- G06F21/6218—Protecting access to data via a platform, e.g. using keys or access control rules to a system of files or objects, e.g. local or distributed file system or database
Definitions
- the embodiment of the present invention relates to a technique for digitizing a paper document and storing it as original data and managing operations on the original data such as browsing and electronic information and copying to paper.
- the scope of compliance is not limited to the original, but extends to all copies where the information resides.
- events that lead to customer information leaks should not occur for financial institutions under the supervision of the Financial Services Agency, and even if such an event occurs, it is necessary to be able to elucidate the background and route. is there. Therefore, access authority management and traceability management of data including paid personal information are fundamental and most important issues for strengthening compliance.
- the embodiment of the present invention has also been made to solve the above-described problems.
- a policy corresponding to a document type is created, and this policy is managed to facilitate the management and system. It aims at providing the technology which reduces the load of the.
- the document management system acquires identification information of original data that is digital data of a paper document, or a management ID that is identification information of duplicate data of the original data, and uses the management ID to obtain information regarding the type of the paper document Is obtained from the storage unit, and an information acquisition unit for outputting the document type information is provided.
- the document management system acquires operation information that is information for identifying an operation type for original data or duplicate data, user information that is information about a user, and the document type information.
- the policy information defining the user's operation range is selected based on the document type information, and whether the user defined by the user information has the authority to execute the operation defined by the operation information is selected.
- a policy selection determination unit for determining according to the definition of the policy information.
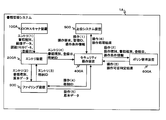
- FIG. 1 is a diagram illustrating an example of a configuration of a document management system according to Embodiment 1.
- FIG. 6 is a diagram illustrating an example of a data configuration of a management file according to Embodiments 1 and 2.
- FIG. It is a figure which shows an example of the process of the document management system concerning Embodiment 1, and the flow of data.
- 2 is a diagram illustrating an example of the configuration and operation of the OCR scanner device according to Embodiment 1.
- FIG. 2 is a diagram illustrating an example of the configuration and operation of an entry device and a filing device according to Embodiment 1.
- FIG. 6 is a diagram illustrating an example of the configuration and operation of the security operation device according to Embodiment 1.
- FIG. 6 is a diagram illustrating an example of the configuration and operation of a host system apparatus according to Embodiments 1 and 2.
- FIG. 6 is a diagram illustrating an example of the configuration and operation of the security operation device according to Embodiment 1.
- FIG. It is a figure which shows an example of a structure and operation
- FIG. 6 is a diagram illustrating an example of the configuration and operation of the security operation device according to Embodiment 1.
- FIG. 6 is a diagram illustrating an example of data held in a policy storage unit according to Embodiment 1.
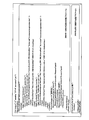
- FIG. 6 is a diagram illustrating an example of a data configuration of a document attribute conversion profile according to Embodiment 1.
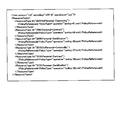
- FIG. 6 is a diagram showing an example of a data configuration of a policy reference file according to Embodiment 1.
- FIG. It is a figure which shows an example of a structure of the document management system which concerns on Embodiment 2.
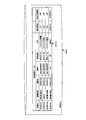
- FIG. It is a figure which shows an example of the table which management DB which concerns on Embodiment 2 hold
- FIG. 10 is a diagram illustrating an example of a data configuration of a document attribute conversion profile according to Embodiment 2.
- FIG. 10 is a diagram illustrating an example of a data configuration of a document attribute conversion profile according to Embodiment 2.
- FIG. 1 shows an example of the data structure of the policy reference file which concerns on Embodiment 2.
- FIG. 1 is a figure explaining one of the effects show
- the document management system acquires identification information of original data that is digital data of a paper document, or a management ID that is identification information of duplicate data of the original data, and uses the management ID to obtain information regarding the type of the paper document Is obtained from the storage unit, and an information acquisition unit for outputting the document type information is provided.
- the document management system acquires operation information that is information for identifying an operation type for original data or duplicate data, user information that is information about a user, and the document type information.
- the policy information defining the user's operation range is selected based on the document type information, and whether the user defined by the user information has the authority to execute the operation defined by the operation information is selected.
- a policy selection determination unit for determining according to the definition of the policy information.
- each device described below can be implemented by either a hardware configuration or a configuration in which hardware resources and software resources cooperate with each device.
- a program that is installed in advance on a computer of a corresponding device from a network or a storage medium and that makes the corresponding device realize a function is used.
- Non-Patent Reference 1 relating to a document in which a rule (policy) format relating to the general reference and editing authority described above is defined is referred to.
- policy a rule relating to the general reference and editing authority described above is defined.
- any expression may be adopted. Note that in the description example of the present embodiment, description of components that are not related to the essence of the present invention is omitted from the name space, attributes, and elements.
- FIG. 1 is a schematic diagram showing a configuration of a document management system according to each embodiment.
- the document management system 1 reads an original document (paper document), converts it into image data, recognizes character information from the image data, generates text data as digital data, and determines and sets the document type.
- a scanner device 100 is included.
- the document management system 1 includes an entry device 200 that generates original data by displaying image data and recognized text data, and supporting correction and complementation of the text data.
- the document management system 1 further includes a filing device 300 that stores original data and a security operation device 400 that centrally manages a copy of an information medium derived from the original data of the document.
- the document management system 1 holds policy data for document management, and requests a policy management apparatus 600 for determining whether or not to operate a document based on a request condition for the operation of the document, and an operation for the document.
- a plurality of host system devices 500 1 to 500 m (hereinafter referred to as host system devices 500). These devices are configured to be able to communicate with each other.
- the types of document operations required by the host system apparatus 500 include browsing of original data, electronic copying, printing on paper, erasing, etc., and processing of electronic copying, printing, and scanning from original data. There are browsing, copying, printing, erasing, and disposal of duplicated copies.
- the duplicate includes various information media such as electronic files, paper, and CD-ROM.
- the host system device 500 can be realized as long as it can input an operation request to an information medium such as electronic data or paper.
- an information medium such as electronic data or paper.
- a mobile phone, a PC (Personal Computer) is used according to the used medium.
- It is realized as various devices such as a digital multifunction device (Multi-Function Printer), a printer, a copier / scanner, a shredder, a microfilm reader, a DVD reader, and a multi-drive, and operates in cooperation with the security operation device 400.
- a digital multifunction device Multi-Function Printer
- printer printer
- copier / scanner a copier / scanner
- a shredder a microfilm reader
- DVD reader Digital Multi-drive
- the document management system 1 assigns a unique management ID (Identification) for individual identification of the information medium described above to each information medium, and creates, discards, and interrelates (system and System type management is performed by associating the status of media type) and media usage with the original document.
- a unique management ID Identity
- system and System type management is performed by associating the status of media type
- the document management system 1 can convert the electronic data into an electronic file in a file format including a management ID.
- the converted electronic file is called a management file.
- the management file includes header information including a management ID and attribute information, a usage control policy, and authentication information for the management file, in addition to the electronic data body of the target information.
- the management file includes a header part, a usage control policy part, a body part, and an authentication data part.
- the header part has a configuration including a management ID of the electronic data, a management ID of the parent information medium, a generation number, a medium type, file information, file storage information, and information management server information.
- the configuration of the header portion is not limited to this.
- the management ID of the parent information medium for example, the management ID of the original electronic data when the electronic data is copied, the management ID of the original electronic data when printing the electronic data and outputting the paper medium, and the paper medium with a scanner
- the management ID assigned to the paper medium when converted to electronic data is used.
- the generation number corresponds to the generation number in the system relationship in which the management file copied from the original data is managed with the parent, child, and grandchild, starting from the original data first registered in the filing apparatus 300 of the document management system 1. It represents the generation number. For example, if the generation number of the management file corresponding to the parent is 1, the generation number of the child information medium corresponding to the duplication is 2, and the generation number of the grandchild information medium corresponding to the duplication of the child information medium is 3.
- the expression format of the generation number is not limited to this.
- the file information includes the file format, file size, creator information, creation date information, and creation location information of the electronic data.
- the file storage information includes information indicating whether or not the electronic data main body stored in the body portion is encrypted, and if encrypted, further includes information on the encryption algorithm, the encryption key, and the encryption module. It is out.
- the information management server information is information for verifying the MAC address, IP address, URI, and authentication data part of the security operation device 400. As information for verifying the authentication data portion, encryption key information or an encryption key certificate related to the key may be stored.
- the usage conditions for the electronic data such as the expiration date of the electronic file, the location where it can be used, the disclosure range information of the organization, etc.
- the usage control policy information related to the usage constraint describing the processing of the electronic file to be permitted or prohibited is stored.
- the electronic data body or encrypted data obtained by applying encryption processing to the electronic data is stored.
- authentication data information obtained by performing encryption processing by the security operation device 400 on the header part, the usage control policy part, and the body part is stored.
- Data authentication information includes digital signatures using public key cryptosystems such as DSA (Digital Signature Algorithm), RSA (Rivest-Shamir-Adleman Scheme), ECDSA (Elliptic Curves DSA), MAC (using hash functions and common key cryptography).
- Message Authentication Code is used, but not limited to these.
- FIG. 3 is a diagram illustrating the flow of data and processing between each device of the document management system 1.
- Entry described in FIG. 3 indicates the flow of registration processing of data and each ID, and the processing proceeds in the order in parentheses.
- Operaation described in FIG. 3 indicates the flow of processing when the above-described operation request such as browsing of original data, electronic copying, etc. is received from the user, and processing is performed in the order in parentheses. Advances. Hereinafter, details of each of these processes will be described for each apparatus.
- the operation request unit 101 of the OCR scanner device 100 sends a document reading request to the central control unit 102 (ST1).
- the central control unit 102 When the central control unit 102 receives a document reading request from the operation request unit 101, the central control unit 102 sends a paper feeding process start request to the paper feeding unit 103 (ST2). The central control unit 102 sends a request to start scanning processing of the document to the scanner unit 104 after the paper feeding processing start request to the paper feeding unit 103 (ST3).
- the paper feed unit 103 Upon receiving a document paper feed process start request from the central control unit 102, the paper feed unit 103 starts the paper feed process so that the scanner unit 104 reads the document. The data is sent to the control unit 102 (ST4).
- the scanner unit 104 Upon receiving a document scanning process start request from the central control unit 102, the scanner unit 104 generates image data that is digital data of the document in conjunction with the paper feeding operation of the paper feeding unit 103, and generates the generated image data. Is sent to the central control unit 102 (ST5). When a reading error occurs, the contents are sent to the central control unit 102.
- the central control unit 102 When the central control unit 102 receives the transmission completion notification from the paper feeding unit 103 and the image data from the scanner unit 104, the central control unit 102 sends the image data to the document attribute judgment unit 105 and sends a document type judgment request for the image data. (ST6).
- the scan processing start request to the scanner unit 104 may be sent from the paper feed unit 103 in accordance with the progress of the paper feed operation.
- the document attribute determination unit 105 receives the image data of the document from the central control unit 102, analyzes the paper size and description of the document, generates text data (hereinafter, recognized text data), and determines the document type. To do.
- the document type is, for example, classification information that can be organized according to differences in document handling rules and business flows such as catalogs, design documents, contracts, and identity verification forms.
- the method of analyzing the description of a document and the method of determining the document type are: text analysis from image data, determination from the document title and keyword, analysis by determining the document serial number, document such as a frame line Any of the methods for determining from the layout pattern may be used.
- the document type may be determined from information stored in the tag.
- these barcodes, tags, RFIDs, and the like are based on character information such as an array of numbers, so these barcodes are also included in the concept of character information. Any method or a combination thereof may be used as long as it can organize document types from image data.
- the document attribute determination unit 105 sends the image data, the recognized text data, and the determined document type to the data transmission unit 106 (ST7).
- general techniques disclosed in, for example, Japanese Patent Laid-Open Nos. 2003-168073 and 2003-168074 may be employed.
- the data transmitting unit 106 Upon receiving the image data, the recognized text data, and the determined document type from the document attribute determining unit 105, the data transmitting unit 106 transmits the image data, the recognized text data, and the document type to the entry device 200 (ST8).
- the entry management unit 201 of the entry device 200 is a functional unit that manages all correction and interpolation operations, and includes an entry management DB 2011.
- the entry management DB 2011 temporarily stores the image data, the recognized text data, and the document type transmitted from the data transmission unit 106 in association with each other and the corrected text data (hereinafter, corrected) from the editing support unit 202. Text data) is also temporarily stored in association with each other.
- the editing support unit 202 is a functional unit that supports confirmation, correction, and interpolation of character string data by a data correction operator (puncher).
- a data correction operator Puncher
- the editing support unit 202 simultaneously displays image data and recognized text data corresponding to the image data by using the display unit and input unit of the entry device 200, and supports correction and interpolation work of character string data by a puncher.
- the entry management DB 201 stores a table in which puncher identification information and document types are associated with each other, so that the entry management unit 201 corrects and interpolates only data of a specific document type for a specific puncher. Can be controlled. Alternatively, control can be performed so that correction and interpolation work is not performed on data of a specific document type.
- the entry management unit 201 of the entry device 200 receives the document type, image data, and recognized text data from the OCR scanner device 100 (ST8), and temporarily stores these data in the entry management DB 2011 in association with each other. In response to a request from the editing support unit 202, the entry management unit 201 sends image data and recognized text data to the editing support unit 202 (ST9).
- the puncher compares the displayed image data with the recognized text data to correct the character string data erroneously recognized by the OCR scanner device 100 to regular data.
- the corrected text data is transmitted to the entry management unit 201 (ST10) and held in the entry management DB 2011.
- the filing control unit 301 of the filing device 300 includes image data and regular text data (corrected text data when correction or complement is required, or recognized text data when correction or complement is not required), and document type Are acquired (ST11) and stored in the original data storage unit 302 in association with each other (ST12).
- image data and regular text data are referred to as original data.
- the filing control unit 301 obtains the storage type information when the document type and the original data are held in the original data storage unit 302, and sends them to the entry device 200 as a storage ID (ST13).
- the entry control unit 201 Upon receipt of the storage ID from the filing device 300, the entry control unit 201 sends the storage ID and the document type of the document to the security operation device 400 and requests a document registration process (ST14).
- the communication management unit 401 of the security operation device 400 When the communication management unit 401 of the security operation device 400 receives the document type and the storage ID together with the document registration processing request from the entry device 200, the communication management unit 401 sends the document type and the storage ID to the security control unit 402 (ST15).
- the security control unit 402 Upon receiving the document type and storage ID from the communication management unit 401, the security control unit 402 sends out the document type, storage ID, medium type, and location to the management DB control unit 403 (ST16), and registers in the management DB 404. Is requested (ST17).
- the medium type transmitted here is “electronic data” because it is the original data of the document. Further, since the location is the original data, it becomes a “filing device”.
- FIG. 7 is a diagram illustrating a data configuration recorded in the management DB 404.
- the management DB 404 stores data in association with each other using the system management table 4041.
- the system management table 4041 has management ID, document type, storage ID, medium type information, location, parent management ID, and original management ID data.
- the location indicates the location or owner of the original data or a copy thereof.
- the parent management ID indicates the management ID of the information medium that is the copy source of the information medium indicated by the management ID.
- the management ID of the original indicates the management ID of the original data that is the origin of the copy that is derived from the original data by repeatedly copying such as electronic copying, printing, and scanning. For example, a copy (management ID: # 1001101) of original data (management ID: # 1000101) of the contract (life) in FIG. 7 printed on paper has a parent ID of # 1000101 and an original management ID of # 1000101. .
- the management DB control unit 403 sends the management ID issued for the original data of the document to the security control unit 402 (ST18).
- the security control unit 402 Upon receiving the management ID from the management DB control unit 403, the security control unit 402 sends the processing result of the registration request of the entry device 200 including the management ID to the communication management unit 401, and returns a reply to the entry device 200. Request (ST19).
- the communication management unit 401 sends processing result information including the management ID to the entry device 200 (ST20). This completes the registration process.
- the request reception unit 501 of the host system apparatus 500 When the request reception unit 501 of the host system apparatus 500 receives an operation request for a document to which a management ID is assigned, the request reception unit 501 operates the management ID of the document and the type of operation for the original data or duplicate data.
- the contents of the document operation request including the information for identifying the user and the user information related to the requesting user are sent to the host control unit 502 (ST31).
- the user information includes information necessary for determining whether or not the document operation is possible, such as information identifying an individual such as an employee number, information identifying a department to which the user belongs, and attribute information such as a manager or regular employee. When copying, all user information that receives the copy is also included.
- the upper control unit 502 Upon receiving the management ID and the document operation request content from the request receiving unit 501, the upper control unit 502 sends a context information acquisition request to the context information acquiring unit 503 (ST32).
- the context information acquisition unit 503 acquires context information about the higher level system device 500 such as an IP address and a MAC address from the related functions of the operating system, and the like. (ST33).
- the context information acquisition unit 503 and ST32 to ST33 can be omitted.
- the authority of document operation by the connection domain is effective in a scene where, for example, only LAN connection on the 7th floor of the head office building can be printed, but in the case of wireless LAN connection, all copying is disabled.
- the context information is information related to the device of the host system device 500.
- the host system device 500 is a device that is used by the user and is information that can identify the user. Therefore, the context information is included in the information about the user.
- the host control unit 502 sends the operation request contents, management ID, and operation condition information to the security operation device 400 (ST34).
- the operation condition information is information including user information, context information, and other information necessary for document operation of the document management system 1.
- the operation accepting unit 405 of the security operation device 400 receives the document operation request content, management ID, and operation condition information from the host system device 500, the operation request content, management ID, and operation condition information are sent to the security control unit 402. Sending out and requesting document operation processing (ST35).
- the security control unit 402 Upon receiving the document operation request content, management ID, and operation condition information from the operation accepting unit 405, the security control unit 402 sends the management ID to the management DB control unit 403, and the document of the document managed with the management ID A request is made to return the type (ST36).
- the management DB control unit 403 When the management DB control unit 403 receives the transmission request for the document type including the management ID from the security control unit 402, the management DB control unit 403 searches the management DB 404 for the management ID and acquires the associated document type (ST37). The management DB control unit 403 sends the acquired document type to the security control unit 402 (ST38).
- the security control unit 402 Upon receiving the document type from the management DB control unit 403, the security control unit 402 sends the operation type, the document type, and the operation condition information included in the document operation request content to the policy management apparatus 600, and the operation condition information In step ST39, a request is made to determine whether or not the management type can be operated.
- various types of operations such as browsing of original data, electronic copying, printing, erasing, electronic copying derived from original data, reproduction of printed matter (electronic copying, printing, scanning), electronic file, document, CD-ROM, etc.
- the policy control unit 601 of the policy management device 600 When the policy control unit 601 of the policy management device 600 receives an operation availability determination request including the operation type, document type, and operation condition information from the security operation device 400, the policy control unit 601 sends the document type to the policy resolution unit 602. The selection of a policy file (policy information) corresponding to the document type is requested (ST40).
- the policy resolution unit 602 When the policy resolution unit 602 receives a policy file selection request including the document type from the policy control unit 601, the policy resolution unit 602 refers to the document attribute conversion profile 6041 and the policy reference file 6042 stored in the policy storage unit 604 and refers to the document type. A policy file corresponding to is selected (ST41).
- FIG. 12 shows an example of data held in the policy storage unit 604.
- the document attribute conversion profile 6041 manages the relationship between the document type and the policy identifier.
- FIG. 13 shows a data configuration example of the document attribute conversion profile 6041. In FIG. 13, for example, when the document type is “catalog”, the policy specified by the policy identifier “NoPersonal-Commodity” is referred to.
- the policy reference file 6042 manages the relationship between the policy identifier and the policy file 6043.
- FIG. 14 shows a data configuration example of the policy reference file 6042.
- the entity of the policy file whose policy identifier is “NoPersonal-Commodity” is “policy-01.xml”.
- the policy resolution unit 602 refers to the document attribute conversion profile 6041 from the policy storage unit 604, searches for a policy identifier whose document type (ResourceReferenceValue Id) is “contract”, and determines a policy of “Personal-Contract”. Get identifier (ResourceTypeId).
- the policy resolution unit 602 refers to the policy reference file 6042 from the policy storage unit 604, searches for a policy file (PolicyReferenceId) corresponding to the policy identifier “Personal-Contract”, and handles the “contract”. 6043 “policy-02.xml” is acquired.
- the policy resolution unit 602 sends the acquired policy file 6043 “policy-02.xml” to the policy control unit 601 (ST42).
- the policy control unit 601 sends the policy file 6043 received from the policy resolution unit 602, the operation type and operation condition information received from the security operation device 400 to the policy evaluation unit 603 (ST43).
- the policy evaluation unit 603 determines whether or not an operation can be performed under the operation condition according to the description in the policy file 6043. For example, the determination is made according to the specifications disclosed in Non-Patent Document 1. As for the description contents of the policy file 6043, for example, the standard description specification including the description sample is disclosed in Non-Patent Document 1. In the first embodiment, the policy file 6043 defines the operation range of the user, and defines information that the user can execute (or cannot execute) the operation.
- the policy evaluation unit 603 makes a determination in accordance with the policy file 6043, and sends an operation availability determination result to the policy control unit 601 (ST44).
- Policy control unit 601 sends an operation availability determination result to security operation device 400 (ST45).
- the security control unit 402 of the security operation device 400 sends the management ID of the operation request to the management DB control unit 403 only when the operation availability determination result received from the policy management device 600 is “Yes”, and the management ID The management DB control unit 403 is requested to acquire the original data corresponding to (ST46).
- the operation availability determination result is “No”
- the host system 500 is notified of the operation impossibility through the operation reception unit 405.
- the management DB control unit 403 searches the system management table 4041 of the management DB 404 and acquires the storage ID associated with the management ID (ST47). .
- the storage ID is sent to the filing device 300, and the transmission of the original data recorded with the storage ID is requested (ST48).
- the filing control unit 301 of the filing device 300 searches the original data storage unit 302 to search for original data corresponding to the storage ID (ST49). ).
- the filing control unit 301 sends the original data to the security operation device 400 (ST50).
- the management DB control unit 403 sends the original data received from the filing device 300 to the security control unit 402 (ST51).
- the security control unit 402 Upon receiving the original data from the management DB control unit 403, the security control unit 402 performs processing according to the operation type, and sends the operation processing result to the operation receiving unit 405 (ST52). The following operation process is performed according to the operation type.
- the security control unit 402 If the operation type is browsing of original data, the security control unit 402 sends the original data to the operation receiving unit 405, and the operation receiving unit 405 sends the original data to the higher-level system device 500. Is sent out.
- the security control unit 402 issues a management ID for the duplicate data.
- the management DB control unit 403 registers the management ID issued in the system management table 4041 of the management DB 404, registers the management ID requested for operation in the parent management ID, and also stores the original corresponding to the parent management ID.
- the management ID is registered in the original management ID.
- the document type associated with the management ID requested to be operated is registered, the medium type is “electronic data”, and the location is registered user information included in the operation condition information from the host system apparatus 500.
- the security control unit 402 creates the management file shown in FIG. 2 and sends it to the operation accepting unit 405 as an operation processing result.
- the operation reception unit 405 outputs the management file to a device that controls the writing of the medium so that the created management file is copied to the medium specified by the user.
- the security control unit 402 issues a management ID for print management, and the system management table 4041 of the management DB 404 through the management DB control unit 403 as in (b) above.
- the management ID issued this time is registered, the original management ID requested for operation is registered in the parent management ID, and the management ID of the original corresponding to the parent management ID is registered in the management ID of the original.
- the document type the document type associated with the management ID requested for operation is registered, the medium type is “paper”, and the location is registered user information included in the operation condition information from the host system device 500. .
- the security control unit 402 sends out the management ID and original data issued to the operation receiving unit 405 as an operation processing result.
- this operation is repeated for the number of users.
- the original data sent to the operation reception unit 405 is attached with an ID tag in which the management ID is stored in an optical tag such as a barcode, a two-dimensional code, a color code, and a stealth barcode, or an electronic tag such as an RFID.
- the operation receiving unit 405 outputs the original data with the management ID attached thereto to a predetermined image forming apparatus, thereby printing on the paper.
- the operation accepting unit 405 sends the operation processing result received from the security control unit 402 to the host system device and completes the processing (ST53).
- the security control unit 402 receives the storage ID from the management DB control unit, and sends the storage ID to the higher system apparatus 500 instead of the original data.
- the form to do may be sufficient.
- the host system device 500 sends the storage ID to the filing device 300 and acquires the corresponding original data.
- the storage ID and management ID are sent to the host system device 500, and the original data is acquired and the ID tag storing the management ID is pasted outside the security operation device. Form may be sufficient.
- FIG. 15 is a schematic diagram showing the configuration of the document management system according to the second embodiment.
- the same parts as those in FIG. 3 are denoted by the same reference numerals, detailed description thereof is omitted, and different parts are mainly described here.
- the second embodiment is a modification of the first embodiment.
- a document registration date is added, and even if the handling of the document changes in the years such as legal revision, This is a form in which a policy suitable for the document registration date is selected and appropriate document management can be performed.
- the registration date may be any form such as the date and time when the original data is stored in the filing device 300, the contract date of the contract document, the application date, or the catalog issue date.
- the document management system 1A described in the second embodiment includes an OCR scanner device 100A, an entry device 200A, a filing device 300, a security operation device 400A, a host system device 500, and a policy management device 600A.
- the original document registration process in the second embodiment is performed in substantially the same manner as in the first embodiment, but the OCR scanner device 100A specifies the column for the contract date, application date, and catalog issue date in the contract document, The date is acquired as the registration date and transmitted to the entry device 200A (see ST8 in FIG. 5). When the registration date is the date and time when the original data is stored in the filing device 300, this process is not necessary.
- the entry device 200A sends the registration date in addition to the document type and the storage ID.
- FIG. 16 shows a configuration example of the management DB 404A in this embodiment.
- the operation of the document registered in the document management system 1A is performed in the same manner as in the first embodiment, but in ST37 to ST39 (see FIG. 9), in addition to the document type, the registration date is acquired and transmitted by each unit.
- the policy control unit 601A of the policy management device 600A receives an operation availability determination request including the operation type, document type, registration date, and operation condition information from the security operation device 400A, the policy control unit 601A sends the document type and registration date to the policy resolution unit 602A. Send out and request selection of a policy file corresponding to the document type (ST40A).
- the policy resolution unit 602A When the policy resolution unit 602A receives a policy file selection request including the document type and registration date from the policy control unit 601A, the policy resolution unit 602A refers to the document attribute conversion profile 6041A and the policy reference file 6042A stored in the policy storage unit 604A. Select a policy file corresponding to the document type.
- the document attribute conversion profile 6041A manages the relationship between the document type and registration date, and the policy identifier.
- FIG. 18 shows a data configuration example of the document attribute conversion profile 6041A.
- the condition of the registration date is defined in the Condition tag, and when this condition is satisfied, it is defined so that the subsequent document type determination is performed.
- the condition of the registration date is defined in the Condition tag, and when this condition is satisfied, it is defined so that the subsequent document type determination is performed.
- the policy reference file 6042A defines the relationship between the policy identifier and the policy file 6043.
- FIG. 19 shows a data configuration example of the policy reference file 6042A.
- the policy file entity having the policy identifier “2000.NoPersonal-Commodity” is “policy-01.xml”.
- the policy file selection operation when the registration date is “2009/01/05” and the document type is “contract” will be described below.
- the policy resolution unit 602A refers to the document attribute conversion profile 6041A from the policy storage unit 604A, and evaluates the conversion profile that handles the document whose registration date is “2009/01/05”. In the case of FIG. 18, the profile whose ResourceProfile Id is “2000_resource_profile” is evaluated.
- the policy resolution unit 602A Since the registration date “2009/01/05” is included in the period from 2000 to 2009 and meets the conditions of the profile, the policy resolution unit 602A has a policy whose document type (ResourceReferenceValue Id) is “contract”. Search for the identifier in the profile and obtain a ResourceTypeId of “2000.Personal-Contract”.
- the policy resolution unit 602A refers to the policy reference file 6042A (see FIG. 19) from the policy storage unit 604A, searches for the PolicyReferenceId corresponding to the policy identifier “2000.Personal-Contract”, and obtains the “contract”.
- a policy file 6043 “policy-02.xml” to be handled is acquired (ST41A).
- the policy resolution unit 602A sends the acquired policy file 6043 “policy-02.xml” to the policy control unit 601A (ST42A).
- the subsequent processing is the same processing as ST43 to ST53 of the first embodiment.
- the document management system according to the first and second embodiments is used by determining a document type such as a catalog or a contract document from a paper document, and setting a predefined policy for the document type in the document. Restrict the user's operations. Conventionally, a policy is defined for each document. However, in the document management system according to the first and second embodiments, a policy is defined for each document type using a document type that is clearly a small number with respect to the number of documents. Therefore, the management becomes easy and the processing load of the system is reduced.
- the document management system according to the first and second embodiments, it is possible to manage original data and a copy thereof, and to confirm where these media are located. Therefore, even if an event that leads to leakage of customer information occurs, it becomes easy to elucidate the process and route.
- the policy file is selected using the date related to the original data, which is the registration date, in addition to the document type, but the mode is not limited, and not only “date” but also “day of the week”. , “Period”, “time”, “time”, “period”, etc. Moreover, not only the registration date (registration date and time) related to the original data but also the date and time when the operation is performed.
- the policy management apparatus 600A acquires the current date and time from, for example, the system clock or an external server, and selects the policy file by the above-described processing using the acquired current date and time. In this way, for example, from the viewpoint of security, even when internal rules are adopted such as not permitting copying of the original outside business hours, or not permitting copying of the original on holidays or holidays
- the aspect of Embodiment 2 can be adapted.
- the document type is relatively large such as “catalog” and “contract document”.
- “catalog” for example, “product A catalog” or “product A A more detailed classification such as “a catalog of one service” may be used.
- the OCR scanner device 100 has a scanner device such as an MFP and an OCR function that converts (recognizes) character information described in image data into electronic data. It may be configured with a computer.
- the document type and the policy file are associated with each other based on the description information in the XML format.
- the format is not limited, and any format or processing format that makes the correspondence clear. Anything may be used.
- a policy file is selected by using two definition files, ie, a document attribute conversion profile and a policy reference file.
- a single file in which a document type and a policy file are directly associated with each other is selected. You may choose.
- a plurality of entry devices 200 are provided according to the number of punchers.
- the configuration may be a stand, or from the viewpoint of load distribution, a configuration in which a plurality of devices are prepared as necessary may be used.
- each function unit is not fixed to each device.
- the document attribute determination unit of the OCR scanner device may be arranged in the entry device.
- the information acquisition unit corresponds to the security operation devices 400 and 400A of the above embodiment
- the policy selection determination unit corresponds to the policy management devices 600 and 600A
- the original data storage unit corresponds to the filing device 300 of the above embodiment.
- the image data conversion unit corresponds to the operation request unit 101, the central control unit 102, the paper feed portion 103, and the scanner unit 104 in the above embodiment, and the recognition unit includes the document attribute determination unit 105 and the data transmission unit 106.
- the support unit corresponds to the entry device 200.
- the policy management devices 600 and 600A of the above-described embodiment can be provided as a user operation determination device having an acquisition unit, a policy selection unit, and a policy determination unit.
- the acquisition unit corresponds to the policy control units 601 and 601A of the above embodiment
- the policy selection unit corresponds to the policy resolution units 602 and 602A and the policy storage units 604 and 604A.
- the policy determination unit corresponds to the policy evaluation unit 603 of the above embodiment.
- the security operation device of the above embodiment can be provided as a data output control device having an acquisition unit, a document type information acquisition unit, and an output unit.
- the acquisition unit corresponds to the operation reception unit 405 of the above embodiment
- the document type information acquisition unit corresponds to the management DB control unit 403
- the output unit includes the security control unit 402, the management DB control.
- the method described in the above embodiment is a program that can be executed by a computer, such as a magnetic disk (floppy (registered trademark) disk, hard disk, etc.), an optical disk (CD-ROM, DVD, etc.), a magneto-optical disk ( MO), and can be stored and distributed in a storage medium such as a semiconductor memory.
- a computer such as a magnetic disk (floppy (registered trademark) disk, hard disk, etc.), an optical disk (CD-ROM, DVD, etc.), a magneto-optical disk ( MO), and can be stored and distributed in a storage medium such as a semiconductor memory.
- the storage medium can store a program and can be read by a computer
- the storage format may be any form.
- an OS operating system
- MW middleware
- database management software network software
- the storage medium in the embodiment of the present invention is not limited to a medium independent of a computer, but also includes a storage medium in which a program transmitted via a LAN or the Internet is downloaded and stored or temporarily stored.
- the number of storage media is not limited to one, and the case where the processing in the above embodiment is executed from a plurality of media is also included in the storage medium in the embodiment of the present invention, and the medium configuration may be any configuration. .
- the computer executes each process according to the above-described embodiment based on a program stored in a storage medium, and includes a single device such as a personal computer, and a plurality of devices connected to a network. Any configuration such as a connected system may be used.
- the computer in the embodiment of the present invention is not limited to a personal computer, but includes an arithmetic processing unit, a microcomputer, and the like included in information processing equipment, and the functions of the embodiment of the present invention can be realized by a program. Collectively refers to equipment and devices.
Landscapes
- Engineering & Computer Science (AREA)
- Theoretical Computer Science (AREA)
- Business, Economics & Management (AREA)
- Physics & Mathematics (AREA)
- Entrepreneurship & Innovation (AREA)
- Human Resources & Organizations (AREA)
- Strategic Management (AREA)
- General Physics & Mathematics (AREA)
- General Business, Economics & Management (AREA)
- Bioethics (AREA)
- Tourism & Hospitality (AREA)
- Operations Research (AREA)
- Marketing (AREA)
- Economics (AREA)
- Data Mining & Analysis (AREA)
- Databases & Information Systems (AREA)
- Health & Medical Sciences (AREA)
- Quality & Reliability (AREA)
- General Health & Medical Sciences (AREA)
- Computer Hardware Design (AREA)
- Computer Security & Cryptography (AREA)
- Software Systems (AREA)
- General Engineering & Computer Science (AREA)
- Storage Device Security (AREA)
- Management, Administration, Business Operations System, And Electronic Commerce (AREA)
Abstract
Description
まず、書類管理システムを説明する際の前提となる用語や概要等を説明する。図1は各実施の形態に係る書類管理システムの構成を示す模式図である。
また、書類管理システム1は、画像データと認識されたテキストデータとを表示して、テキストデータの修正、補完作業を支援することで、原本データを生成するエントリ装置200を有する。
さらに、書類管理システム1は、原本データを保存するファイリング装置300と、書類の原本データから派生する情報媒体の複製を一元管理するセキュリティ操作装置400とを有する。
ここで、書類管理システム1は、書類管理のポリシデータを保持し、書類に対しての操作の要求条件を元に、書類の操作可否を判定するポリシ管理装置600と、書類への操作を要求する複数の上位システム装置5001乃至500m(以下、これらを上位システム装置500とする)とを有する。これら各装置は互いに通信可能な構成となっている。
書類の記載内容を分析する方法や書類種別を判定する方法は、画像データから文字解析を行い、書類タイトルやキーワードから判定する方法や、書類整理番号を解析して判定する方法、枠線といった書類のレイアウトパターンから判定する方法のいずれでもよい。また、書類にバーコード、二次元コード、カラーコード、ステルスバーコードといった光学タグやRFIDといった電子タグが貼付されている場合には、当該タグに格納された情報から書類種別を判定してもよい。
なお、これらバーコード、タグ、RFID等は、数字の配列等の文字情報に基づいた形態であるため、これらバーコード等も文字情報の概念に含まれる。画像データから書類種別を整理できる方法であれば、いずれの方法またはその組み合わせでもかまわない。
書類属性判定部105は、画像データ、認識テキストデータ、及び判定した書類種別をデータ送信部106へ送出する(ST7)。なお、文字認識や書類種別の判定については、例えば特開2003-168073号公報、特開2003-168074号公報に開示されている一般的な技術を採用してもよい。
編集支援部202は、エントリ装置200の表示手段、入力手段を用いることで、画像データと、当該画像データに対応した認識テキストデータを同時に表示し、パンチャーによる文字列データの修正、補間作業を支援する。また、エントリ管理用DB2011にパンチャーの識別情報と書類種別とを対応付けたテーブルを保持させることで、エントリ管理部201は特定のパンチャーには特定の書類種別のデータのみ修正、補間作業を行わせるように制御できる。または、特定の書類種別のデータに対しては修正、補間作業を行わせないように制御できる。
(a)ポリシ解決部602は、ポリシ記憶部604から書類属性変換プロファイル6041を参照し、書類種別(ResourceReferenceValue Id)が「契約書」に該当するポリシ識別子を検索し、「Personal-Contract」というポリシ識別子(ResourceTypeId)を取得する。
(b)ポリシ解決部602は、ポリシ記憶部604からポリシ参照ファイル6042を参照し、ポリシ識別子が「Personal-Contract」に該当するポリシファイル(PolicyReferenceId)を検索し、「契約書」を取り扱うポリシファイル6043「policy-02.xml」を取得する。
(c)ポリシ解決部602は、取得したポリシファイル6043「policy-02.xml」をポリシ制御部601へ送出する(ST42)。
(a)セキュリティ制御部402は、操作種別が原本データの閲覧であれば、セキュリティ制御部402は当該原本データを操作受付部405へ送出し、操作受付部405は、上位システム装置500へ原本データを送出する。
(b)操作種別が原本データの複製データをセキュリティ保護した管理ファイルとして払い出す電子コピーの場合、セキュリティ制御部402は、複製データ用の管理IDを発行する。管理DB制御部403は、管理DB404の系統管理テーブル4041に発行された管理IDを登録し、操作要求された管理IDを親の管理IDに登録し、また、親の管理IDに対応した原本の管理IDを、原本の管理IDに登録する。また、操作要求された管理IDに関係づけられた書類種別が登録され、媒体種別は「電子データ」、所在は上位システム装置500からの操作条件情報に含まれる利用者情報が登録される。この後、セキュリティ制御部402は、図2で示した管理ファイルを作成し、操作処理結果として操作受付部405へ送出する。操作受付部405は、作成された管理ファイルが利用者指定の媒体にコピーされるように、媒体の書き込み制御を行っている装置に管理ファイルを出力する。受け取る利用者が複数の場合は、この操作を人数分繰り返す。
(c)原本データを紙に印刷する場合は、セキュリティ制御部402は、印刷物管理用に管理IDを発行し、上述の(b)と同様、管理DB制御部403を通じて管理DB404の系統管理テーブル4041に今回発行された管理IDを登録し、操作要求された元の管理IDを親の管理IDに登録し、親の管理IDに対応した原本の管理IDを原本の管理IDに登録する。書類種別には、操作要求された管理IDに関係づけられた書類種別が登録され、媒体種別は「紙」、所在は上位システム装置500からの操作条件情報に含まれる利用者情報が登録される。この後、セキュリティ制御部402は、操作処理結果として操作受付部405へ発行した管理ID及び原本データを送出する。受け取る利用者が複数の場合は、この操作が人数分繰り返される。なお、操作受付部405へ送出される原本データは、当該管理IDをバーコード、二次元コード、カラーコード、ステルスバーコードといった光学タグやRFIDといった電子タグに格納したIDタグが貼付される。操作受付部405は、この管理IDが貼付された原本データを所定の画像形成装置へ出力することで、紙面に印刷される。
図15は実施の形態2に係る書類管理システムの構成を示す模式図であり、図3と同一部分には同一符号を付してその詳しい説明を省略し、ここでは異なる部分について主に述べる。
なお、「2000年~2009年登録の変換プロファイル」は、書類の登録日が「2000/1/1」から「2009/12/31」の書類で、書類種別とポリシ識別子とを管理するプロファイルを指す。
そして、「2010年以降に登録の変換プロファイル」は、書類の登録日が「2010/1/1」以降の書類で、書類種別とポリシ識別子とを管理するプロファイルを指す。
(a)ポリシ解決部602Aは、ポリシ記憶部604Aから書類属性変換プロファイル6041Aを参照し、登録日が「2009/01/05」の書類を取り扱う変換プロファイルを評価する。図18の場合、ResourceProfile Idが「2000_resource_profile」であるプロファイルを評価する。登録日の「2009/01/05」は、2000年から2009年に含まれ、当該プロファイルの条件に合うため、ポリシ解決部602Aは、書類種別(ResourceReferenceValue Id)が「契約書」に該当するポリシ識別子を当該プロファイル内で検索し、「2000.Personal-Contract」というResourceTypeIdを取得する。
(b)ポリシ解決部602Aは、ポリシ記憶部604Aからポリシ参照ファイル6042A(図19参照)を参照し、ポリシ識別子が「2000.Personal-Contract」に該当するPolicyReferenceIdを検索し、「契約書」を取り扱うポリシファイル6043「policy-02.xml」を取得する(ST41A)。
(c)ポリシ解決部602Aは、取得したポリシファイル6043「policy-02.xml」をポリシ制御部601Aへ送出する(ST42A)。
Claims (9)
- 紙面書類のデジタルデータである原本データの識別情報または原本データの複製データの識別情報である管理IDを取得し、前記管理IDを用いて前記紙面書類の種別に関する情報である書類種別情報を記憶部から取得し、該書類種別情報を出力する情報取得部と、
原本データまたは複製データに対する操作の種類を識別する情報である操作情報と、ユーザに関する情報であるユーザ情報と、前記書類種別情報とを取得し、ユーザの操作範囲を定義したポリシ情報を前記書類種別情報に基づき選択し、前記ユーザ情報で定義されたユーザが、前記操作情報で定義された操作を実行する権限を有するか否かを前記選択されたポリシ情報の定義に則り判定するポリシ選択判定部と、
を有する書類管理システム。 - 請求項1に記載の書類管理システムにおいて、
前記情報取得部は、さらに、取得した前記管理IDを用いて前記原本データに係る日時の情報を取得し、該日時の情報を出力し、
前記ポリシ選択判定部は、さらに、前記情報取得部から出力された日時の情報を取得し、前記書類種別情報と前記日時の情報とに基づきポリシ情報を選択する
書類管理システム。 - 請求項1または請求項2に記載の書類管理システムにおいて、
前記情報取得部は、さらに、現在の日時の情報を取得し、該日時の情報を出力し、
前記ポリシ選択判定部は、さらに、前記情報取得部から出力された日時の情報を取得し、前記書類種別情報と前記日時の情報とに基づきポリシ情報を選択する
書類管理システム。 - 請求項1乃至請求項3のいずれか1項に記載の書類管理システムにおいて、さらに、
原本データを蓄積する原本データ蓄積部を有し、
前記ポリシ選択判定部は、さらに、前記判定の結果を出力し、
前記情報取得部は、さらに、前記判定の結果を取得し、該判定の結果が、前記ユーザが前記操作を実行できるとしたものである場合、前記原本データ蓄積部から前記管理IDに基づき前記IDに対応した原本データを取得し、前記操作情報で定義された操作を実行する装置に該原本データを出力する
書類管理システム。 - 請求項4に記載の書類管理システムにおいて、さらに、
紙面書類を画像データに変換する画像データ変換部と、
前記画像データ内の文字情報及び掛線情報のいずれか一方または両方を認識し、前記文字情報をテキストデータに変換するとともに、前記紙面書類の書類種別情報を、認識した文字情報及び掛線情報のいずれか一方または両方に基づき、前記画像データと前記テキストデータとで関連付けて設定する認識部と、
前記画像データと前記認識部によって変換されたテキストデータとを同時に表示し、前記認識部の認識誤りによって生じた誤記を有するテキストデータが是正されるのを支援する支援部と、を有し、
前記原本データ蓄積部は、前記認識部によって認識されたテキストデータまたは前記支援部による支援によって是正されたテキストデータと、前記画像データとを原本データとして取得して蓄積し、
前記情報取得部は、前記原本データ蓄積部に蓄積された前記原本データの格納場所を示す情報と前記書類種別情報とを取得し、これらの情報を少なくとも含んだレコードを作成し、該レコードに管理IDを付与して記憶部に記憶する
書類管理システム。 - 紙面書類のデジタルデータである原本データに対する操作の種類を識別する情報、または原本データの複製データに対する操作の種類を識別する情報である操作情報と、ユーザに関する情報であるユーザ情報と、紙面書類の種別に関する情報である書類種別情報とを取得する取得部と、
ユーザの操作範囲を定義したポリシ情報を、前記書類種別情報に基づき選択するポリシ選択部と、
前記ユーザ情報で定義されたユーザが、前記操作情報で定義された操作を実行する権限を有するか否かを前記ポリシ選択部によって選択されたポリシ情報の定義に則り判定するポリシ判定部と、
を有するユーザ操作の判定装置。 - 紙面書類のデジタルデータである原本データの識別情報、または原本データの複製データの識別情報である管理IDと、ユーザに関する情報であるユーザ情報と、原本データまたは複製データに対する操作の種類を識別する情報である操作情報とを取得する取得部と、
前記管理IDを用いて前記紙面書類の種別に関する情報である書類種別情報を記憶部から取得し、該書類種別情報を出力する書類種別情報取得部と、
前記書類種別情報取得部によって出力された書類種別情報に基づき前記ユーザ情報で定義されたユーザが前記操作情報で定義された操作を実行する権限を有すると判定され、該判定結果を取得した場合、前記管理IDに対応する原本データを記憶部から取得し、前記操作情報で定義された操作を実行する装置に該原本データを出力する出力部と、
を有するデータ出力制御装置。 - コンピュータが、
紙面書類のデジタルデータである原本データの識別情報、または原本データの複製データの識別情報である管理IDを取得し、前記管理IDを用いて前記紙面書類の種別に関する情報である書類種別情報を記憶部から取得し、該書類種別情報を出力し、
原本データまたは複製データに対する操作の種類を識別する情報である操作情報と、ユーザに関する情報であるユーザ情報と、前記書類種別情報とを取得し、ユーザの操作範囲を定義したポリシ情報を前記書類種別情報に基づき選択し、前記ユーザ情報で定義されたユーザが、前記操作情報で定義された操作を実行する権限を有するか否かを前記選択されたポリシ情報の定義に則り判定する
書類管理方法。 - 紙面書類のデジタルデータである原本データの識別情報、または原本データの複製データの識別情報である管理IDを取得し、前記管理IDを用いて前記紙面書類の種別に関する情報である書類種別情報を記憶部から取得し、該書類種別情報を出力し、
原本データまたは複製データに対する操作の種類を識別する情報である操作情報と、ユーザに関する情報であるユーザ情報と、前記書類種別情報とを取得し、ユーザの操作範囲を定義したポリシ情報を前記書類種別情報に基づき選択し、前記ユーザ情報で定義されたユーザが、前記操作情報で定義された操作を実行する権限を有するか否かを前記選択されたポリシ情報の定義に則り判定する
処理を、コンピュータに実行させる書類管理プログラム。
Priority Applications (2)
| Application Number | Priority Date | Filing Date | Title |
|---|---|---|---|
| US13/635,106 US20130004078A1 (en) | 2010-03-31 | 2011-03-31 | Document management system, evaluation device, data output control device, document management method and document management program |
| CN2011800179995A CN102834841A (zh) | 2010-03-31 | 2011-03-31 | 文档管理系统、判定装置、数据输出控制装置、文档管理方法、文档管理程序 |
Applications Claiming Priority (2)
| Application Number | Priority Date | Filing Date | Title |
|---|---|---|---|
| JP2010081315A JP2011215728A (ja) | 2010-03-31 | 2010-03-31 | 書類管理システム、判定装置、データ出力制御装置、書類管理方法、書類管理プログラム |
| JP2010-081315 | 2010-03-31 |
Publications (1)
| Publication Number | Publication Date |
|---|---|
| WO2011125828A1 true WO2011125828A1 (ja) | 2011-10-13 |
Family
ID=44762766
Family Applications (1)
| Application Number | Title | Priority Date | Filing Date |
|---|---|---|---|
| PCT/JP2011/058191 Ceased WO2011125828A1 (ja) | 2010-03-31 | 2011-03-31 | 書類管理システム、判定装置、データ出力制御装置、書類管理方法、書類管理プログラム |
Country Status (4)
| Country | Link |
|---|---|
| US (1) | US20130004078A1 (ja) |
| JP (1) | JP2011215728A (ja) |
| CN (1) | CN102834841A (ja) |
| WO (1) | WO2011125828A1 (ja) |
Families Citing this family (19)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| US9323466B2 (en) | 2011-04-27 | 2016-04-26 | Commvault Systems, Inc. | System and method for client policy assignment in a data storage system |
| US8717633B2 (en) | 2011-09-20 | 2014-05-06 | Kabushiki Kaisha Toshiba | Printed image erasing system |
| US20140359785A1 (en) * | 2013-05-30 | 2014-12-04 | Microsoft Corporation | Security for Displayed Electronic Content from Unauthorized Access During Application Idle Periods |
| CN103632106A (zh) * | 2013-12-18 | 2014-03-12 | 北京明朝万达科技有限公司 | 一种基于oa流程的oa数据保护方法和系统 |
| CN103824031B (zh) * | 2014-02-28 | 2016-09-14 | 江苏敏捷科技股份有限公司 | 使用电子文件安全标签保证电子文件安全的方法及系统 |
| US10516732B2 (en) * | 2014-05-05 | 2019-12-24 | Datadirect Networks, Inc. | Disconnected ingest in a distributed storage system |
| CN112287389B (zh) * | 2015-03-03 | 2024-08-02 | 旺德海尔斯有限责任公司 | 机器可读标识符中加密数据的访问控制 |
| US10561881B2 (en) * | 2015-03-23 | 2020-02-18 | Tau Orthopedics, Inc. | Dynamic proprioception |
| CN104869119B (zh) * | 2015-05-19 | 2019-02-01 | 上海大学 | 脚本引擎中网络文件的隔离与访问控制方法 |
| CN105005551A (zh) * | 2015-06-29 | 2015-10-28 | 东南(福建)汽车工业有限公司 | 一种在文档修订中实现快速获取图片文字的方法 |
| US10410008B2 (en) | 2016-03-08 | 2019-09-10 | Oracle International Corporation | Thick client policy caching |
| CN108280360A (zh) * | 2017-01-05 | 2018-07-13 | 珠海金山办公软件有限公司 | 一种安全文档日志管理方法及服务器 |
| JP6871840B2 (ja) * | 2017-11-06 | 2021-05-19 | 株式会社日立製作所 | 計算機及び文書識別方法 |
| JP7056514B2 (ja) * | 2018-10-30 | 2022-04-19 | 日本電信電話株式会社 | 管理システム、取得装置及び管理方法 |
| US11616816B2 (en) * | 2018-12-28 | 2023-03-28 | Speedchain, Inc. | Distributed ledger based document image extracting and processing within an enterprise system |
| JP7565188B2 (ja) * | 2020-10-27 | 2024-10-10 | シャープ株式会社 | 画像形成装置、設定方法及びシステム |
| TWI785546B (zh) * | 2021-03-23 | 2022-12-01 | 創鑫智慧股份有限公司 | 浮點數的編碼與解碼的方法與裝置 |
| JP2022148910A (ja) * | 2021-03-24 | 2022-10-06 | 富士フイルムビジネスイノベーション株式会社 | 情報処理装置、情報処理システム、および情報処理プログラム |
| JP7721947B2 (ja) * | 2021-04-09 | 2025-08-13 | 株式会社リコー | 情報処理システム、データ管理装置、データ管理方法及びプログラム |
Citations (2)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| JP2009098779A (ja) * | 2007-10-15 | 2009-05-07 | Fuji Xerox Co Ltd | 文書管理システム、文書管理装置および文書管理プログラム |
| JP2009187374A (ja) * | 2008-02-07 | 2009-08-20 | Toshiba Corp | 情報ライフサイクル管理システム、情報管理サーバ装置、電子媒体制御装置及びプログラム |
Family Cites Families (6)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| CN1245935A (zh) * | 1999-06-21 | 2000-03-01 | 李虹 | 名片全自动识别录入与检索系统 |
| US7757162B2 (en) * | 2003-03-31 | 2010-07-13 | Ricoh Co. Ltd. | Document collection manipulation |
| EP1507402A3 (en) * | 2003-06-23 | 2005-07-20 | Ricoh Company, Ltd. | Access control decision system, access control enforcing system, and security policy |
| EP1551146B1 (en) * | 2004-01-05 | 2011-08-24 | Ricoh Company, Ltd. | Document security management for repeatedly reproduced hardcopy and electronic documents |
| CN100546332C (zh) * | 2005-08-22 | 2009-09-30 | 株式会社理光 | 图像处理系统,方法和程序以及图像形成装置 |
| JP4817994B2 (ja) * | 2006-07-03 | 2011-11-16 | キヤノン株式会社 | データ管理システム |
-
2010
- 2010-03-31 JP JP2010081315A patent/JP2011215728A/ja active Pending
-
2011
- 2011-03-31 WO PCT/JP2011/058191 patent/WO2011125828A1/ja not_active Ceased
- 2011-03-31 CN CN2011800179995A patent/CN102834841A/zh active Pending
- 2011-03-31 US US13/635,106 patent/US20130004078A1/en not_active Abandoned
Patent Citations (2)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| JP2009098779A (ja) * | 2007-10-15 | 2009-05-07 | Fuji Xerox Co Ltd | 文書管理システム、文書管理装置および文書管理プログラム |
| JP2009187374A (ja) * | 2008-02-07 | 2009-08-20 | Toshiba Corp | 情報ライフサイクル管理システム、情報管理サーバ装置、電子媒体制御装置及びプログラム |
Non-Patent Citations (1)
| Title |
|---|
| SHINGO MIYAZAKI ET AL.: "Denshi Joho ya Kami ni Fukusei sare, Kakusan suru Joho no Shozai ya Life Cycle o Ichigen Kanri suru Joho Togyo Gijutsu inforester", TOSHIBA SOLUTION TECHNICAL NEWS 2009 NEN SHUKI-GO, vol. 19, 15 October 2009 (2009-10-15), pages 16 - 17 * |
Also Published As
| Publication number | Publication date |
|---|---|
| JP2011215728A (ja) | 2011-10-27 |
| CN102834841A (zh) | 2012-12-19 |
| US20130004078A1 (en) | 2013-01-03 |
Similar Documents
| Publication | Publication Date | Title |
|---|---|---|
| JP2011215728A (ja) | 書類管理システム、判定装置、データ出力制御装置、書類管理方法、書類管理プログラム | |
| CN102449650B (zh) | 文档管理支持系统、信息管理服务器装置以及信息介质控制装置 | |
| US8195713B2 (en) | Information life-cycle management system, information management server apparatus, electronic media control apparatus, and storage medium | |
| CN101364221B (zh) | 文档管理装置、文档管理系统和方法 | |
| US8402459B2 (en) | License management system, license management computer, license management method, and license management program embodied on computer readable medium | |
| US8370954B2 (en) | Content management systems and methods including content usage restrictions | |
| JP2005332401A (ja) | 情報処理方法、情報処理装置及びコンピュータ読出し可能な記憶媒体 | |
| JP2009224958A (ja) | 業務手順推定システム及びプログラム | |
| JP5012525B2 (ja) | セキュリティポリシーサーバ、セキュリティポリシー管理システム及びセキュリティポリシー管理プログラム | |
| US20110085194A1 (en) | Log information process device, image formation apparatis, and log information processing method | |
| US20060047731A1 (en) | Document-management device, document-management program, recording medium, and document-management method | |
| US8675216B2 (en) | Selective duplicating system and information management server device | |
| JP4980840B2 (ja) | 情報処理装置及び情報処理方法 | |
| US7574498B2 (en) | Device identification information managing system and method for communicably connecting between a network device and a device managing terminal unit that manages the network device | |
| CN1979548A (zh) | 工作流管理系统、方法和存储介质 | |
| US8599397B2 (en) | Access control system, apparatus, and program | |
| US20090307782A1 (en) | Document management system, document management method and computer program | |
| US20070198487A1 (en) | Document management system and document management method | |
| US20110106753A1 (en) | Document managing system | |
| JP5347844B2 (ja) | 文書管理システム及びプログラム | |
| US20070214185A1 (en) | Document management system, method and program therefor | |
| JP5851962B2 (ja) | 中継サーバ | |
| US20080155259A1 (en) | Computer readable medium storing electronic document processing program, electronic document processing system, key information recording system, document storage system and electronic document processing method | |
| JP4992731B2 (ja) | 文書管理装置、文書管理システム、及びプログラム | |
| CN104145275B (zh) | 复合媒体管理系统、信息管理服务器装置、复合利用制约制作装置及程序 |
Legal Events
| Date | Code | Title | Description |
|---|---|---|---|
| WWE | Wipo information: entry into national phase |
Ref document number: 201180017999.5 Country of ref document: CN |
|
| 121 | Ep: the epo has been informed by wipo that ep was designated in this application |
Ref document number: 11765728 Country of ref document: EP Kind code of ref document: A1 |
|
| WWE | Wipo information: entry into national phase |
Ref document number: 13635106 Country of ref document: US |
|
| WWE | Wipo information: entry into national phase |
Ref document number: 8290/DELNP/2012 Country of ref document: IN |
|
| NENP | Non-entry into the national phase |
Ref country code: DE |
|
| 122 | Ep: pct application non-entry in european phase |
Ref document number: 11765728 Country of ref document: EP Kind code of ref document: A1 |