WO2016048784A1 - Anonymous identity-based cryptosystems - Google Patents
Anonymous identity-based cryptosystems Download PDFInfo
- Publication number
- WO2016048784A1 WO2016048784A1 PCT/US2015/050670 US2015050670W WO2016048784A1 WO 2016048784 A1 WO2016048784 A1 WO 2016048784A1 US 2015050670 W US2015050670 W US 2015050670W WO 2016048784 A1 WO2016048784 A1 WO 2016048784A1
- Authority
- WO
- WIPO (PCT)
- Prior art keywords
- mod
- identity
- setting
- message
- ciphertext
- Prior art date
- Legal status (The legal status is an assumption and is not a legal conclusion. Google has not performed a legal analysis and makes no representation as to the accuracy of the status listed.)
- Ceased
Links
Classifications
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04L—TRANSMISSION OF DIGITAL INFORMATION, e.g. TELEGRAPHIC COMMUNICATION
- H04L9/00—Cryptographic mechanisms or cryptographic arrangements for secret or secure communications; Network security protocols
- H04L9/08—Key distribution or management, e.g. generation, sharing or updating, of cryptographic keys or passwords
- H04L9/0816—Key establishment, i.e. cryptographic processes or cryptographic protocols whereby a shared secret becomes available to two or more parties, for subsequent use
- H04L9/0838—Key agreement, i.e. key establishment technique in which a shared key is derived by parties as a function of information contributed by, or associated with, each of these
- H04L9/0847—Key agreement, i.e. key establishment technique in which a shared key is derived by parties as a function of information contributed by, or associated with, each of these involving identity based encryption [IBE] schemes
Definitions
- the present principles relate to cryptography, and more specifically, to anonymous identity-based encryption (IBE) systems.
- IBE anonymous identity-based encryption
- Identity-based cryptography is an extension of the public -key paradigm which was first put forward by Shamir [19].
- a major issue with public-key cryptography is the management of trust.
- Another issue to be dealt with is to recover the public key and companion certificate, check them, and then only encrypt and send messages.
- Identity-based cryptography aims at solving these practical issues by simplifying the key management.
- the setup algorithm SETUP 310 is a randomized algorithm that takes on input some security parameter ⁇ and outputs the system parameters mp k together
- the key derivation algorithm EXTRACT takes on input an identity id and master secret key msk and returns a secret key for the user with identity id : usk ⁇ - EXTRACT msk (id) .
- ENCRYPT 330 is a randomized algorithm that takes on input an identity id and a plaintext m G M , and returns a ciphertext C.
- the decryption algorithm DECRYPT 340 takes on input secret key usk (corresponding to identity id) and ciphertext C and returns the corresponding plaintext m or a special symbol 1 indicating that the ciphertext is invalid.
- usk corresponding to identity id
- ciphertext C returns the corresponding plaintext m or a special symbol 1 indicating that the ciphertext is invalid.
- DECRYPT usk ENCRYPT mpk (id, m)
- DECRYPT usk ENCRYPT mpk (id, m)
- algorithm ⁇ issues private-key extraction queries id 1( id ni and receives back the private key uskj corresponding to identity ⁇ (. usk j ⁇ - EXTRACT msk (id j ). The queries may be asked adaptively.
- the adversary decides no to make further oracle queries, it outputs a challenge identity id* (with id* ⁇ id; , 1 ⁇ i ⁇ 3 ⁇ 4), two (different) equal-size messages m 0 and m 1 G M , and some state information s.
- algorithm ⁇ 2 receives a challenge ciphertext C which is the encryption of m b for identity id* and where b is chosen at random in ⁇ 0,1 ⁇
- Algorithm ⁇ 2 can issue more private -key extraction queries id ni +i ⁇ ⁇ ⁇ idn 2 ; tne on ly restriction is that idj ⁇ id*, n ⁇ i ⁇ n 2 .
- the goal of ⁇ A 2 is to recover the value of b from 5 and C.
- An IBE scheme is said semantically secure (or indistinguishable) if
- Adversary A (A lt A 2 ) can encrypt any message of its choice for any identity.
- the adversary can mount chosen-identity, chosen-plaintext attacks (I D- CPA).
- I D- CPA chosen-plaintext attacks
- algorithm 1 algorithm 1 issues private -key extraction queries id 1( ... , id ni and receives back the private key usk j corresponding to identity id; : uskj ⁇ - EXTRACT msk (idj) .
- the queries may be asked adaptively.
- the adversary decides not to make further oracle queries, it outputs two (different) challenge identities id*, and id ⁇ (with id*,, id ⁇ idj , 1 ⁇ i ⁇ 3 ⁇ 4), a message m G M , and some state information s.
- algorithm A 2 receives a challenge ciphertext C which is the encryption of m for identity id*, and where b is chosen at random in ⁇ 0,1 ⁇
- Algorithm ⁇ A 2 can issue more private -key extraction queries id ni +i ⁇ ⁇ ⁇ idn 2 ; tne on ly restriction is that id; ⁇ id * ,, id ⁇ , n ⁇ i ⁇ n 2 .
- the goal of ⁇ 2 is to recover the value of b from 5 and C.
- An IBE scheme is said anonymous (ANO) if
- An IBE scheme is ANO-I N D-I D-CPA if it is I N D- I D- CPA and if is negligible in the security parameter for any polynomial-time adversary ⁇ ; the probability is taken over the random coins of the experiment according to the distribution induced by SETUP and over the random coins of the adversary.
- the difference is that a random message r is encrypted as opposed to the message m chosen by ⁇ ; the only restriction being that r and m must be of equal length.
- N pq be the product of two (odd) primes p and q.
- the Jacobi symbol modulo N of an integer a is denoted by 7 w (a).
- Q N is a subset of J N .
- Random oracle model is an idealized model introduced by Bellare and Rogaway [6] to analyze the security of certain cryptographic constructions using hash functions.
- the random oracle model assumes that the output of a hash function behaves as the output of a random generator.
- map yields a homomorphism from T p to G p .
- ⁇ ( ⁇ ) ⁇ .
- T p multiplicatively and use ⁇ to denote its group law.
- the group (T p ) 2 has (p— l)/2 elements.
- the present invention recognizes the need to improve the existing systems and methods for implementing crytosystems and methods, especially anonymous cryptosystems and methods.
- a method for communicating a message m comprising:
- N is a composite integer
- u G N ⁇ Q W , 5 is a bit-string
- ⁇ is a cryptographic hash function mapping bit-strings to elements of N
- ⁇ Q ld ⁇ is a family of functions mapping bit-strings to elements of a subset of ⁇ / ⁇ , namely 6 id : ⁇ 0,l ⁇ * ⁇ TLINTL.
- a method for processing a ciphertext comprising:
- N is a composite integer
- ff id ⁇ (id), t, t G ( ⁇ / ⁇ ) ⁇
- public system parameters mpk ⁇ N, u, ⁇ , ⁇ i d ⁇ , s]
- N is a composite integer
- u G N ⁇ Q W , 5 is bit- string
- ⁇ is a cryptographic hash function mapping bit-strings to elements of N and ⁇ £ /iC
- ⁇ is a family of functions mapping bit-strings to elements of a subset of ⁇ / ⁇ , namely £ id : ⁇ 0,1 ⁇ * ⁇ /N
- an apparatus for communicating a message m, comprising:
- an apparatus for processing a ciphertext, comprising:
- N is a composite integer
- ff id (id), t, i G ( ⁇ / ⁇ ) ⁇
- d Q ⁇ d (s)
- c c ⁇ 1 ⁇
- c c ⁇ 2 ⁇ for random bits ⁇ 1 , ⁇ 2 £ ⁇ 0,1 ⁇
- public system parameters mpk ⁇ N, u, ⁇ , ⁇ Q d ⁇ , s]
- N is a composite integer
- u £ J JV ⁇ Qffi M , 5 bit- string
- ⁇ is a cryptographic hash function mapping bit-strings to elements of N
- N is a composite integer
- ff id ⁇ (id), t, i G ( ⁇ / ⁇ ) ⁇
- d Q id (s)
- c c (/3l)
- c c ⁇ 2 ⁇ for random bits ⁇ 1 , ⁇ 2 £ ⁇ 0,1 ⁇ , comprising:
- N is a composite integer
- u G N ⁇ Q W , 5 is a bit-string
- ⁇ is a cryptographic hash function mapping bit-strings to elements of N
- ⁇ Q ld ⁇ is a family of functions mapping bit-strings to elements of a subset of ⁇ / ⁇ , namely 6 id : ⁇ 0,l ⁇ * ⁇ TLINTL.
- N is a composite integer
- ff id ⁇ (id), t, i G ( ⁇ / ⁇ ) ⁇
- d Q id (s)
- c c (/3l)
- c c ⁇ 2 ⁇ for random bits ?i, ? 2 £ ⁇ 0 ⁇ 1 ⁇
- FIGS. 1 to 3 show exemplary apparatus according to the present principles
- FIGS. 4 to 6 show exemplary processes according to the present principles.
- the examples set out herein illustrate exemplary embodiments of the invention. Such examples are not to be construed as limiting the scope of the invention in any manner.
- the recipient in a transmission needs to be kept anonymous. This allows users to maintain some privacy. Protecting communication content may be not enough, as already observed in a couple of papers (e.g., [4,5, 17]).
- the cryptosystem by Clear et al. produces somewhat long ciphertexts.
- the goal of the present principles is to provide anonymous identity-based cryptosystems with much shorter ciphertexts.
- the resulting ciphertexts are twice shorter, improving all previous anonymous IBEs based on the quadratic residuosity. Extra useful properties offered by the proposed cryptosystems are listed later.
- T p ⁇ u ⁇ u G W p ⁇ ⁇ 5 ⁇ U ⁇
- this group can be defined by
- parameter d is derived from the system parameters and/or the identity of the recipient.
- the encryption algorithm can randomly draw t, i G ⁇ / ⁇ .
- Proposition 2 The scheme is I N D-I D-CPA under the quadratic residuosity assumption in the random oracle model.
- Proposition 3 The scheme is AN 0-1 D-CPA under the quadratic residuosity assumption in the random oracle model.
- ⁇ a cryptographic hash function mapping bit-strings to elements of N (i.e., ⁇ : ⁇ 0,1 ⁇ * ⁇ Jw)
- the decryption algorithm can evaluate ⁇ as
- d the smallest nonnegative integer
- Remark 9 In order to have short system parameters mpk, it may be advantageous to select a small value for d.
- N pq where p and q are prime and p ⁇ —q (mod 4) . It also generates a random element u G N ⁇ Q W .
- PEKS public key encryption with keyword search
- FIG. 1 illustrates a block diagram of an exemplary system in which various aspects of the exemplary embodiments of the present principles may be implemented.
- System 100 may be embodied as a device including the various components described below and is configured to perform the processes described above. Examples of such devices, include, but are not limited to, personal computers, laptop computers, smartphones, tablet computers, digital multimedia set top boxes, digital television receivers, personal video recording systems, connected home appliances, and servers.
- System 100 may be communicatively coupled to other similar systems, and to trusted third parties via a communication channel as shown in Figure 2 and as known by those skilled in the art to implement the exemplary cryptosystems described above.
- the system 100 may include at least one processor 110 configured to execute instructions loaded therein for implementing the various processes as discussed above.
- Processor 110 may include embedded memory, input output interface and various other circuitries as known in the art.
- the system 100 may also include at least one memory 120 (e.g., a volatile memory device, a non-volatile memory device).
- System 100 may additionally include a storage device 140, which may include nonvolatile memory, including, but not limited to, EEPROM, ROM, PROM, RAM, DRAM, SRAM, flash, magnetic disk drive, and/or optical disk drive.
- the storage device 140 may comprise an internal storage device, an attached storage device and/or a network accessible storage device, as non-limiting examples.
- System 100 may also include an encryption/decryption module 130 configured to process data to provide an encrypted message or decrypted message.
- Encryption/decryption module 130 represents the module(s) that may be included in a device to perform the encryption and/or decryption functions.
- a device may include one or both of the encryption and decryption modules, for example, encryption may be done on a regular PC since encryption does not involve secret key so that the PC need not include secure memory for storing the input parameters (i.e., the public system parameters and the user's identity).
- Decryption however, requires secret keys (i.e., the decryption key) and is done in a secure device, for example a smart card. As memory is expensive on smart card, the encryption functionality may not always be provided on a smart card.
- encryption and/or decryption may be performed using shared resources as known to those skilled in the art. Additionally, encryption/decryption module 130 may be implemented as a separate element of system 100 or may be incorporated within processors 110 as a combination of hardware and software as known to those skilled in the art.
- Program code to be loaded onto processors 110 to perform the various processes described hereinabove may be stored in storage device 140 and
- processors 110 may store one or more of the various items during the performance of the processes discussed herein above, including, but not limited to a public system parameters, a private key, encrypted messages, equations, formula, matrices, variables, operations, and operational logic.
- the system 100 may also include communication interface 150 that enables communication with other devices via communication channel 160.
- the system 100 may also include communication interface 150 that enables communication with other devices via communication channel 160.
- communication interface 150 may include, but is not limited to a transceiver configured to transmit and receive data from communication channel 160.
- the communication interface may include, but is not limited to, a modem or network card and the communication channel may be implemented within a wired and/or wireless medium.
- the various components of system 100 may be connected or
- one or more of the above-identified components may receive and/or store the information (e.g., to be encrypted) and/or the ciphertext (e.g., to be decrypted, to be operated on homomorphically, resulting from encryption).
- the above-identified components may receive and/or store the encryption function(s) and/or the decryption function(s), as described herein above.
- the exemplary embodiments of this invention may be carried out by computer software implemented by the processor 110 or by hardware, or by a combination of hardware and software.
- the exemplary embodiments of this invention may be implemented by one or more integrated circuits.
- the memory 120 may be of any type appropriate to the technical environment and may be implemented using any appropriate data storage technology, such as optical memory devices, magnetic memory devices, semiconductor-based memory devices, fixed memory and removable memory, as non-limiting examples.
- the processor 110 may be of any type appropriate to the technical environment, and may encompass one or more of microprocessors, general purpose computers, special purpose computers and processors based on a multi-core architecture, as non-limiting examples.
- FIG. 2 illustrates an arrangement wherein data is exchanged between two terminals 210 and 220 in accordance with the present principles.
- Each of the terminals 210 and 220 include encryptor/decryptor modules 230 and 240, respectively, and may additionally include each of the other components of system 100 described above, as appropriate.
- Terminals 210 and 220 are communicatively coupled to each other via communication channel 250, which may be implemented via wired and/or wireless medium.
- arrangement 200 may include a trusted third party 260 communicatively coupled to terminals 210 and 220, wherein third party 260 may in some cases, among other things, generate common parameters and the keys, distribute them to the terminals, and/or generate common keys in a manner known to those skilled in the art.
- the setup algorithm is performed by the trusted third party to generate, among other things, the master secret key.
- a message can be encrypted and decrypted by the terminals as described above, and transmitted and received via communication channel 250.
- Figure 3 illustrates a generalized flow diagram of an identity-based cryptosystem.
- Figures 4 to 6 show exemplary flow charts according to the present principles.
- the flow charts illustrate the anonymous identity-based crypto processes discussed above.
- the processes of Figures 4 - 6 may be executed by e.g., a processor 110 of Figure 1.
- the processes may represent, e.g., computer program products having the computer-executable instructions which may be stored in non-transitory computer- readable storage media 120 of Figure 1 as described before.
- the embodiments described herein may be implemented in, for example, a method or a process, an apparatus, a software program, a data stream, or a signal. Even if only discussed in the context of a single form of implementation (for example, discussed only as a method), the implementation of features discussed above may also be implemented in other forms (for example, an apparatus or program).
- An apparatus may be implemented in, for example, appropriate hardware, software, and firmware.
- the methods may be implemented in, for example, an apparatus such as, for example, a processor, which refers to processing devices in general, including, for example, a computer, a microprocessor, an integrated circuit, or a programmable logic device. Processors also include communication devices, such as, for example, computers, cell phones, portable/personal digital assistants ("PDAs”), and other devices that facilitate communication of information between end-users.
- PDAs portable/personal digital assistants
- the appearances of the phrase “in one embodiment” or “in an embodiment” or “in one implementation” or “in an implementation”, as well any other variations, appearing in various places throughout the specification are not necessarily all referring to the same embodiment.
- Determining the information may include one or more of, for example, estimating the information, calculating the information, predicting the information, or retrieving the information from memory.
- Accessing the information may include one or more of, for example, receiving the information, retrieving the information (for example, from memory), storing the information, processing the information, transmitting the information, moving the information, copying the information, erasing the information, calculating the information, determining the information, predicting the information, or estimating the information.
- Receiving is, as with “accessing”, intended to be a broad term.
- Receiving the information may include one or more of, for example, accessing the information, or retrieving the information (for example, from memory).
- “receiving” is typically involved, in one way or another, during operations such as, for example, storing the information, processing the information, transmitting the information, moving the information, copying the information, erasing the information, calculating the information, determining the information, predicting the information, or estimating the information.
- implementations may produce a variety of signals formatted to carry information that may be, for example, stored or transmitted.
- the information may include, for example, instructions for performing a method, or data produced by one of the described embodiments.
- a signal may be formatted to carry the bitstream of a described embodiment.
- Such a signal may be formatted, for example, as an electromagnetic wave (for example, using a radio frequency portion of spectrum) or as a baseband signal.
- the formatting may include, for example, encoding a data stream and modulating a carrier with the encoded data stream.
- the information that the signal carries may be, for example, analog or digital information.
- the signal may be transmitted over a variety of different wired and/or wireless links, as is known.
- the signal may be stored on a processor-readable medium.
Landscapes
- Engineering & Computer Science (AREA)
- Computer Security & Cryptography (AREA)
- Computer Networks & Wireless Communication (AREA)
- Signal Processing (AREA)
- Storage Device Security (AREA)
Abstract
The present principles relate to several new identity-based cryptosystems. Notably, the cryptosystems are anonymous, that is, the ciphertexts reveal nothing about the recipient's identity. The ciphertexts are also twice shorter than the best known scheme. Further, the proposed cryptosystems come with strong security guarantees: they are proved to be semantically secure under the standard quadratic residuosity assumption, in the random oracle model. Anonymous identity-based schemes are important cryptographic tools as they constitute the central building block for public-key encryption with keyword search (a.k.a. PEKS).
Description
ANONYMOUS IDENTITY-BASED CRYPTOSYSTEMS
RELATED APPLICATION
This patent application claims the benefit of U.S. Provisional Application No. 62/098391 filed on December 31, 2014, U.S. Provisional Application No. 62/055731 filed on September 26, 2014 both with the same title, and the disclosure of which is incorporated by reference herein in its entirety.
Field of the Invention
The present principles relate to cryptography, and more specifically, to anonymous identity-based encryption (IBE) systems.
Background Information
This section is intended to introduce the reader to various aspects of art, which may be related to various aspects of the present invention that are described and/or claimed below. This discussion is believed to be helpful in providing the reader with background information to facilitate a better understanding of the various aspects of the present invention. Accordingly, it should be understood that these statements are to be read in this light, and not as admissions of prior art.
Referenced Documents
[1] Michel Abdalla, Mihir Bellare, Dario Catalano, Eike Kiltz, Tadayoshi Kohno, Tanja Lange, John Malone-Lee, Gregory Neven, Pascal Paillier, and Haixia Shi. Searchable encryption revisited: Consistency properties, relation to anonymous IBE, and extensions. In V. Shoup, editor, Advances in Cryptology— CRYPTO 2005, volume 3621 of Lecture Notes in Computer Science, pages 205-222. Springer, 2005.
[2] Michel Abdalla, Mihir Bellare, Dario Catalano, Eike Kiltz, Tadayoshi Kohno, Tanja Lange, John Malone-Lee, Gregory Neven, Pascal Paillier, and Haixia Shi. Searchable encryption revisited: Consistency properties, relation to anonymous IBE, and extensions. /. Cryptology, 21(3):350-391, 2008. An extended abstract appears in [1].
[3] Giuseppe Ateniese and Paolo Gasti. Universally anonymous IBE based on the quadratic residuosity assumption. In M. Fischlin, editor, Topics in Cryptology— CT-RSA 2009, volume 5473 of Lecture Notes in Computer Science, pages 32-47.
Springer, 2009.
[4] Adam Barth, Dan Boneh, and Brent Waters. Privacy in encrypted content distribution using private broadcast encryption. In G. Di Crescenzo and A.D. Rubin, editors, Financial Cryptography and Data Security, volume 4107 of Lecture Notes in Computer Science, pages 52-64. Springer, 2006.
[5] Mihir Bellare, Alexandra Boldyreva, Anand Desai, and David Pointcheval. Key-privacy in public-key encryption. In C. Boyd, editor, Advances in Cryptology— ASIACRYPT 2001 , volume 2248 of Lecture Notes in Computer Science, pages 566-582. Springer, 2001.
[6] Mihir Bellare and Phillip Rogaway. Random oracles are practical: A paradigm for designing efficient protocols. In st ACM Conference on Computer and Communications Security, pages 62-73. ACM Press, 1993.
[7] Dan Boneh, Giovanni Di Crescenzo, Rafail Ostrovsky, and Giuseppe Persiano. Public key encryption with keyword search. In C. Cachin and J. Camenisch, editors, Advances in Cryptology — EUROCRYPT 2004, volume 3027 of Lecture Notes in Computer Science, pages 506-522. Springer, 2004.
[8] Dan Boneh and Matthew K. Franklin. Identity-based encryption from the Weil pairing. SIAM J. CompuL , 32(3):586-615, 2003.
[9] Dan Boneh, Craig Gentry, and Michael Hamburg. Space-efficient identity based encryption without pairings. In th Annual IEEE Symposium on Foundations of Computer Science (FOCS 2007), pages 647-657. IEEE Computer Society, 2007.
[10] Michael Clear, Hitesh Tewari, and Ciaran McGoldrick. Anonymous IBE from quadratic residuosity with improved performance. In D. Pointcheval and D. Vergnaud, editors, Progress in Cryptology - AFRICACRYPT 2014, volume 8469 of Lecture Notes in Computer Science, pages 377-397. Springer, 2014.
[11] Giovanni Di Crescenzo and Vishal Saras wat. Public key encryption with searchable keywords based on Jacobi symbols. In K. Srinathan, CP. Rangan, and M. Yung, editors, Progress in Cryptology - INDOCRYPT 2007, volume 4859 of Lecture Notes in Computer Science, pages 282-296. Springer, 2007.
[12] Shafi Goldwasser and Silvio Micali. Probabilistic encryption. /. Comput.
Syst. Sci., 28(2):270-299, 1984.
[13] Shai Halevi. A sufficient condition for key -privacy. IACR Cryptology ePrint Archive, Report 2005/005, 2005. http://eprint.iacr.org/.
[14] Marc Joye. U.S. Provisional Application No. 62/055722 filed on September 26, 2014, titled "Key-private Cryptosystems Based on the Quadratic Residuosity."
[15] Marc Joye. U.S. Provisional Application No. 62/055729 filed on September 26, 2014, titled "Identity-based XOR homomorphic cryptosystems."
[16] Marc Joye and Gregory Neven, editors. Identity-Based Cryptography, volume 2 of Cryptology and Information Security Series. IOS Press, 2009.
[17] Aggelos Kiayias, Yiannis Tsiounis, and Moti Yung. Group encryption. In K. Kurosawa, editor, Advances in Cryptology— ASIACRYPT 2007 , volume 4833 of Lecture Notes in Computer Science, pages 181-199. Springer, 2007.
[18] Karl Rubin and Alice Silverberg. Compression in finite fields and torus- based cryptography. SIAM J. Comput , 37(5): 1401-1428, 2008.
[19] Adi Shamir. Identity-based cryptosystems and signature schemes. In G. R. Blakley and D. Chaum, editors, Advances in Cryptology, Proceedings of CRYPTO '84, volume 196 of Lecture Notes in Computer Science, pages 47-53. Springer, 1985.
Identity-based encryption
Identity-based cryptography is an extension of the public -key paradigm which was first put forward by Shamir [19]. A major issue with public-key cryptography is the management of trust. Another issue to be dealt with is to recover the public key and companion certificate, check them, and then only encrypt and send messages. We refer the reader to the excellent introduction [16] by Joux for details. Identity-based cryptography aims at solving these practical issues by simplifying the key management.
Formally, we define an identity-based encryption scheme [8] (or IBE in short) as a tuple of four algorithms (SETUP, EXTRACT, ENCRYPT, DECRYPT). The generalized flow diagram of the process is illustrated as process 300 in Figure 3.
Setup The setup algorithm SETUP 310 is a randomized algorithm that takes on input some security parameter κ and outputs the system parameters mp k together
R
with the master secret key msk: (m pk, msk) <- SETUP(1K).
Key derivation The key derivation algorithm EXTRACT , or Key Derivation 320, takes on input an identity id and master secret key msk and returns a secret key for the user with identity id : usk <- EXTRACTmsk(id) .
Encryption Let M denote the message space. The encryption algorithm ENCRYPT 330 is a randomized algorithm that takes on input an identity id and a plaintext m G M , and returns a ciphertext C. We write C <- ENCRYPTmpk(id, m) .
Decryption The decryption algorithm DECRYPT 340 takes on input secret key usk (corresponding to identity id) and ciphertext C and returns the corresponding plaintext m or a special symbol 1 indicating that the ciphertext is invalid. We write m - DECRYPTusk(C) if C is a valid ciphertext and ± - DECRYPTusk(C) if it is not.
We require that, with non-negligible probability, DECRYPTusk(ENCRYPTmpk(id, m)) = m for all messages m E M. The specific processes associated with each of these steps as they relate to the present principles is described in further detail below.
Security notions
Indistinguishability (IND) of encryptions
The notion of indistinguishability of encryptions [12] captures a strong notion of data-privacy: The adversary should not learn any information whatsoever about a plaintext given its encryption beyond the length of the plaintext. The definitions for the public -key setting naturally extend to the identity-based paradigm. The standard definition is strengthened by allowing the adversary to issue chosen private-key extraction queries [8].
We view an adversary Λ as a pair (·Λ1, ·Λ2) of probabilistic algorithms. This corresponds to adversary Λ running in two stages. Upon receiving the system parameters m pk, in the "find" stage, algorithm Λ issues private-key extraction queries id1( idni and receives back the private key uskj corresponding to identity \ά(. uskj <- EXTRACTmsk(idj). The queries may be asked adaptively. Once the adversary decides no to make further oracle queries, it outputs a challenge identity id* (with id*≠ id; , 1 < i < ¾), two (different) equal-size messages m0 and m1 G M , and some state information s. In the "guess" stage, algorithm ·Λ2 receives a challenge ciphertext C which is the encryption of mb for identity id* and where b is chosen at random in {0,1}· Algorithm ·Λ2 can issue more private -key extraction queries
idni+i<■■■< idn2 ; tne only restriction is that idj≠ id*, n < i < n2. The goal of <A2 is to recover the value of b from 5 and C.
An IBE scheme is said semantically secure (or indistinguishable) if
(m pk, msk) <- SETUP(1K),
r /| EXTRACTmsk(-) /- EXTRACTmsk( ) f Γ ,
Pr (id , m0, m1, s <- C Z1 msK (m pk),: c/Z2 msK (s, C) = b
[b ^ {0,1}, C <- ENCRYPTmpk(id*, m¾)
is negligible in the security parameter for any polynomial-time adversary A ; the probability is taken over the random coins of the experiment according to the distribution induced by SETUP and over the random coins of the adversary.
Adversary A = (Alt A2) can encrypt any message of its choice for any identity. In other words, the adversary can mount chosen-identity, chosen-plaintext attacks (I D- CPA). Hence, we write I N D- I D- CPA the security notion achieved by a semantically secure identity-based encryption scheme.
Remark 1. As messages m0 and m1 are supposed to be different, when the message space is M = {0,1}, the previous relation simplifies to
(m pk, msk) <- SETUP(1K),
EXTRACTmsk( ) . EXTRACW.) (S) C) = &
Pr (id*, s) <- A (m pk),
b <- {0,1}, C <- ENCRYPTmpk(id*, b) Anonymity Analogously, the notion of anonymity captures a strong requirement about privacy: a ciphertext should not reveal the identity of the recipient. More formally, it is defined as a straightforward adaptation of key privacy [5] to the identity-based paradigm [2].
As before, we view an adversary A as a pair (·Α1, ·Α2) of probabilistic algorithms. In the "find" stage, algorithm 1 algorithm 1 issues private -key extraction queries id1( ... , idni and receives back the private key uskj corresponding to identity id; : uskj <- EXTRACTmsk(idj) . The queries may be asked adaptively. Once the adversary decides not to make further oracle queries, it outputs two (different) challenge identities id*, and id^ (with id*,, id^≠ idj , 1 < i < ¾), a message m G M , and some state information s. In the "guess" stage, algorithm A2 receives a challenge ciphertext C which is the encryption of m for identity id*, and where b is chosen at
random in {0,1}· Algorithm <A2 can issue more private -key extraction queries idni+i<■■■< idn2 ; tne only restriction is that id;≠ id*,, id^, n < i < n2. The goal of Λ2 is to recover the value of b from 5 and C.
An IBE scheme is said anonymous (ANO) if
(mpk, msk) ^ SETUP(1K),
Pr (id*0, idi, m, s) <- ^x™CTmski m k) . ^x CTms i s, C = b
lb <- {0,1}, C <- ENCRYPTmpk(id*„ m)
is negligible in the security parameter for any polynomial-time adversary Λ; the probability is taken over the random coins of the experiment according to the distribution induced by SETUP and over the random coins of the adversary. We write ANO-I D-CPA the corresponding security notion achieved by an anonymous IBE.
Of course, the goals of indistinguishability and anonymity can be combined to give rise to the ANO-I N D-I D-CPA security notion. Halevi's sufficient condition [13] was extended to IBE schemes in [2]. An IBE scheme is ANO-I N D-I D-CPA if it is I N D- I D- CPA and if
 is negligible in the security parameter for any polynomial-time adversary Λ; the probability is taken over the random coins of the experiment according to the distribution induced by SETUP and over the random coins of the adversary. The difference is that a random message r is encrypted as opposed to the message m chosen by Λ ; the only restriction being that r and m must be of equal length. When the message space is M = {0,1}, the above relation simplifies to
(mpk, msk) <- SETUP(1K),
. EXTRACW.)(S)C) = &
Pr (id* 0, id*, 5) <- c/z TRACW0(mpk),
b {0,1}, r 2- {0,1}, C <- ENCRYPTmpk(id , r)
Complexity assumptions
It is useful to introduce some notation. Let N = pq be the product of two (odd) primes p and q. The Jacobi symbol modulo N of an integer a is denoted by 7w(a). The set of integers whose Jacobi symbol is 1 is denoted by N, N = {a G ΈΝ* \]Ν ά) = 1); the set of quadratic residues is denoted by QMW, QMW = {a G ¾Ι/ρ(α) = Jq(a) = 1}· Note that Q N is a subset of JN.
Definition 1 (Quadratic Residuosity Assumption). Let RSAGen be a probabilistic algorithm which, given a security parameter κ, outputs primes p and q and their product N = pq. The Quadratic Residuosity (QR) assumption asserts that the success probability defined as the distance
Pr[V(x,N) = l\x -QRN] -Pr[V(x,N) = l\x^ N\QRN] is negligible for any probabilistic polynomial-time distinguisher D; the probabilities are taken over the experiment of running (N,p,q) <- RSAGen (1K) and choosing at random x G Q N and x G JN \ Q N.
Random oracle model The random oracle model is an idealized model introduced by Bellare and Rogaway [6] to analyze the security of certain cryptographic constructions using hash functions. Informally, the random oracle model assumes that the output of a hash function behaves as the output of a random generator.
The group Τνγ x (Tq)2
Let p be an odd prime, let Δ G IFp x, and let δ2 = A. Define the multiplicative group
Gp = {x + 8y\x,y G Wp and x2 — Ay2 = 1).
Where it is defined, consider the map
u + δ
ψ Ψν→ Gv,u To ease the notation, we augment Wp with a special symbol∞ and define ψ(∞) = \. There are two cases to distinguish:
1. If δ £ Wp then Gp = G IFp U {∞}}—see [18];
2. If δ G IFp then Gp =
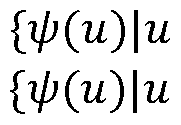 G IFp U {∞}, u≠ ±δ}.
(Observe that 0 ί Gp when δ G IFp.)
We are interested in the second case. From now on, we will suppose that δ G IFp x and thus that Δ G QRp. For convenience, we write Tp = Wp \ {±£}) U
{∞). We so have Gp = ψ(Τρ). Clearly, map ψ: Tp→ Gp is injective and thus defines a bijection. Indeed, suppose τ/>(«ι) = ( 2) for some ultu2 Tp. This implies (i½ + δ) (u2— δ) = (u2 + δ) (ΜΧ— δ) and in turn u = u2. The inverse map is given by^ ^G^ ^V H— .
Furthermore, map
 yields a homomorphism from Tp to Gp. We have ψ(∞) = \. Let

Consequently, Tp endows a group structure. Its order is #Tp = p— 1. We write Tp multiplicatively and use © to denote its group law. We have:
• the neutral element is 00 :
u®∞=∞®u=u for all u G Tp; the inverse of u G Tp \ {∞) is— u:
u © (— u) = (— u) © u
• given ult u2 G Tp\ {∞), their multiplication is given by:
IU1U2 + A
if u-i≠—u2 ,
00 otherwise.
Remark that 0 is of order 2 as an element of Tp, namely 0 © 0 = 00. Remark also that for u G Tp, u≠ 0, 00, we have u © 0 = A/u.
Let ( p)2 c Tp represent the subgroup of squares in Tp:

The group (Tp)2 has (p— l)/2 elements.
Let u1,u2 Tp. Define w1 =u1®u1 and w2 =w2 ©w2. Then letting u3: = ux © u2 we get:
w3 : = w1 © w2
= (u ® u ) ® (u2 ® u2) = (u ® u2) ® (u ® u2) = u3 ® u3.
Further, for any 1 < i < 3, if wt ≠ 00 then
(ui ± δ)2
2W; ± 2δ = , ,1
Ui (!) and thus 7p(2wj ± 25) = Jp(Ui).
The previous setting naturally extends through Chinese remaindering. Let N = pq be an RSA (Rivest-Shamir-Adleman) modulus. Then (Tp)2 x (Tq)2 is a group and has order φ(Ν). SUMMARY OF THE INVENTION
The present invention recognizes the need to improve the existing systems and methods for implementing crytosystems and methods, especially anonymous cryptosystems and methods.
In accordance with an aspect of the present principles, a method for communicating a message m is presented, comprising:
accessing the message m;
accessing a user identity id and public system parameters mpk =
{N, u, Ή, {^iC|}, s], where N is a composite integer, u G N \ Q W, 5 is a bit-string, Ή is a cryptographic hash function mapping bit-strings to elements of N and {Qld} is a family of functions mapping bit-strings to elements of a subset of Έ/ΝΈ, namely 6id : {0,l}*→ TLINTL. s→d = Qld(s) such that JN (d2 - 4Jf(id)) = JN(d2 - uM (id)) = -1;
generating a ciphertext C = {ε, c, έ, c] of the message m using the user identity id, where ε = (-l)mJN(t), c(°> = t + mod N-
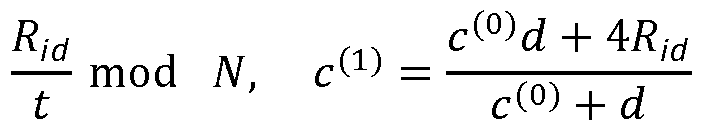
,ηΛ uRid ί c(0)d + 4uRid
ε = (-l)mJN(t), c(°' = t + - mod N, =— (0) mod N, where i?id = Ή (id) , t, i G (Έ/ΝΈ)Χ, d = gid (s), choosing random bits β1} β2 G {0,1} and setting c = c^1^ and c = c^2^; and
transmitting the ciphertext C = {ε, c, έ, c] to a device via a communication channel.
In accordance with another aspect of the present principles, a method for processing a ciphertext is presented, comprising:
receiving the ciphertext C = {ε, c, έ, c] for a user with an identity id via a communication channel; and
accessing the ciphertext C = {ε, c, έ, c] of a plaintext message m, where
c^d + 4Rjd
mod N, c(°) + d 1 uR, c^d + 4ui? id
£ = (-l)mJN(t), ci°) = t + ^ mod N, mod N, t c(°) + d
where N is a composite integer, ffid = Ή (id), t, t G (Έ/ΝΈ)Χ, d = Q-I( (s), c = (βι) ancj c = c^z) for random bits β1, β2 £ {0,1}, wherein public system parameters mpk = {N, u, Ή, {^id}, s], where N is a composite integer, u G N \ Q W, 5 is bit- string, Ή is a cryptographic hash function mapping bit-strings to elements of N and {£/iC|} is a family of functions mapping bit-strings to elements of a subset of Έ/ΝΈ, namely £id : {0,1}*→ /N , s■→ d = Qld (s) such that JN(d2 - 4Jf (id)) = JN(d2 - uM (id)) = -1 ;
generating the message m by accessing a private key usk = {rid} for a user with an identity id by following steps:
if r 2≡ ffid (mod N), setting v = ε, γ = c and Δ = ffid; otherwise
, where d = Qld(s ;

and
determining the message m as
1— v · τ
m
2
In accordance with another aspect of the present principles, a method is presented for generating keys for an identity-based cryptosystem wherein a private key is used to decrypt ciphertext C = {ε, c, έ, c] of a plaintext message m for a user with an identity id where
Rid c(0)d + 4ff/d
ε = (-l)m;w(t), c(°' = t +— mod N, c« = ^ mod N, t c^) + d
,ηΛ Rj t ... c^d + uRj t
e = {-l)mJN{i), c(°' = t + - mod N, c« = _(Q) rf mod N, where N is a composite integer, ff id = (id), t, t £ (Έ/ΝΈ)Χ, d = Qid(s), c = c(/3l) and c = c^2^ for random bits β , β2 G {0,1}, comprising steps of:
setting a master secret key msk; and
generating, using the master secret key msk, the private key usk = {rid} for a user with an identity id, using public system parameters mpk = {N,u,J ,{Qld},s}, where N is a composite integer, u G N \ Q W, 5 is bit-string, Ή is a cryptographic hash function mapping bit-strings to elements of N and {Qld} is a family of functions mapping bit-strings to elements of a subset of Έ/ΝΈ namely Qld: {0,1}*→ Έ/ΝΈ, s <→ d = GidO such that JN(d2 - \W (id)) = JN(d2 - 4u?f (id)) = -1.
In accordance with another aspect of the present principles, an apparatus is presented for communicating a message m, comprising:
a processor configured to access the message m, the processor further configured to access a user identity id and public system parameters mpk = {N, u, Ή, {£/iC|}, s], where N is a composite integer, ii £jw\ Q W, 5 is a bit-string, Ή is a cryptographic hash function mapping bit-strings to elements of N and [Qld] is a family of functions mapping bit-strings to elements of a subset of Έ/ΝΈ, namely 6id:{0,l}*→ Έ/ΝΈ,Ξ■→ d = Qld(s such that JN(d2 - 4Jf(id)) = JN d2 - uM (id)) = -1;
an encryptor configured to generate a ciphertext C = {ε, c, έ, c] of the message m using the user identity id, where
Rid c^d + 4Rid
ε = (-l)mJN(t), c(°' = t + - - mod N, c« = ,a mod N,
,ηΛ uRid ί c(0)d + 4uRid
ε = (-l)mJN(t), c(°' = t + - mod N, =— (0) mod N, where i?id = Ή (id), t, i G (Έ/ΝΈ)Χ, d = gid(s), choosing random bits β1}β2 G {0,1} and setting c = c^1^ and c = c^2^; and
a communication interface, coupled to a communication channel, configured to transmit the ciphertext C = {ε, c, έ, c] via the communication channel.
In accordance with another aspect of the present principles, an apparatus is presented for processing a ciphertext, comprising:
a communication interface, coupled to a communication channel, configured to receive the ciphertext C = {ε, c, έ, c] of a plaintext message m, where ε = (-l)m;w(t), c(°' = t + mod N,

£ = (-l)mJN(t), ci°) = t + ^ mod N, mod N, t c(°) + d
where N is a composite integer, ffid = (id), t, i G (Έ/ΝΈ)Χ, d = Q\d (s), c = c^1^ and c = c^2^ for random bits β1, β2 £ {0,1}, wherein public system parameters mpk = {N, u, Ή, {Q d}, s], where N is a composite integer, u £ JJV \ QffiM , 5 is bit- string, Ή is a cryptographic hash function mapping bit-strings to elements of N and [Qld] is a family of functions mapping bit-strings to elements of a subset of Έ/ΝΈ, namely 6id : {0,l}*→ /N , s■→ d = Qld (s) such that JN (d2 - 4Jf(id)) = JN(d2 - 4uJf(id)) = -1 ; and
the processor generates the plaintext message m by accessing a private key usk = {rid} for a user with an identity id by following steps:
if r 2≡ ffid (mod N), setting v = ε, γ = c and Δ = ffid; otherwise
, where d = Qld(s ;

and
determining the plaintext m as
1— v · τ
m
In accordance with another aspect of the present principles, an apparatus is presented for generating keys for an identity-based cryptosystem wherein a private key is used to decrypt ciphertext C = {ε, c, έ, c] of a plaintext message m for a user with an identity id where ε = (-l)m t), c(°' = t + mod N,

where N is a composite integer, ff id = Ή (id), t, i G (Έ/ΝΈ)Χ, d = Qid(s), c = c(/3l) and c = c^2^ for random bits β1, β2 £ {0,1}, comprising:
a processor configured to set a master secret key msk, and generate, using the master secret key msk, the private key usk = {rid} for a user with an identity id, using
public system parameters m pk = {N, u, Ή, s), where N is a composite integer, u G N \ Q W , 5 is bit-string, Ή is a cryptographic hash function mapping bit-strings to elements of N and {Qld} is a family of functions mapping bit-strings to elements of a subset of Έ/ΝΈ namely 6id : {0,l}*→ Έ/ΝΈ, Ξ >→ d = Qld (s such that JN (d2 - 4Jf(id)) = JN (d2 - πΉ(\ά)) = -1 ; and
a communication interface, coupled to a communication channel, configured to transmit the private key usk = {rid} via the communication channel. In accordance with another aspect of the present principles, a computer program product stored in non-transitory computer-readable storage media is presented, comprising computer-executable instructions for
accessing the message m;
accessing a user identity id and public system parameters mpk =
{N, u, Ή,
 s], where N is a composite integer, u G N \ Q W , 5 is a bit-string, Ή is a cryptographic hash function mapping bit-strings to elements of N and {Qld} is a family of functions mapping bit-strings to elements of a subset of Έ/ΝΈ, namely 6id : {0,l}*→ TLINTL. s→ d = Qld (s) such that JN (d2 - 4Jf(id)) = JN (d2 - AuK (id)) = -1;
generating a ciphertext C = {ε, c, έ, c] of the message m using the user identity id, where
R c^d + R
ε = (-l)m t), c(°' = t +— mod N, c<U = ^ mod N, t c^) + d ε = (-l)m JN (i), c(°' = t + mod N, = ^ mod N, t c^) + d
where ffid = (id) , t, t G (Έ/ΝΈ) , d = ld (s) , choosing random bits β1, β2 G {0,1} and setting c = c^1^ and c = c^2^ ; and
transmitting the ciphertext C = {ε, c, έ, c] to a device via a communication channel.
In accordance with another aspect of the present principles, a computer program product stored in non-transitory computer-readable storage media is presented, comprising computer-executable instructions for
receiving the ciphertext C = {ε, c, έ, c] for a user with an identity id via a communication channel; and
accessing the ciphertext C = {ε, c, έ, c] of a plaintext message m, where
,n, Rid , , c(0)d + 4Rid
ε = (-1Γ h(t), c<0> = t + -^ mod N, = g(0) rf mod N,
,ηΛ uRid c(0)d + 4uRid
ε = (-l)mJN(t), c(°' = t + - mod N, =— (0) mod N, where N is a composite integer, ffid = Ή (id), t, t ε (Έ/ΝΈ)Χ, d = Q\d (s), c = c^1^ and c = c^2^ for random bits β , β2 £ {0,1}, wherein public system parameters m pk = {N, u, Ή, {£/ jd }, s], where N is a composite integer, u G N \ Q W, 5 is bit- string, Ή is a cryptographic hash function mapping bit-strings to elements of N and {£/id} is a family of functions mapping bit-strings to elements of a subset of Έ/ΝΈ, namely £id : {0,1}*→ /N , s■→ d = Qld (s) such that JN(d2 - 4Jf (id)) = JN(d2 - uM (id)) = -1 ;
generating the message m by accessing a private key usk = {rid} for a user with an identity id by following steps:
if rid 2≡ ffid (mod N), setting v = ε, γ = c and Δ = ffid; otherwise setting v = έ, γ = c and Δ = uRld;
determining σ = ]Ν{γ2— 4Δ),
setting
ΠΝ(γ + 2rid) if σ = 1
T = l (r + 2rid)(d - 2rid) (d - y)) if σ = -1< where d = and
determining the message m as
1— v · τ
In accordance with another aspect of the present principles, a computer program product stored in non-transitory computer-readable storage media is presented, for generating keys for an identity-based cryptosystem wherein a private key is used to decrypt ciphertext C = {ε, c, έ, c] of a plaintext message m for a user with an identity id where
 uRid ,, Λ c U)d + 4uRid
ε = (-l)m JN (t), c(°' = t + mod N, = mod N, t c^) + a
where N is a composite integer, ff id = Ή (id), t, i G (Έ/ΝΈ) Χ , d = Qid (s) , c = c(/3l) and c = c^2^ for random bits ?i, ?2 £ {0<1}, comprising computer-executable instructions for:
setting a master secret key msk; and
generating, using the master secret key msk, the private key usk = {rid} for a user with an identity id , using public system parameters m pk = {N, u, J , {Qld}, s}, where N is a composite integer, u G N \ Q W , 5 is bit-string, Ή is a cryptographic hash function mapping bit-strings to elements of N and { id} is a family of functions mapping bit-strings to elements of a subset of Έ/ΝΈ namely id : {0,1}*→ Έ/ΝΈ, Ξ <→ d = £;„(<?) such that JN (d2 - \W (id)) = JN (d2 - 4u?f (id)) = -1.
DETAILED DESCRIPTION OF THE DRAWINGS
The above-mentioned and other features and advantages of this invention, and the manner of attaining them, will become more apparent and the invention will be better understood by reference to the following description of embodiments of the invention taken in conjunction with the accompanying drawings, wherein:
Figures 1 to 3 show exemplary apparatus according to the present principles; and
Figures 4 to 6 show exemplary processes according to the present principles. The examples set out herein illustrate exemplary embodiments of the invention. Such examples are not to be construed as limiting the scope of the invention in any manner.
DETAILED DESCRIPTION
Technical problems to solve
In numerous scenarios, the recipient in a transmission needs to be kept anonymous. This allows users to maintain some privacy. Protecting communication content may be not enough, as already observed in a couple of papers (e.g., [4,5, 17]).
For example, by analyzing the traffic between an antenna and a mobile device, one can recover some information about [at least] user' s position and some details about the use of her mobile device. This information leaks easily during all day: it is a
common habit, indeed, to use a mobile phone every day and to keep it (almost) always switched on.
There are a couple of anonymous IBE schemes based on quadratic residuosity in the literature [9,11,3,10]. Among them the most efficient ones are those of Ateniese and Gasti [3] and the recent one by Clear et al. [10]. Table 1 in [10] gives a comparison of the schemes. The scheme by Clear et al. features the best encryption and decryption times (i.e., 79 ms and 27 ms for a 128-message with a key-size of 1024 bits in their setting). The security relies on the quadratic residuosity assumption in the random oracle model.
However, the cryptosystem by Clear et al. produces somewhat long ciphertexts. The goal of the present principles is to provide anonymous identity-based cryptosystems with much shorter ciphertexts. As will be seen, the resulting ciphertexts are twice shorter, improving all previous anonymous IBEs based on the quadratic residuosity. Extra useful properties offered by the proposed cryptosystems are listed later.
Main ideas
As a reminder, using the notation described before, Tp = {u\u G Wp \ {±<5}} U {∞) and Gp = {v = x + Sy\x, y G Wp, x2— Ay2 = 1} are groups under the respective laws © and · (multiplication in Wp); the respective neutral element are∞ and \.
Finally, Tp→ Gp, u <→ v = ψ(ιι) is a group isomorphism. Specifically, we have ψ(∞) = 1 and ψ(ΐί) = if u≠∞. We also define the subgroup of squares in Tp, namely (Tp)2 = {u © u\u G Tp}. Alternatively, as shown in [14], this group can be defined by
CFp)2 = {u G Wp \ {+8}\Jp{u2 - Δ) = 1} U {∞}.
Conversely, the group of non-squares in Tp can be defined as
(TPY2 = {u G Wp \ {±5}\]p(u2— Δ) = -1} U {∞}.
The next proposition [14] is central to our ideas.
Proposition 1. Let N = pq be an RSA modulus and let w G ( p \ {∞)) x
(?q \ {∞}). if
]N (w2 - A) = -l
then w £ Fp)2 x (Tq)2.
Let u G N \ QMW. It implies that elements of the form c =— -^- mod N
(respectively, c =— -^- mod N) (or multiples thereof)— where ffid = Ή (id) G Q JV (respectively, uRld = uK" (id) G Q W) is derived from some user's identity id— cannot be used as part of a ciphertext for user with identity id' because if
JN(c2— ffid') =— 1 (respectively, if JN (c2— uRldi) =— 1)— where ffid' = Ή (id') G QMW (respectively, uR id' = uK" (id') G Q W) for some other identity id'— then one can conclude that the identity of the recipient of the ciphertext is not id'. This clearly violates the anonymity requirement.
In order to address this issue, we propose to ©-multiply with probability 1 /2 the value of c (resp. c) by an element d satisfying JN(d2— Δ) =— 1 (resp. JN(d2— uA) =— 1). The decryption algorithm, assuming it is the legitimate recipient of the ciphertext, can then ©-divide by d the ciphertext in the case it was ©-multiplied by d; letting e (resp. e) the received part of the ciphertext, it is easy for the decryption algorithm to know if e = c or e = c © d (resp. e = c or e = c © d) by checking if JN(e2— Δ) = 1 or— 1 (resp. JN(e2— uA) = 1 or—1), respectively.
In a typical implementation, parameter d is derived from the system parameters and/or the identity of the recipient.
Remark 2. Instead of ©-dividing by d, one could also ©-multiply by d. The resulting element would then be in (Tp)2 x (Tq)2, as desired. A close inspection shows that the corresponding decryption process is likely less efficient.
Exemplary embodiments
First exemplary embodiment
The exemplary embodiments are now described in the framework of the flow diagram of Figure 3. Our first cryptosystem is defined as follows. For slightly better performance, all elements of Tp x Tq are scaled by a factor of 2.
SETUP(1K) Given a security parameter κ, SETUP generates an RSA modulus N = pq where p and q are prime. It selects a bit-string s. It also generates a random element u G N \ Q W . The public system parameters are mpk = {N, u, Ή, {£/jd}, s] where Ή is a cryptographic hash function mapping bit-strings to elements of N (i.e.,
Ή : {0,1}*→ JJ ) and {^id} is a family of functions mapping bit-strings to elements of a subset of Έ/ΝΈ, namely
gid: {0,l}*→%/N%, s d = gid(s) such that JN (d2 - \W (id)) = ]N d2 - 4u?f (id)) = -1. The master secret key is msk = {p, q}. EXTRACTmsk(id) Given identity id, key derivation algorithm EXTRACT first sets ffid = Ή (id). If ffid G Q N it computes rid = R-^1^2 mod N; otherwise it computes rid = (uR^)1^2 mod N. EXTRACT returns user's private key usk = {rid}.
ENCRYPTmpk(id, m) To encrypt a message m G {0,1} for a user with identity id , ENCRYPT first defines ffid = Ή (id). It chooses at random t, i G (Έ/ΝΈ)Χ satisfying gcd ( t2 - Rld, N) = gcd ( t2 - uRld, N) = 1 and lets e = {-l)mJN{t), c^ = t + -^ mod N, = g(0) rf mod N, ε = (-l)mJN(i), c(°' = t +— mod N, c« = ^ mod N, t c^) + a
where d = Qld (s). It chooses random bits β1, β2 £ {0,1} and sets c = c^1^ and c = c^2\ The returned ciphertext is C = {ε, c, έ, c}.
DECRYPTusk(C) Let Rid = Ή (id) . From usk = {rid} and C = {ε, c, έ, c], if rid 2≡ ff id (mod N), DECRYPT sets v = ε, γ = c and Δ = ffid; otherwise it sets v = έ, γ = c and Δ = uRld. Next, it computes σ = ]Ν{γ2— 4Δ). If σ £ {±1} it returns 1; otherwise, from d = Qld(s), it sets

and returns plaintext m as
1— v · τ
m = .
Remark 3. As an alternative, we see from Eq. (1) that the decryption algorithm can evaluate τ as τ = ]Ν γ— 2rid) when σ = 1 and as τ = ]Ν((γ— 2rid)(d + 2rid)(d - 7)) = - (r - 2rid)(did - 2rid)(did - y)) = -/w((y + 2rid)(d + 2rid)(d— y)) when σ =—1. Also the value of JN(d + 2rid) or of JN(d— 2rid) can be precomputed.
Remark 4. Input 5 can be the empty string in the encryption/decryption algorithm.
Remark 5. In a practical implementation, for better efficiency, the encryption algorithm can randomly draw t, i G Έ/ΝΈ.
Correctness
Correctness is straightforward and follows from [14]. Security analysis
The two next propositions assess the security of the scheme under the quadratic residuosity assumption, in the random oracle model.
Proposition 2. The scheme is I N D-I D-CPA under the quadratic residuosity assumption in the random oracle model.
Proof. Analogously to the proof of [14, Proposition 2] this would imply an I N D-l D-CPA adversary against the scheme of [15, first exemplary embodiment].
Proposition 3. The scheme is AN 0-1 D-CPA under the quadratic residuosity assumption in the random oracle model.
Proof. The proof can be derived from [14, Proposition 3].
The two propositions show that the scheme meets the AN 0- 1 N D-l D-CPA under the quadratic residuosity assumption in the random oracle model.
Second exemplary embodiment
Let £ represent the bit-length of RSA modulus N. Similarly to [14], the previous scheme can be adapted so that the ciphertext needs at most 2£ bits for its representation— the previous implementation needs 2£ + 2 bits. Here is an implementation of a so-obtained cryptosystem.
SETUP(1K) Given a security parameter κ, SETUP generates an RSA modulus N = pq where p and q are prime. It selects a bit-string s. It also generates a random element u G N \ QMW. The public system parameters are m pk = {N, u, Ή, {^jd}, s] where Ή is a cryptographic hash function mapping bit-strings to elements of N (i.e., Ή : {0,1}* → Jw) and
 is a family of functions mapping bit-strings to elements of a subset of Έ/ΝΈ, namely
6id:{0,l}*→ Έ/ΝΈ,σ■→ d = ld(s) such that JN(d2 - 4Jf(id))
= JN(d2 -4uKQd)) = -1.
The master secret key is msk = {p, q}.
EXTRACTmsk(id) Given identity id, key derivation algorithm EXTRACT first sets ffid = Ή (id). If ffid G Q N it computes rid = R-^1^2 mod N; otherwise it computes rid = (uR^)1^2 mod N. EXTRACT returns user's private key usk = {rid}.
ENCRYPTmpk(id, m) To encrypt a message m G {0,1} for a user with identity id, ENCRYPT first defines ffid = Ή (id). It chooses at random t, i G TL/NTL and lets ε' = (-l)m]N(t), c'(0) = t+— mod N, c'(1) = -— ,+ R'd mod N, t c'{0) + d ε' = (-l)mJN(t), mod N,

where d = £/jd s). It chooses random bits βί,β2 G {0,1} and sets c' = c'^1^ and c' = Define c = min (c',N - c') and c = min (c',N - c'). If c = c' then define ε = ε'; otherwise define
= (ε'· -ΐ) if ?1 = o
£ Ιε' -JN(-(td + 2Rid)(td + 2t2)) if ?! = l' Likewise, if c = c' then define έ = έ'; otherwise define
£
 '
The returned ciphertext is C = {ε, c, έ, c}.
DECRYPTusk(C) Let Rid = Ή (id). From usk = {rid} and C = {ε, c, έ, c], if rid 2≡ i?id (mod N , DECRYPT sets v = ε,γ = c and Δ = ff id; otherwise it sets v = έ,γ = c and Δ = uRld. Next, it computes σ = ]N( 2— 4Δ). If σ *fc {±1} it returns 1; otherwise, from d = £/jd s), it sets

and returns plaintext m as
1— v · τ
m = .
Remark 6. For slightly better efficiency, as a variant, the encryption algorithm directly evaluate ε as ε = (—l)mJN(—(td + 2Rld)(d + 2t)) when c≠ c' and
β1 = 1. Likewise, it can evaluate έ as έ = (—l)mJN(—(id + 2uRld)(d + 2i)) when c≠ c' and β2 = 1.
Remark 7. As an alternative, the decryption algorithm can evaluate τ as
T = JN(I - 2rid) when σ = 1 and as τ = /w ((y - 2rid)(d + 2rid)(d - y)) =
-7w ((y - 2rid)(did - 2rid)(did - y)) = -/w ((y + 2rid)(d + 2rid)(d - y)) when σ =— 1. Also the value of /w(d + 2rid) or of JN(d— 2rid) can be precomputed.
Third exemplary embodiment
Instead of selecting parameter d as the output of a family of functions, it can be chosen as, for example, the smallest nonnegative integer d such that JN(d2— ΑΉ (id)) = JN(d2 - uH (id)) = -1. We give below an illustration with the first exemplary embodiment. A similar embodiment can be obtained for the second exemplary embodiment.
The advantage is that the system parameters are smaller since {QLD} is not explicitly included in mpk.
SETUP(1K) Given a security parameter κ, SETUP generates an RSA modulus N = pq where p and q are prime. It also generates a random element u G N \ Q W. The public system parameters are m pk = {N, u, where Ή is a cryptographic hash function mapping bit-strings to elements of N. The master secret key is msk = {p, q}.
EXTRACTmsk(id) Given identity id, key derivation algorithm EXTRACT first sets ffid = Ή (id). If ffid G Q N it computes rid = ff ^1 2 mod N; otherwise it computes rid = (uR^)1^2 mod N. EXTRACT returns user's private key usk = {rid}.
ENCRYPTmpk(id, m) To encrypt a message m G {0,1} for a user with identity id , ENCRYPT first defines ffid = Ή (id). Next, it tries d = 0,1,2, ... until JN(d2 - 4ffid) = JN(d2 - 4ui?id) = -1. It chooses at random t, i G Έ/ΝΈ and lets ε = (-l)mJN(t), c(°> = t +— mod N, c« = mod N, t c^) + d ε = (-l)mJN(i), c<°> = t +— - mod N, c& =— _(Q) mod N.
It chooses random bits β1, β2 G {0,1} and sets c = c^1^ and c = c^2 The returned ciphertext is C = {ε, c, έ, c}.
DECRYPTusk(C) Let Rid = Ή (id) . From usk = {rid} and C = {ε, c, έ, c], if rid 2≡ i?id (mod N , DECRYPT sets v = ε, γ = c and Δ = ff id; otherwise it sets
v = ε, γ = c and Δ = uRld. Next, it computes σ = ]Ν{γ2— 4Δ). If σ £ {±1} it returns 1; otherwise, it sets
r y + 2rid) ίί σ = 1
T t;W((7 + 2rid)(d - 2rid)(d - 7)) ίί σ = -1 and returns plaintext m as
1— v · τ
m = The value d used by DECRYPT is the smallest nonnegative integer d such that
JN(d2— 4ffid) = JN(d2— 4uffid) =— 1. This value can also be precomputed.
Remark 8. As an alternative, the decryption algorithm can evaluate τ as = JN(J - 2rid) when σ = 1 and as τ = /w((y - 2rid)(d + 2rid)(d - y)) =
7« ((y - 2rid)(did - 2rid)(did - y)) = -/w((y + 2rid)(d + 2rid)(d - y)) when =— 1. Also the value of JN (d + 2rid) or of JN(d— 2rid) can be precomputed.
Fourth exemplary embodiment
It is possible to fix the value of d as a global value to be used with all identities and to include it in the system parameters. We again illustrate the technique with the first exemplary embodiment. A similar embodiment can be obtained for the second exemplary embodiment.
This can be achieved by specializing hash function Ή . Instead of considering a function mapping bit-strings to any element of N, we require that, in addition, on input id, the output must satisfy the extra condition JN(d2— 4ffid) = JN (d2— 4uffid) =—1 for some given d:

H> Jfd (id) satisfying JN(d2 - 4Jfd (id)) (2) = JN (d2 - d (id)) = -1.
SETUP(1K) Given a security parameter κ, SETUP generates an RSA modulus N = pq where p and q are prime. It also generates a random element u G N \ Q W and a global integer d. The public system parameters are mpk = {N, u, d, J d} where Ήά is a cryptographic hash function as per Eq. (2). The master secret key is msk =
{P. <?}■
EXTRACTmsk(id) Given identity id, key derivation algorithm EXTRACT first sets ffid = J-Cd(\d). If ffid G Q W it computes rid = R^1^2 mod N; otherwise it computes rid = (uR^)1^2 mod N. EXTRACT returns user's private key usk = {rid}.
ENCRYPTmpk(id, m) To encrypt a message m G {0,1} for a user with identity id, ENCRYPT first defines ffid = Jfd(id). It chooses at random t, i G TL/NTL and lets e = {-l)mJN{t), c^ = t + -^ mod N, = g(0) rf mod N
uff c(0)d + 4uff/d έ = (-l)m t), c(°' = t + - mod N, c« =— -(0) + d mod
It chooses random bits ?i, ?2 G {0<1} and sets c = c^1^ and c = c^2^ . The returned ciphertext is C = {ε, c, έ, c}.
DECRYPTusk(C) Let Rid = J£d( d . From usk = {rid} and C = {ε, c, έ, c], if rid 2≡ i?id (mod N), DECRYPT sets v = ε, γ = c and Δ = ff id; otherwise it sets v = έ, γ = c and Δ = uRld. Next, it computes σ = ]N(j2 - 4Δ). If σ £ {±1} it returns 1; otherwise, it sets
r;w(y + 2rid) ίί σ = 1
T t;W((7 + 2rid)(d - 2rid)(d - y)) if σ = -1 and returns plaintext m as
1— v · τ
m
Remark 9. In order to have short system parameters mpk, it may be advantageous to select a small value for d.
Remark 10. As an alternative, the decryption algorithm can evaluate τ as T = JN(I - 2rid) when σ = 1 and as τ = /w((y - 2rid)(d + 2rid)(d - y)) =
- (r - 2rid)(did - 2rid)(did - y)) = -/w((y + 2rid)(d + 2rid)(d - y)) when σ =—1. Also the value of JN(d + 2rid) or of JN(d— 2rid) can be precomputed.
Fifth exemplary embodiment
Assume now primes p and q satisfy the extra condition p≡—q (mod 4). In this case, we know that Jp(—1) =—Jq(—1) and therefore JN(— 1) =—1. Note that it is easily verified that N is the product of two primes that are inversely congruent modulo 4 by checking that N≡ 3 (mod 4).
This setting simplifies the cryptosystem. A nice observation is that d = 0 is a valid parameter when N≡ 3 (mod 4) since then JN (d2— Ή (id)) = JN (d2— 4uJ (id)) = JN (—1) =—1 as desired. Any cryptographic hash function Ή mapping bit- strings to elements of N can be used.
SETUP(1K) Given a security parameter κ, SETUP generates an RSA modulus
N = pq where p and q are prime and p≡—q (mod 4) . It also generates a random element u G N \ Q W . The public system parameters are m pk = {N, u, where Ή is a cryptographic hash function mapping bit-strings to elements of N . The master secret key is msk = {p, q}.
EXTRACTmsk(id) Given identity id, key derivation algorithm EXTRACT first sets ffid = Ή (id). If ffid G Q N it computes rid = R^1^2 mod N; otherwise it computes rid = (uR^)1^2 mod N. EXTRACT returns user's private key usk = { ά}·
ENCRYPTmpk(id, m) To encrypt a message m G {0,1} for a user with identity id , ENCRYPT first defines ffid = Ή (id). It chooses at random t, i G TL/NTL and lets ε = (-l)m JN (t), c(°' = t +— mod N, c« = ¾ mod N, ε = (-l)m ;w (t), c(°> = t + ^ mod N, c« =— ^ mod N. It chooses random bits β1, β2 £ {0,1} and sets c = c^1^ and c = c^2 The returned ciphertext is C = {ε, c, έ, c}.
DECRYPTusk(C) Let i?id = Ή (id) . From usk = {rid} and C = {ε, c, έ, c], if rid 2≡ ff id (mod N , DECRYPT sets v = ε, γ = c and Δ = ff id ; otherwise it sets v = έ, γ = c and Δ = uRld . Next, it computes σ = ]Ν {γ2— 4Δ). If σ ¾ {±1} it returns 1; otherwise, it sets

and returns plaintext m as
1— v · τ
m = .
Remark 11. For better efficiency, as a variant, the encryption algorithm can first choose β , β2 at random in {0,1} and then sets c = t + mod N if βί = 0 and
^≤^ mod Nif/?1 = l;andc = t + ^mod N if β2 mod Nif/?2 = 1.
i2+uRid
Remark 12. As an alternative, the decryption algorithm can evaluate τ as Τ = JN(Y— 2^id) when σ = 1 and as τ =—Jn((Y— 2rid)(2ridy)) when σ =— 1. Also the value of 7w(2rid) can be precomputed.
5ϊχίΛ exemplary embodiment
The next embodiment corresponds to the case N≡ 3 (mod 4) and d = 0 applied to the second exemplary embodiment.
Assume ffid = Jf(id) G Q W. Then, using the notation of the second exemplary embodiment, we notice that
JN(-(td + 2ffid)(td + 2t2)) = -4ffidt2) = JN(-1) = -1 when d = 0. Hence, in the encryption process, if c≠ c' we always have ε = ε' ·/«(— 1) =— , whatever the value of β . The case uRld = η (id) G QMW (i.e., (id) G Jw \ QMW) is similar. We always have έ = έ' · JN(— 1) =— ε, whatever the value of β2.
SETUP(1K) Given a security parameter κ, SETUP generates an RSA modulus N = pq where p and q are prime and p≡—q (mod 4). It also generates a random element u G N \ Q W. The public system parameters are mpk = {N, u, where Ή is a cryptographic hash function mapping bit-strings to elements of N . The master secret key is msk = {p, q}.
EXTRACTmsk(id) Given identity id, key derivation algorithm EXTRACT first sets ffid = Ή (id). If ffid G Q N it computes rid = ff jd^2 mod N; otherwise it computes rid = (uR^)1^2 mod N. EXTRACT returns user's private key usk = {rid}.
ENCRYPTmpk(id, m) To encrypt a message m G {0,1} for a user with identity id, ENCRYPT first defines ffid = Ή (id). It chooses at random t, i G TL/NTL and lets ε' = (-l)m;w(t), c'(0) = t +— mod N, c'(1) = ^ mod N,
§' = -l)mJN i), c'(0) = t + ^ mod N, c'(1) =^mod Λί.
It chooses random bits βί,β2 G {0,1} and sets c' =
 Define c = min (c',N— c') and c = min (c',N— c'). If c = c' then define ε = ε';
otherwise define ε =—ε' . Likewise, if c = c' then define ε = ε' ; otherwise define έ =—έ' . The returned ciphertext is C = {ε, c, έ, c}.
DECRYPTusk(C) Let Rid = Ή (id). From usk = {rid} and C = {ε, c, έ, c], if rid 2≡ ff id (mod N , DECRYPT sets v = ε, γ = c and Δ = ff id ; otherwise it sets v = έ, γ = c and Δ = wffid . Next, it computes σ = ]Ν {γ2— 4Δ). If σ £ {±1} it returns 1; otherwise, from d = £/jd s) , it sets

and returns plaintext m as
Remark 13. For better efficiency, as a variant, the encryption algorithm can first choose β , β2 at random in {0,1} and then sets c' = t + ^ mod N if β = 0 and c' = - ^ mod N if β1 = 1 ; and c' = i + ^ mod N if β2 = 0 and c' = mod Ν ιί β2 = 1.
t2+uRid r
Remark 14. As an alternative, the decryption algorithm can evaluate τ as Τ = JN (Y— 2^id) when σ = 1 and as τ = —Jn ((Y— 2rid) (2rid7)) when σ =—1. Also the value of 7w (2rid) can be precomputed.
There are several advantages for the proposed cryptosystems:
• identity-based paradigm;
• both confidentiality and anonymity;
· short ciphertexts;
• fast encryption/decryption times;
• building blocks for PEKS (public-key encrypton with keyword search);
• strong security guarantees. The proposed encryption systems can be used in any application requiring efficient anonymous identity-based encryption. Compared with [14], the new cryptosystems proposed in this application present the advantage of being identity- based. This solves a number of practical issues in real systems. However, the ciphertexts are twice longer.
An important application of anonymous IBEs is public key encryption with keyword search (PEKS) [7]. PEKS allows searching on data that is encrypted using a public -key system. A typical application is for an email gateway to test whether or not the keyword "urgent" is present in an email. The gateway then routes the email if it is the case. Of course the gateway should only learn whether the word "urgent" is present but nothing else about the email. Further applications for PEKS can be found in [7].
FIG. 1 illustrates a block diagram of an exemplary system in which various aspects of the exemplary embodiments of the present principles may be implemented. System 100 may be embodied as a device including the various components described below and is configured to perform the processes described above. Examples of such devices, include, but are not limited to, personal computers, laptop computers, smartphones, tablet computers, digital multimedia set top boxes, digital television receivers, personal video recording systems, connected home appliances, and servers. System 100 may be communicatively coupled to other similar systems, and to trusted third parties via a communication channel as shown in Figure 2 and as known by those skilled in the art to implement the exemplary cryptosystems described above.
The system 100 may include at least one processor 110 configured to execute instructions loaded therein for implementing the various processes as discussed above. Processor 110 may include embedded memory, input output interface and various other circuitries as known in the art. The system 100 may also include at least one memory 120 (e.g., a volatile memory device, a non-volatile memory device). System 100 may additionally include a storage device 140, which may include nonvolatile memory, including, but not limited to, EEPROM, ROM, PROM, RAM, DRAM, SRAM, flash, magnetic disk drive, and/or optical disk drive. The storage device 140 may comprise an internal storage device, an attached storage device and/or a network accessible storage device, as non-limiting examples. System 100 may also include an encryption/decryption module 130 configured to process data to provide an encrypted message or decrypted message.
Encryption/decryption module 130 represents the module(s) that may be included in a device to perform the encryption and/or decryption functions. As is known, a device may include one or both of the encryption and decryption modules, for example, encryption may be done on a regular PC since encryption does not involve secret key so that the PC need not include secure memory for storing the input
parameters (i.e., the public system parameters and the user's identity). Decryption however, requires secret keys (i.e., the decryption key) and is done in a secure device, for example a smart card. As memory is expensive on smart card, the encryption functionality may not always be provided on a smart card. The encryption and/or decryption may be performed using shared resources as known to those skilled in the art. Additionally, encryption/decryption module 130 may be implemented as a separate element of system 100 or may be incorporated within processors 110 as a combination of hardware and software as known to those skilled in the art.
Program code to be loaded onto processors 110 to perform the various processes described hereinabove may be stored in storage device 140 and
subsequently loaded onto memory 120 for execution by processors 110. In accordance with the exemplary embodiments of the present principles, one or more of the processor(s) 110, memory 120, storage device 140 and encryption/decryption module 130 may store one or more of the various items during the performance of the processes discussed herein above, including, but not limited to a public system parameters, a private key, encrypted messages, equations, formula, matrices, variables, operations, and operational logic.
The system 100 may also include communication interface 150 that enables communication with other devices via communication channel 160. The
communication interface 150 may include, but is not limited to a transceiver configured to transmit and receive data from communication channel 160. The communication interface may include, but is not limited to, a modem or network card and the communication channel may be implemented within a wired and/or wireless medium. The various components of system 100 may be connected or
communicatively coupled together using various suitable connections, including, but not limited to internal buses, wires, and printed circuit boards.
As a non- limiting example, one or more of the above-identified components may receive and/or store the information (e.g., to be encrypted) and/or the ciphertext (e.g., to be decrypted, to be operated on homomorphically, resulting from encryption). As a further non-limiting example, one or more of the above-identified components may receive and/or store the encryption function(s) and/or the decryption function(s), as described herein above.
The exemplary embodiments of this invention may be carried out by computer software implemented by the processor 110 or by hardware, or by a combination of
hardware and software. As a non-limiting example, the exemplary embodiments of this invention may be implemented by one or more integrated circuits. The memory 120 may be of any type appropriate to the technical environment and may be implemented using any appropriate data storage technology, such as optical memory devices, magnetic memory devices, semiconductor-based memory devices, fixed memory and removable memory, as non-limiting examples. The processor 110 may be of any type appropriate to the technical environment, and may encompass one or more of microprocessors, general purpose computers, special purpose computers and processors based on a multi-core architecture, as non-limiting examples.
Figure 2 illustrates an arrangement wherein data is exchanged between two terminals 210 and 220 in accordance with the present principles. Each of the terminals 210 and 220 include encryptor/decryptor modules 230 and 240, respectively, and may additionally include each of the other components of system 100 described above, as appropriate. Terminals 210 and 220 are communicatively coupled to each other via communication channel 250, which may be implemented via wired and/or wireless medium. Additionally, arrangement 200 may include a trusted third party 260 communicatively coupled to terminals 210 and 220, wherein third party 260 may in some cases, among other things, generate common parameters and the keys, distribute them to the terminals, and/or generate common keys in a manner known to those skilled in the art. For example, in identity based encryption, the setup algorithm is performed by the trusted third party to generate, among other things, the master secret key. Following key generation, a message can be encrypted and decrypted by the terminals as described above, and transmitted and received via communication channel 250.
Figure 3 illustrates a generalized flow diagram of an identity-based cryptosystem.
Figures 4 to 6 show exemplary flow charts according to the present principles. The flow charts illustrate the anonymous identity-based crypto processes discussed above. The processes of Figures 4 - 6 may be executed by e.g., a processor 110 of Figure 1. The processes may represent, e.g., computer program products having the computer-executable instructions which may be stored in non-transitory computer- readable storage media 120 of Figure 1 as described before.
The foregoing has provided by way of exemplary embodiments and non- limiting examples a description of the method and systems contemplated by the
inventor. It is clear that various modifications and adaptations may become apparent to those skilled in the art in view of the description. However, such various modifications and adaptations fall within the scope of the teachings of the various embodiments described above.
The embodiments described herein may be implemented in, for example, a method or a process, an apparatus, a software program, a data stream, or a signal. Even if only discussed in the context of a single form of implementation (for example, discussed only as a method), the implementation of features discussed above may also be implemented in other forms (for example, an apparatus or program). An apparatus may be implemented in, for example, appropriate hardware, software, and firmware. The methods may be implemented in, for example, an apparatus such as, for example, a processor, which refers to processing devices in general, including, for example, a computer, a microprocessor, an integrated circuit, or a programmable logic device. Processors also include communication devices, such as, for example, computers, cell phones, portable/personal digital assistants ("PDAs"), and other devices that facilitate communication of information between end-users.
Reference to "one embodiment" or "an embodiment" or "one implementation" or "an implementation" of the present principles, as well as other variations thereof, mean that a particular feature, structure, characteristic, and so forth described in connection with the embodiment is included in at least one embodiment of the present principles. Thus, the appearances of the phrase "in one embodiment" or "in an embodiment" or "in one implementation" or "in an implementation", as well any other variations, appearing in various places throughout the specification are not necessarily all referring to the same embodiment.
Additionally, this application or its claims may refer to "determining" various pieces of information. Determining the information may include one or more of, for example, estimating the information, calculating the information, predicting the information, or retrieving the information from memory.
Further, this application or its claims may refer to "accessing" various pieces of information. Accessing the information may include one or more of, for example, receiving the information, retrieving the information (for example, from memory), storing the information, processing the information, transmitting the information, moving the information, copying the information, erasing the information, calculating
the information, determining the information, predicting the information, or estimating the information.
Additionally, this application or its claims may refer to "receiving" various pieces of information. Receiving is, as with "accessing", intended to be a broad term. Receiving the information may include one or more of, for example, accessing the information, or retrieving the information (for example, from memory). Further, "receiving" is typically involved, in one way or another, during operations such as, for example, storing the information, processing the information, transmitting the information, moving the information, copying the information, erasing the information, calculating the information, determining the information, predicting the information, or estimating the information.
As will be evident to one of skill in the art, implementations may produce a variety of signals formatted to carry information that may be, for example, stored or transmitted. The information may include, for example, instructions for performing a method, or data produced by one of the described embodiments. For example, a signal may be formatted to carry the bitstream of a described embodiment. Such a signal may be formatted, for example, as an electromagnetic wave (for example, using a radio frequency portion of spectrum) or as a baseband signal. The formatting may include, for example, encoding a data stream and modulating a carrier with the encoded data stream. The information that the signal carries may be, for example, analog or digital information. The signal may be transmitted over a variety of different wired and/or wireless links, as is known. The signal may be stored on a processor-readable medium.
While several embodiments have been described and illustrated herein, those of ordinary skill in the art will readily envision a variety of other means and/or structures for performing the functions and/or obtaining the results and/or one or more of the advantages described herein, and each of such variations and/or modifications is deemed to be within the scope of the present embodiments. More generally, those skilled in the art will readily appreciate that all parameters, dimensions, materials, and configurations described herein are meant to be exemplary and that the actual parameters, dimensions, materials, and/or configurations will depend upon the specific application or applications for which the teachings herein is/are used. Those skilled in the art will recognize, or be able to ascertain using no more than routine experimentation, many equivalents to the specific embodiments described herein. It
is, therefore, to be understood that the foregoing embodiments are presented by way of example only and that, within the scope of the appended claims and equivalents thereof, the embodiments disclosed may be practiced otherwise than as specifically described and claimed. The present embodiments are directed to each individual feature, system, article, material and/or method described herein. In addition, any combination of two or more such features, systems, articles, materials and/or methods, if such features, systems, articles, materials and/or methods are not mutually inconsistent, is included within the scope of the present embodiment.
Claims
1. A method for communicating a message m, comprising:
accessing the message m;
accessing a user identity id and public system parameters mpk = {N, u, Ή,
 s], where N is a composite integer, u G N \ Q W, 5 is a bit-string, Ή is a cryptographic hash function mapping bit-strings to elements of N and {Qld} is a family of functions mapping bit-strings to elements of a subset of Έ/ΝΈ, namely Qld: {0,1}*→ Έ/ΝΈ, s <→ d = gid(s such that JN(d2 - K (id)) = JN(d2 - uK (id)) = -1;
generating a ciphertext C = {ε, c, έ, c] of the message m using the user identity id, where e= {-l)mJN{t), cW = t + -^ mod N, c∞ = ^ ^ mod N,
,ηΛ _ uRjj c^d + uRjj
ε = (-l)m , c(0) = t + - mod N, =— } mod N, where ffid = (id), t, i G (Έ/ΝΈ)Χ, d = Qld(s), choosing random bits β1,β2 G {0,1} and setting c = c^1^ and c = c^2-1; and
transmitting the ciphertext C = {ε, c, έ, c] via a communication channel.
2. The method of claim 1, wherein N = pq,p and q are prime.
3. The method of claim 1, wherein the message m G {0,1}.
4. The method of claim 1, wherein the ciphertext C = {ε, c, έ, c] is determined instead by the following steps:
setting ε' = (-l)m;w(t), c'(0) = t +— mod N, c'(1) = -— ^^ mod IV,
t c'(0) + d
_ uRiri C' ^ ^ d + llRjri
ε' = (-l)mJN(t), c'(0) = t + -^- mod N, c'(1) = mod N;
t c'(0) + d
choosing random bits β1, β2 G {0,1};
setting c' = c'(/Jl) and c' = c'(¾) ;
setting c = min ( c', N— c') and c = min ( c', N— c');
if c = c' then setting ε = ε'; otherwise setting
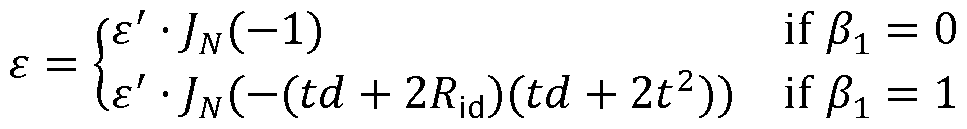 ' an
if c = c' then setti = έ'; otherwise setting

5. The method of claim 1, wherein d is the smallest nonnegative integer d such that such that JN (d2 - K (id)) = JN(d2 - uK (id)) = -1.
6. The method of claim 1 , wherein d is fixed as a global value to be used with all identities.
7. The method of claim 1 , wherein N is such that JN(— 1) =—1.
8. The method of claim 7, wherein d = 0.
9. A method for processing a ciphertext, comprising:
receiving the ciphertext C = {ε, c, έ, c] for a user with an identity id via a communication channel;
accessing the ciphertext C = {ε, c, έ, c] of a plaintext message m, where ε = (-l)mJN(t), c^ = t + - mod N, = (0) mod N,
uRid c(0)d + AuRjd
ε = (-l)mJN(t), = t + - mod N, =— } mod N, where N is a composite integer, ffid = (id), t, t £ Έ/ΝΈ Χ, d = Qld (s , c = c(/3l) and c = c^2) for random bits β1, β2 G {0,1}, wherein public system parameters m pk = {N, u, Ή, {£/ iC|}, s], where N is a composite integer, u G N \ Q W, 5 is bit-string, Ή is a cryptographic hash function mapping bit- strings to elements of N and {^id} is a family of functions mapping bit-strings to elements of a subset οΐ Έ/ΝΈ, namely ^id: {0,1}*→
/N , s B d = gid (s) such that JN(d2 - 4Jf (id)) = JN(d2 - uH (id)) = -1; and generating the message m by accessing a private key usk = {rid} for a user with an identity id by following steps:
if rid 2≡ ffid (mod N), setting v = ε, γ = c and Δ = ffid; otherwise setting v = έ, γ = c and Δ = uRld ;
determining σ = /w(y2— 4Δ),
setting
( y + 2rid) \ί σ = 1
T = l (r + 2rid)(d - 2rid)(d - y)) if = -V ^ d = ^ and determining the message m as
1— v · τ
m
10. The method of claim 9, wherein the private key usk = {rid} for the user with the identity id is generated by a master secrete key msk, wherein ffid = Ή (id), and if ffid G then rid = R ^1^2 mod N; otherwise, rid = (wff ^)1/2 mod N.
11. The method of claim 10, wherein N = pq, p and q are prime.
12. The method of claim 11 , wherein the master secret key is msk = (p, q}.
13. The method of claim 9, wherein the message m G {0,1}·
14. The method of claim 9, wherein d is the smallest nonnegative integer d such that such that JN (d2 - K (id)) = JN(d2 - uK (id)) = -1.
15. The method of claim 9, wherein d is fixed as a global value to be used with all identities.
16. The method of claim 9, wherein N is such that JN(—1) =— 1.
17. The method of claim 16, wherein d = 0.
18. A method for generating keys for an identity-based cryptosystem wherein a private key is used to decrypt ciphertext C = {ε, c, έ, c] of a plaintext message m for a user with an identity id where e = {-l)mJN{t), cW = t + -^ mod N, c∞ = ^ ^ mod N,
,ηΛ _ uRj j c^d + uRj j
e = {-l)mJN{t), cW = t + - mod N, = _(Q) rf mod N where N is a composite integer, i?id = K (id), t, t £ (Έ/ΝΈ Χ, d = id (s), c = c(/3l) and c = c^2^ for random bits β1, β2 G {0,1}, comprising:
setting a master secret key msk; and
generating, using the master secret key msk, the private key usk = {rid} for a user with an identity id, using public system parameters mpk = {N, u, Ή, {Q-^}, s], where N is a composite integer, u G N \ Q W , 5 is bit-string, Ή is a cryptographic hash function mapping bit-strings to elements of N and {^id} is a family of functions mapping bit-strings to elements of a subset of Έ/ΝΈ namely
6id: {0,l}*→ 1/N1, s i→ d = gid (s such that JN(d2 - 4Jf(id)) = JN d2 - 4uJf(id)) =
-1.
19. The method of claim 18, wherein N = pq, p and q are prime.
20. The method of claim 19, wherein msk = {p, q}.
21. The method of claim 18, wherein N is such that JN(— 1) =—1.
22. An apparatus for communicating a message m, comprising:
a processor configured to access the message m, the processor further configured to access a user identity id and public system parameters mpk = {N, u, Ή, {Q d}, s], where N is a composite integer, u G N \ Q W, 5 is a bit-string, Ή is a cryptographic hash function mapping bit-strings to elements of N and {Qld} is a family of functions mapping bit- strings to elements of a subset οΐ Έ/ΝΈ, namely Qld: {0,1}* → Έ/ΝΈ, s <→ d =
gid(s such that JN (d2 - K (id)) = JN(d2 - uK (id)) = -1;
an encryptor configured to generate a ciphertext C = {ε, c, έ, c] of the message m using the user identity id, where
R c^d + 4ff- ε = (-l)m;w(t), cM = t + - mod N, = ,a mod N,
uRid ,Λ c(0)d + AuRjd
ε = (-l)m , = t + - mod N, =— } mod N, where ff id = H " (id), t, i G (Έ/ΝΈ)Χ , d = Qid (s), choosing random bits β1, β2 G {0,1} and setting c = c^1^ and c = c^2-1; and
a communication interface, coupled to a communication channel, configured to transmit the ciphertext C = {ε, c, έ, c] via the communication channel.
23. The apparatus of claim 22, wherein N = pq, p and q are prime.
24. The apparatus of claim 22, wherein the message m G {0,1}.
25. The apparatus of claim 23, wherein the ciphertext C = [ε, c, έ, c] is determined instead by the following steps:
setting ε' = (-l)m;w(t), c'(0) = t +— mod N, c'W = -— + Rid mod N,
t c'(0) + d
_ URiri (Λ C'^ ^ d + llRjri
ε' = (-l)mJN(t), c'(0) = t + -^- mod N, c'(1) = mod N;
t c'(0) + d
choosing random bits β^ β2 £ {0,1};
setting c' = ε'(βι) and c' = c'(¾) ;
setting c = min ( c', N— c') and c = min ( c', N— c');
if c = c' then setting ε = ε'; otherwise setting
= '■;*(-!) if ?! = o
^ ' - JN{- td + 2ffid)(td + 2t2)) if ft = l ' an
if c = c' then setting έ = έ'; otherwise setting
(έ'■;*(-!) if ^2 = 0
' · JN(-(td + 2uRld)(id + 2i2)) if /?2 = 1'
26. The apparatus of claim 22, wherein d is the smallest nonnegative integer d such that such that JN (d2 - K (id)) = JN(d2 - uK (id)) = -1.
27. The apparatus of claim 22, wherein d is fixed as a global value to be used with all identities.
28. The apparatus of claim 22, wherein N is such that /«(—!) =—1.
The apparatus of claim 28, wherein d
30. An apparatus for processing a ciphertext, comprising:
a communication interface, coupled to a communication channel, configured to receive the ciphertext C = {ε, c, έ, c] of a plaintext message m, where
R c^d + 4ff- ε = (-l)m t), c = t + - mod N, = ,a mod N,
,ηΛ _ uRj j c^d + uRj j
ε = (-l)mJN(t), = t + - mod N, =— } mod N, where N is a composite integer, ffid = (id), t, t £ (Έ/ΝΈ)Χ, d = Qid (s), c = c(/3l) and c = c^2^ for random bits β1, β2 G {0,1}, wherein public system parameters mpk = {N, u, Ή, {£/ jd}, s], where N is a composite integer, u G N \ Q W, 5 is bit-string, Ή is a cryptographic hash function mapping bit- strings to elements of N and { id} is a family of functions mapping bit-strings to elements of a subset οΐ Έ/ΝΈ, namely ^id: {0,1}*→
1/N1, s B d = gid (s) such that JN(d2 - 4Jf (id)) = JN d2 - uK (id)) = -1; and a processor configured to generate the plaintext message m by accessing a private key usk = {rid} for a user with an identity id by following steps:
if rid 2≡ ffid (mod N), setting v = ε, γ = c and Δ = ffid; otherwise setting v = έ, γ = c and Δ = uRld ;
determining σ = ]Ν{γ2— 4Δ),
setting
T = k((7 + 2rid)(d - 2rid)(d - y)) if a = -V ^ d = ^ d determining the plaintext m as
1— v · τ
31. The apparatus of claim 30, wherein the private key usk = {rid} for the user with the identity id is generated by a master secrete key msk, wherein ffid = Ή (id), and if ffid G QRN then rid = R id 1/2 mod N; otherwise, rid = (uffid)1/2 mod N.
32. The apparatus of claim 31 , wherein N = pq, p and q are prime.
33. The apparatus of claim 32, wherein the master secret key is msk = {p, q}.
34. The apparatus of claim 30, wherein the message m G {0,1}·
35. The apparatus of claim 30, wherein d is the smallest nonnegative integer d such that such that JN (d2 - K (id)) = JN(d2 - uK (id)) = -1.
36. The apparatus of claim 30, wherein d is fixed as a global value to be used with all identities.
37. The apparatus of claim 30, wherein N is such that JN(— 1) =—1.
38. The apparatus of claim 37, wherein d = 0.
39. An apparatus for generating keys for an identity-based cryptosystem wherein a private key is used to decrypt ciphertext C = {ε, c, έ, c] of a plaintext message m for a user with an identity id where ε = (-l)mJN(t), c^ = t + - mod N, = (0) mod N, uRid c(0)d + AuRjd
ε = (-l)mJN(t), = t + - mod N, =— } mod N, where N is a composite integer, ffid = (id), t, t £ (Έ/ΝΈ)Χ, d = Qid (s), c = c^1^ and c = c^2^ for random bits β^ β2 G {0,1}, comprising:
a processor configured to set a master secret key msk, and generate, using the master secret key msk, the private key usk = {rid} for a user with an identity id, using public system parameters mpk = {N, u, Ή, {Q^}, s], where N is a composite integer, u G N \ Q W, 5 is bit-string, Ή is a cryptographic hash function mapping bit-strings to elements of N and { id} is a family of functions mapping bit-strings to elements of a subset οΐ Έ/ΝΈ namely £id : {0,1}*→ %/N%, s >→ d = Qid (s) such that JN(d2 - 4Jf (id)) = JN (d2 - uK (id)) = -1; and
a communication interface, coupled to a communication channel, configured to transmit the private key usk = {rid} via the communication channel.
40. The apparatus of claim 39, wherein N = pq, p and q are prime.
41. The apparatus of claim 40, wherein msk = {p, q}.
42. The apparatus of claim 39, wherein N is such that JN(—1 = -1.
43. A computer program product stored in non-transitory computer-readable storage media comprising computer-executable instructions for:
accessing the message m;
accessing a user identity id and public system parameters m pk = {N, u, Ή, {Q d}, s], where N is a composite integer, u G N \ Q W, 5 is a bit-string, Ή is a cryptographic hash function mapping bit-strings to elements of N and {Qld} is a family of functions mapping bit-strings to elements of a subset of Έ/ΝΈ, namely Qld: {0,1}* → Έ/ΝΈ, s <→ d = gid(s such that JN (d2 - K (id)) = JN(d2 - uK (id)) = -1;
generating a ciphertext C = {ε, c, έ, c] of the message m using the user identity id , where e = {-l)mJN{t), cW = t + -^ mod N, c∞ = ^ ^ mod N,
,ηΛ _ uRj j c^d + uRj j
ε = (-l)mJN(t), = t + - mod N, =— } mod N, where ffid = (id) , t, t G (Έ/ΝΈ)Χ , d = Qld (s), choosing random bits β1, β2 G {0,1} and setting c = c^1^ and c = c^2-1; and
transmitting the ciphertext C = {ε, c, έ, c] via a communication channel.
44. A computer program product stored in non-transitory computer-readable storage media comprising computer-executable instructions for:
receiving the ciphertext C = {ε, c, έ, c] for a user with an identity id via a communication channel; and
accessing the ciphertext C = {ε, c, έ, c] of a plaintext message m, where ε = (-l)m t), c = t + mod N,

e = {-l)mJN{i), cW = t + -=^ mod N, c∞ = _(Q) rf mod N, where N is a composite integer, ffid = (id), t, t £ (Έ/ΝΈ)Χ, d = Qld (s), c = c^1^ and c = c^2^ for random bits β1, β2 G {0,1}, wherein public system parameters m pk =
{N, u, Ή, {£/jd}, s], where N is a composite integer, u G N \ Q W, 5 is bit-string, Ή is a cryptographic hash function mapping bit- strings to elements of N and {Qld} is a family of functions mapping bit-strings to elements of a subset οΐ Έ/ΝΈ, namely Qld: {0,1}*→
/N , s B d = gid (s) such that JN(d2 - 4Jf (id)) = JN(d2 - uH (id)) = -1; and generating the message m by accessing a private key usk = {rid} for a user with an identity id by following steps:
if rid 2≡ ffid (mod N), setting v = ε, γ = c and Δ = ff id; otherwise setting v = έ, γ = c and Δ = uRld ;
determining σ = /w(y2— 4Δ),
setting
T = k((7 + 2rid)(d - 2rid)(d - y)) if = -V ^ d = ^ and determining the message m as
1— v · τ
45. A computer program product stored in non-transitory computer-readable storage media for generating keys for an identity-based cryptosystem wherein a private key is used to decrypt ciphertext C = {ε, c, έ, c] of a plaintext message m for a user with an identity id where ε = (-l)m t), cM = t + - mod N, = (0) mod N,
uRid c(0)d + AuRjd
ε = (-l)mJN(t), = t + - mod N, =— } mod N, where N is a composite integer, ffid = (id), t, t £ (Έ/ΝΈ)Χ, d = Qld (s), c = c^1^ and c = c^2^ for random bits β1, β2 G {0,1}, comprising computer-executable instructions for: setting a master secret key msk; and
generating, using the master secret key msk, the private key usk = {rid} for a user with an identity id, using public system parameters mpk = {N, u, Ή, {Q d}, s], where N is a composite integer, u G N \ Q W , 5 is bit-string, Ή is a cryptographic hash function mapping bit-strings to elements of N and {Qld} is a family of functions mapping bit-strings to elements of a subset of Έ/ΝΈ namely
£id: {0,l}*→ 1/N1, s■→ d = Qld (s such that JN(d2 - 4Jf(id)) = JN d2 - 4uJf (id)) =
Applications Claiming Priority (4)
| Application Number | Priority Date | Filing Date | Title |
|---|---|---|---|
| US201462055731P | 2014-09-26 | 2014-09-26 | |
| US62/055,731 | 2014-09-26 | ||
| US201462098391P | 2014-12-31 | 2014-12-31 | |
| US62/098,391 | 2014-12-31 |
Publications (1)
| Publication Number | Publication Date |
|---|---|
| WO2016048784A1 true WO2016048784A1 (en) | 2016-03-31 |
Family
ID=54292908
Family Applications (1)
| Application Number | Title | Priority Date | Filing Date |
|---|---|---|---|
| PCT/US2015/050670 Ceased WO2016048784A1 (en) | 2014-09-26 | 2015-09-17 | Anonymous identity-based cryptosystems |
Country Status (1)
| Country | Link |
|---|---|
| WO (1) | WO2016048784A1 (en) |
Cited By (3)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| CN105915520A (en) * | 2016-04-18 | 2016-08-31 | 深圳大学 | File storage and searching method based on public key searchable encryption, and storage system |
| CN109325361A (en) * | 2018-09-11 | 2019-02-12 | 陕西师范大学 | Searchable public key encryption method supporting inner product operation |
| CN109639425A (en) * | 2018-11-07 | 2019-04-16 | 华中科技大学 | What a kind of side calculated lightweight under environment can search for public key encryption method |
-
2015
- 2015-09-17 WO PCT/US2015/050670 patent/WO2016048784A1/en not_active Ceased
Non-Patent Citations (19)
Cited By (6)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| CN105915520A (en) * | 2016-04-18 | 2016-08-31 | 深圳大学 | File storage and searching method based on public key searchable encryption, and storage system |
| CN105915520B (en) * | 2016-04-18 | 2019-02-12 | 深圳大学 | File storage, search method and storage system based on public key searchable encryption |
| CN109325361A (en) * | 2018-09-11 | 2019-02-12 | 陕西师范大学 | Searchable public key encryption method supporting inner product operation |
| CN109325361B (en) * | 2018-09-11 | 2021-08-03 | 陕西师范大学 | Searchable public key encryption method supporting inner product operation |
| CN109639425A (en) * | 2018-11-07 | 2019-04-16 | 华中科技大学 | What a kind of side calculated lightweight under environment can search for public key encryption method |
| CN109639425B (en) * | 2018-11-07 | 2020-05-19 | 华中科技大学 | Lightweight searchable public key encryption method and storage medium in side computing environment |
Similar Documents
| Publication | Publication Date | Title |
|---|---|---|
| Rao et al. | Efficient attribute-based signature and signcryption realizing expressive access structures | |
| Fan et al. | Proxy re-encryption and re-signatures from lattices | |
| Gu et al. | New public key cryptosystems based on non‐Abelian factorization problems | |
| Hrestak et al. | Homomorphic encryption in the cloud | |
| EP3143719A1 (en) | Method and apparatus for generating shorter signatures almost tightly related to standard assumptions | |
| Hada | Secure obfuscation for encrypted signatures | |
| US9356783B2 (en) | Method for ciphering and deciphering, corresponding electronic device and computer program product | |
| Kwant et al. | Lattice klepto: Turning post-quantum crypto against itself | |
| Sedghighadikolaei et al. | A comprehensive survey of threshold signatures: NIST standards, post-quantum cryptography, exotic techniques, and real-world applications | |
| Joye | Identity-based cryptosystems and quadratic residuosity | |
| Nishimaki et al. | Key-private proxy re-encryption from lattices, revisited | |
| EP2892177A1 (en) | Proxy re-encryption methods and devices | |
| Guo et al. | Towards a secure certificateless proxy re-encryption scheme | |
| Tseng et al. | Anonymous Multireceiver Identity‐Based Encryption against Chosen‐Ciphertext Attacks with Tight Reduction in the Standard Model | |
| WO2016073059A2 (en) | Public-key encryption with keyword search | |
| Sarier | A new biometric identity based encryption scheme secure against DoS attacks | |
| Karati et al. | Efficient and provably secure random oracle‐free adaptive identity‐based encryption with short‐signature scheme | |
| Gaidhani et al. | A SURVEY REPORT ON TECHNIQUES FOR DATA CONFIDENTIALITY IN CLOUD COMPUTING USING HOMOMORPHIC ENCRYPTION. | |
| Zheng et al. | Improved anonymous proxy re-encryption with CCA security | |
| WO2016048775A1 (en) | Xor-homomorphic cryptosystems with fast key generation | |
| Hsu et al. | Oblivious transfer protocols based on commutative encryption | |
| WO2016073058A2 (en) | Method and apparatus for secure elgamal-type cryptography | |
| Gligor | Brief Encounters with a Random Key Graph: (Transcript of Discussion) | |
| Cheon et al. | A cryptanalysis of the original domingo-ferrer's algebraic privacy homomophism | |
| Cui et al. | Formal security treatments for IBE-to-signature transformation: Relations among security notions |
Legal Events
| Date | Code | Title | Description |
|---|---|---|---|
| 121 | Ep: the epo has been informed by wipo that ep was designated in this application |
Ref document number: 15778801 Country of ref document: EP Kind code of ref document: A1 |
|
| NENP | Non-entry into the national phase |
Ref country code: DE |
|
| 122 | Ep: pct application non-entry in european phase |
Ref document number: 15778801 Country of ref document: EP Kind code of ref document: A1 |