WO2015055765A1 - Method for generating a quasi-adaptive non-interactive zero-knowledge proof and corresponding electronic device - Google Patents
Method for generating a quasi-adaptive non-interactive zero-knowledge proof and corresponding electronic device Download PDFInfo
- Publication number
- WO2015055765A1 WO2015055765A1 PCT/EP2014/072222 EP2014072222W WO2015055765A1 WO 2015055765 A1 WO2015055765 A1 WO 2015055765A1 EP 2014072222 W EP2014072222 W EP 2014072222W WO 2015055765 A1 WO2015055765 A1 WO 2015055765A1
- Authority
- WO
- WIPO (PCT)
- Prior art keywords
- vector
- electronic device
- proof
- generating
- linearly homomorphic
- Prior art date
- Legal status (The legal status is an assumption and is not a legal conclusion. Google has not performed a legal analysis and makes no representation as to the accuracy of the status listed.)
- Ceased
Links
Classifications
-
- H—ELECTRICITY
- H04—ELECTRIC COMMUNICATION TECHNIQUE
- H04L—TRANSMISSION OF DIGITAL INFORMATION, e.g. TELEGRAPHIC COMMUNICATION
- H04L9/00—Cryptographic mechanisms or cryptographic arrangements for secret or secure communications; Network security protocols
- H04L9/32—Cryptographic mechanisms or cryptographic arrangements for secret or secure communications; Network security protocols including means for verifying the identity or authority of a user of the system or for message authentication, e.g. authorization, entity authentication, data integrity or data verification, non-repudiation, key authentication or verification of credentials
- H04L9/3218—Cryptographic mechanisms or cryptographic arrangements for secret or secure communications; Network security protocols including means for verifying the identity or authority of a user of the system or for message authentication, e.g. authorization, entity authentication, data integrity or data verification, non-repudiation, key authentication or verification of credentials using proof of knowledge, e.g. Fiat-Shamir, GQ, Schnorr, ornon-interactive zero-knowledge proofs
Definitions
- the disclosure relates to cryptography, and more specifically, with the development of efficient non-interactive zero-knowledge (e.g. "NIZK”) proofs of membership in hard languages.
- NIZK efficient non-interactive zero-knowledge
- PPT Probabilistic polynomial time
- CRS Common Reference String
- NIZK Non-interactive zero-knowledge (as already mentioned)
- QA-NIZK Quasi-adaptive non-interactive zero-knowledge
- DLIN Decision Linear
- SDP means Simultaneous Double Pairing
- /c-SDP means Simultaneous k -wise Pairing
- SXDH means Symmetric external Diffie-Hellman
- GS Groth-Sahai
- SPHF Smooth Projective Hash Function.
- Non-interactive zero-knowledge (NIZK) proofs play a central role in cryptography.
- NIZK Non-interactive zero-knowledge
- ⁇ f A E ⁇ ⁇ is a matrix of rank t ⁇ n (where t and n are integers, and ⁇ ⁇ is the additive group of integers modulo a prime number p), in order to prove membership in the language
- Jutla and Roy gave significantly more efficient solutions for quasi-adaptive NIZK proofs (OA-NIZK), where the common reference string (CRS) may depend on the language of which membership is being proved. While malleable in their original form (just like the Groth-Sahai proofs), the Jutla Roy OA-NIZK proofs can be modified to achieve a weak form of non-malleability called relative simulation-soundness, which is sufficient for many applications like password-authenticated key exchange protocols and chosen-ciphertext-secure non-interactive threshold encryption.
- the proposed technique aims to reduce the number of group elements in relatively sound Q.A-NIZK proofs. More precisely, the proposed technique aims to obtain a size of a proof that does not depend on the dimension of a considered subspace.
- one goal of the proposed technique is to obtain a size of the proof that should not depend on the number of equations n or on the number of variables t.
- this goal seems very difficult to achieve given that it would even outperforms Fiat-Shamir-like proofs derived from ⁇ protocols in the random oracle model, as explained in the article "Random oracles are practical: A paradigm for designing efficient protocols" by M. Bellare and P.
- references in the specification to "one embodiment”, “an embodiment”, “an example embodiment”, indicate that the embodiment described may include a particular feature, structure, or characteristic, but every embodiment may not necessarily include the particular feature, structure, or characteristic. Moreover, such phrases are not necessarily referring to the same embodiment. Further, when a particular feature, structure, or characteristic is described in connection with an embodiment, it is submitted that it is within the knowledge of one skilled in the art to affect such feature, structure, or characteristic in connection with other embodiments whether or not explicitly described.
- the present invention is directed to a method for generating a quasi-adaptive non- interactive zero-knowledge proof, said proof assessing a membership of a first vector to a hard language, which is a subspace of G n , where G is a group and n is an integer.
- the method is executed by an electronic device, and it comprises: generating a derived linearly homomorphic signature on a second vector, said second vector being defined as a function of said first vector, a linearly homomorphic signatures comprised in a common reference string and a witness associated with said first vector; and generating a non-malleable element by using a public evaluation function of a smooth projective hash function, in combination with a hash function, said first vector, said witness and elements comprised in said common reference string, said proof being a combination of said derived linearly homomorphic signature and said non-malleable element.
- the method for generating is remarkable in that said hard language corresponds to a set which is equal to E G n ⁇ x E ⁇ s.
- t. v * g x A ]
- p is a prime number
- t is an integer
- g is a generator of said group G
- A is a t x n matrix of rank t whose elements are comprised in ⁇ ⁇ .
- the method for generating is remarkable in that said linearly homomorphic signatures comprised in a common reference string comprise 2t elements, each element being defined by a vector (z, r lt ... , r k ) , where k is a integer greater or equal to two, corresponding to a linearly homomorphic signature on independent vectors, which are obtained from rows of a matrix g A .
- the method for generating according is remarkable in that generating a derived linearly homomorphic signature, and generating a non-malleable element further use a label.
- the different steps of the method are implemented by a computer software program or programs, this software program comprising software instructions designed to be executed by a data processor of a relay module according to the disclosure and being designed to control the execution of the different steps of this method.
- an aspect of the disclosure also concerns a program liable to be executed by a computer or by a data processor, this program comprising instructions to command the execution of the steps of a method as mentioned here above.
- This program can use any programming language whatsoever and be in the form of a source code, object code or code that is intermediate between source code and object code, such as in a partially compiled form or in any other desirable form.
- the disclosure also concerns an information medium readable by a data processor and comprising instructions of a program as mentioned here above.
- the information medium can be any entity or device capable of storing the program.
- the medium can comprise a storage means such as a ROM (which stands for "Read Only Memory”), for example a CD-ROM (which stands for “Compact Disc - Read Only Memory”) or a microelectronic circuit ROM or again a magnetic recording means, for example a floppy disk or a hard disk drive.
- ROM Read Only Memory
- CD-ROM Compact Disc - Read Only Memory
- microelectronic circuit ROM again a magnetic recording means, for example a floppy disk or a hard disk drive.
- the information medium may be a transmissible carrier such as an electrical or optical signal that can be conveyed through an electrical or optical cable, by radio or by other means.
- the program can be especially downloaded into an I nternet-type network.
- the information medium can be an integrated circuit into which the program is incorporated, the circuit being adapted to executing or being used in the execution of the method in question.
- an embodiment of the disclosure is implemented by means of software and/or hardware components.
- module can correspond in this document both to a software component and to a hardware component or to a set of hardware and software components.
- a software component corresponds to one or more computer programs, one or more sub-programs of a program, or more generally to any element of a program or a software program capable of implementing a function or a set of functions according to what is described here below for the module concerned.
- One such software component is executed by a data processor of a physical entity (terminal, server, etc.) and is capable of accessing the hardware resources of this physical entity (memories, recording media, communications buses, input/output electronic boards, user interfaces, etc.).
- a hardware component corresponds to any element of a hardware unit capable of implementing a function or a set of functions according to what is described here below for the module concerned. It may be a programmable hardware component or a component with an integrated circuit for the execution of software, for example an integrated circuit, a smart card, a memory card, an electronic board for executing firmware etc.
- a step of obtaining an element/value in the present document can be viewed either as a step of reading such element/value in a memory unit of an electronic device or a step of receiving such element/value from another electronic device via communication means.
- the present invention is directed to an electronic device comprising a module configured to generate a quasi-adaptive non-interactive zero-knowledge proof, said proof assessing a membership of a first vector to a hard language, which is a subspace of G n , where G is a group and n is an integer.
- Such electronic device comprises: a module configured to generate a derived linearly homomorphic signature on a second vector, said second vector being defined as a function of said first vector, a linearly homomorphic signatures comprised in a common reference string and a witness associated with said first vector;
- a module configured to generate a non-malleable element by using a public evaluation function of a smooth projective hash function, in combination with a hash function, said first vector, said witness and elements comprised in said common reference string, said proof being a combination of said derived linearly homomorphic signature and said non-malleable element.
- the electronic device is remarkable in that said linearly homomorphic signatures comprised in a common reference string comprise 2t elements, each element being defined by a vector (z, r lt ... , r k ) , where k is a integer greater or equal to two, corresponding to a linearly homomorphic signature on independent vectors, which are obtained from rows of a matrix g A .
- the electronic device is remarkable in that the module configured to generate a derived linearly homomorphic signature, and the module configured to generate a non-malleable element further use a label.
- the present invention is directed to an, an electronic device comprising a module configured to cipher in an non-interactive and adaptively secure threshold cryptosystems with chosen-ciphertext security.
- the electronic device comprises a module configured to generate a quasi-adaptive non-interactive zero-knowledge proof, said proof assessing a membership of a first vector to a hard language, which is a subspace of G n , where G is a group and n is an integer, that comprises: a module configured to generate a derived linearly homomorphic signature on a second vector, said second vector being defined as a function of said first vector, a linearly homomorphic signatures comprised in a common reference string and a witness associated with said first vector; and
- a module configured to generate a non-malleable element by using a public evaluation function of a smooth projective hash function, in combination with a hash function, said first vector, said witness and elements comprised in said common reference string, said proof being a combination of said derived linearly homomorphic signature and said non-malleable element.
- Figures 2(a)-(f) present a non-interactive threshold cryptosystem according to one embodiment of the invention
- Figure 3 presents an example of an electronic device that can be used to perform one or several steps of methods disclosed in the present document.
- a non-interactive zero-knowledge (NIZK) proof for a relation R " usually consists of three algorithms or methods noted (K, P, V), where K is a randomized algorithm (or method) that takes as input a security parameter 1 £ N (in unary) and outputs a common reference string (CRS); P is a randomized algorithm (or method) used by the prover on input of a statement x and a witness w such that l(x, w) 1 to generate a proof for the statement x E L; and the algorithm (or method) V is a deterministic algorithm (or method) which is run by the verifier to output a binary value (which is 1 if and only if the verifier is convinced that E L; and 0 otherwise) on input of the CRS, a statement x and a proof ⁇ .
- K is a randomized algorithm (or method) that takes as input a security parameter 1 £ N (in unary) and outputs a common reference string (CRS)
- P is a
- the CRS should be seen as a set of common public parameters generated by some trusted party.
- the zero-knowledge property usually refers to the existence of a simulator S that takes as input a true statement x E L but no witness. Instead of a witness, the simulator S uses a trapdoor ⁇ associated with the CRS to generate simulated proofs ⁇ whose distribution is indistinguishable from real proofs ⁇ produced by the actual algorithm P using the witness.
- the intuition is that a proof ⁇ leaks nothing beyond the validity of the statement x E L.
- Quasi-Adaptive NIZK (Q.A-NIZK) proofs are NIZK proofs where the CRS is allowed to depend on the specific language for which proofs have to be generated.
- the CRS is divided into a fixed part ⁇ , produced by an algorithm K 0 , and a language-dependent part ⁇ , produced by an algorithm However, there should be a single simulator for the entire class of languages.
- ⁇ E N be a security parameter.
- this label can include the message-carrying part (g r , M. h r ) of an Elgamal-like encryption.
- a tuple of algorithms (K Q , K lt P, V) is a Q.A-NIZK proof system for R if there exists a PPT simulator (S lt S 2 ), such that, for any PPT adversaries ⁇ 1 , ⁇ 2 and /Z 3 , the properties hereunder stands.
- quasi-adaptive completeness means that honestly generated proofs are always accepted by the verifier.
- Quasi-adaptive soundness captures that it should be computationally infeasible for the prover to trick the verifier into accepting a proof for a false statement.
- the quasi-adaptive zero-knowledge property it requires the existence of a simulator (S lt S 2 ) that can emulate the behavior of the real prover P (which always generates proofs using the witnesses) without knowing the witnesses w: instead, (S lt S 2 ) uses a simulation trapdoor T sim hidden in the CRS ⁇ to create simulated proofs. Yet, no probabilistic polynomial time (PPT) adversary should be unable to see the difference.
- PPT probabilistic polynomial time
- ⁇ ( ⁇ ,.,.) emulates the actual prover and outputs a proof ⁇ on input of (x,w) £ l p , and ZM.
- S 2 (ip,T sim ,.,.) is an oracle that takes as input x E L p (i.e. for which there exists w such that (x,w) £ 52p ) as well as a label Ibl , and outputs a simulated proof ⁇ ⁇ - ⁇ /'» T st?m x,lbfy. It is assumed that the CRS ⁇ contains an encoding of p, which is thus available to V.
- the definition of Quasi-Adaptive Zero-Knowledge requires a single simulator for the entire family of relations R.
- Reminders on Simulation-Soundness and Relative Soundness It is often useful to have a property called simulation-soundness, which requires that the adversary be unable to prove false statements even after having seen simulated proofs for possibly false statements.
- a labeled single-theorem relatively sound Q.A-NIZK proof system is comprised of a quasi- adaptive labeled proof system (Ko,K lt P, V) along with an efficient private verifier W and an efficient simulator (S lt S 2 ).
- the following properties should hold for any PPT adversaries ( ⁇ 1 , ⁇ 2 , ⁇ 3 ,, ⁇ ). Quasi Adaptive Relative Single-Theorem Zero-Knowledge:
- SDP Simultaneous Double Pairing problem
- the DLIN and the SDP problems can both be generalized to dimensions higher than three.
- Linearly homomorphic SPS schemes are homomorphic signatures where messages and signatures live in the domain group G of a bilinear map.
- the authors of this report recently described in the article "Linearly Homomorphic Structure-Preserving Signatures and their Applicgtions" by B. Libert et al., and published in the conference proceedings of Crypto 2013, the following one-time construction and proved its security under the SDP assumption.
- Verify(p/c, ⁇ , ( ⁇ 1; ...,M n )): given a purposed signature ⁇ ⁇ z,r,u) £ G 3 , and a vector (M 1; ...,M n ), return 1 if and only if (M 1; ...,M n ) ⁇ (1 G , ...,1c) / and (z,r, ) satisfy
- Sign( sk,(M lt ...,M n ) ): to sign a vector ( 1; ...,M n ) E G n using sk z,r lt ...,r k ) E G k+1 , where with; £ ⁇ 1, ...,/c ⁇ .
- SignDerive(p/c, ⁇ ⁇ ( ⁇ ): given a public key p/c as well as £ pairs ( ⁇ £ , ⁇ ), where ⁇ £ £ ⁇ ⁇ for each ⁇ , parse as (z it r i lt ... , r i k ) E G k+1 for i E ⁇ 1, ... , £ ⁇ .
- a sk (x) A pk (x,w) using the public evaluation algorithm A pk (. ).
- a sk (. ) A pk (x,w) using the public evaluation algorithm A pk (. ).
- the action of A sk (. ) on x is completely undetermined.
- the value A sfc (x) should be statistically indistinguishable from a random value.
- the language-dependent CRS contains one-time linearly homomorphic signatures on the rows of the matrix p E G txn .
- the prover can use the witness x E TL ⁇ to derive a one-time homomorphic signature ⁇ z, r, u) on v.
- the difficulty is that it is necessary to combine two seemingly conflicting requirements: first, the prover should be able to publicly derive a homomorphic signature ⁇ z, r, u) on v from signatures that are available in the CRS; second, one should prevent unwanted manipulations in the derived signature.
- v g x A
- each proof of membership (z, r, u, n Q ) E G 4 consists of a derived linearly homomorphic signature ⁇ z, r, u) on some vector that depends on v and a non-malleable part ⁇ 0 consisting of a SPHF public evaluation which is calculated as a function of the language p and the statement !?.
- the relative soundness property is guaranteed by the properties of the underlying SPHF as it implies that, even if the adversary is allowed to see exactly one simulated proof for a false statement, it will be unable to prove a false statement by itself.
- Figures l(a)-(d) present a relatively sound QA-NIZK proof system according to one embodiment of the invention.
- the initialization method (see Figure 1(a)) aims at obtaining from a security parameter l, some parameters that are used in the other methods described in Figures 1(b) -
- a E ⁇ ⁇ ⁇ can be either fixed or part of £ p so that t, n can be given as input to the CRS generation method described in Figure 1(b).
- the electronic device generates a key pair (pk ots ,sk ots ) for the one-time linearly homomophic signature, depicted in the section "d) Linearly Homomorphic Structure-Preserving Signatures" in the present document, in order to sign vectors in G 2n+1 .
- the generation of (pk ots ,sk ots ) can re-use the generator g produced in output of step 101.
- Hi (G , ... , G n , Y i ⁇ 1, ... ,1) £ G 2n+1 with i £ ⁇ 1, ... , t ⁇
- the electronic device obtains a collision-resistant hash function H: ⁇ 0,1 ⁇ * ⁇ ⁇ ⁇ to be used.
- the electronic device determines the CRS i/> which comprises a first part CRSi that is only used by the prover and a second part CRS 2 whch is only used by the verifier.
- CRS 1 (p,pk ots ,W,Y, ⁇ , , ⁇ , ⁇ ),
- CRS 2 (pk ots ,W,Y,H).
- the electronic device outputs the proof ⁇ which is equal to (z, r, u, ⁇ 0 ) E G 4 .
- the generator method system delivers a relatively sound QA-NIZK proof that only requires 0(1) group elements.
- the size of the proof does not depend on the dimension of the considered subspace.
- the electronic device verifies that the format of the received/obtained parameters is compliant with the expected one (i.e. each coordinate of the vector v must belong to the group G, the proof should have the following format (z, r, u, ⁇ 0 ) E G 4 , etc.).
- the electronic device determines if the elements
- the electronic device outputs an information (such as a value equal to 1) if the one time linearly homomorphic signature is valid.
- the electronic device verifies if the following equations stand (where are obtained from the public key pk ots generated in step 103 and comprised in the CRS ⁇ )
- the electronic device If the verification fails, the electronic device outputs a value equal to 0.
- the electronic device determines that the format of the parameters provided as input fulfill the expected rule.
- step referenced 114 the electronic device checks if the following equations stand (where are obtained from the public key pk ots generated in step 103):
- the electronic device delivers an output value equals to zero.
- the electronic device delivers an output value equals to zero if the equation is not verified. Otherwise, it delivers an output value equals to one.
- the proposed relatively sound QA-NIZK proof system readily extends to rest on the k - SDP assumption with /c > 2 .
- the only required modification is to replace the linearly homomorphic signature based on the SDP assumption by the second linearly homomorphic signature described in the section "d) Linearly Homomorphic Structure-Preserving Signatures" in the present document.
- the ⁇ z, r, u) part is thus replaced by a signature of the form (z, r lt ... , r k ) while the smooth projective hash value remains unchanged.
- the proof requires k + 2 group elements whereas combining the techniques of the articles "Relatively-Sound NIZKs and Password-Based Key-Exchange” and "Shorter Quasi-Adaptive NIZK Proofs for Linear Subspaces" requires k(n + 1— t) elements per proof. From a security standpoint, the following result can be proven: the proposed proof system is a relatively sound Q.A-NIZK proof system if the SDP assumption holds in (G, G T ) and if H is a collision-resistant hash function.
- Figures 2(a)-(f) present a non-interactive threshold cryptosystem according to one embodiment of the invention.
- the proposed threshold scheme is fully non-interactive: namely, decryption servers never have to talk to each other during the decryption process and they only send one message to a dedicated entity, called combiner, that gather the decryption shares in order to recover the plaintext.
- the key generation method (see Figure 2(a)) executed or implemented by an electronic device, takes a security parameter ⁇ , a number t, and a number N enabling to define a (t, N)- threshold encryption scheme (where t parties (or electronic devices) are required to perform the deciphering).
- the electronic device obtains a bilinear group (G, G r ) of prime order p > 2 ⁇ .
- the electronic device obtains three elements (randomly
- the electronic device obtains nine random elements in ⁇ ⁇ :
- the electronic device obtains Groth-Sahai CRS (f lt f 2 , f 3 ), to be used for providing the validity of decryption shares. More precisely, the electronic device R
- the electronic device obtains three random polynomials
- the electronic device obtains a collision-resistant hash function H: ⁇ 0,1 ⁇ * ⁇ ⁇ ⁇ .
- the public key is defined to be:
- PK ⁇ g> 7i> T2
- the electronic device determines a linearly homomorphic signature (Z,R,U) on the vector C 1 ,C 2 ,C 3 ,C 4 ,C 1 a ,C 2 a ,C 3 a ) E G 7 . More precisely, it determines such signature as follows:
- the ciphertext verify method (see Figure 2(c)) executed or implemented by an electronic device, takes in input a public key PK and a ciphertext C.
- the electronic device checks, in a step referenced 212, if the ciphertext comprises eight elements of G (i.e. the ciphertext C can be represented by (C 0 , C lt C 2 , C 3 , C ,Z,R, U) EG 8 ).
- the electronic device outputs a value equal to 1 if and only if the following equations are verified:
- the share decrypt method (see Figure 2(d)) executed or implemented by an electronic device, takes as input a public key PK, a value i, a secret key S/Q and a ciphertext C.
- the electronic device executes the method described in Figure 2(c). In the case that the result is equal to zero, then, the electronic device outputs the value i and an information, noted 1, indicating that the ciphertext is malformed.
- the commitments C PI ,C P2 , C PQ and the proof ⁇ ⁇ . are generated using the CRS
- the share verify method (see Figure 2(e)) executed or implemented by an electronic device, takes as input a public key PK, a verification key VK it a ciphertext C and the following value (i, fli) (corresponding to the output of the share decrypt method).
- the electronic device parses the ciphertext C as (C 0 , C lt C 2 , C 3 , C ,Z, R, U) E G 8 , and VKi as ( ⁇ , ⁇ ) ⁇ ⁇ £> 2 ⁇ If the ⁇ is equal to 1, or if ⁇ can not be parsed properly as ( i ,C Pi ,Cp 2 ,C Po ,n Vi ), then it outputs a value equal to 0. Otherwise it outputs a value equal to 1 if ⁇ ⁇ . is a valid proof. In other situation, it outputs a value equal to 0.
- the combine method (see Figure 2(f)) executed or implemented by an electronic device takes as input PK, VK, C, ⁇ i, fii ) ⁇ ⁇ eS .
- the threshold encryption scheme of Figures 2(a)-(f) can be proved chosen-ciphertext secure under adaptive corruptions if the DLIN assumption holds. Moreover, the security reduction is tight as, up to negligible terms, the adversary's advantage is bounded by a constant multiplied by the maximal probability of breaking the underlying assumptions.
- the following theorem can be set up: the above threshold cryptosystem is IND-CCA secure against adaptive corruptions assuming that: (i) H is collision-resistant; (ii) The DLIN assumption holds in G. More precisely, the advantage of any PPT adversary /Zis at most
- ciphertexts are further compressed by 11% while relying on the same assumption and retaining tight security.
- the improvement provided by the present technique becomes more important as the ciphertext reduces to 2k + 4 group elements. Specifically, it is needed k + 1 elements for the second homomorophic signature described in the section "d) Linegrly Homomorphic Structure-Preserving Signgtures" in the present document, another (/c + 1) elements to contain the /c-linear instance, one element for the Cramer-Shoup-like proof ⁇ 0 and one element to carry the plaintext.
- Such device referenced 300 comprises a computing unit (for example a CPU, for "Central Processing Unit"), referenced 301, and one or more memory units (for example a RAM (for "Random Access Memory”) block in which intermediate results can be stored temporarily during the execution of instructions a computer program, or a ROM block in which, among other things, computer programs are stored, or an EEPROM (“Electrically-Erasable Programmable Read-Only Memory”) block, or a flash block) referenced 302.
- Computer programs comprise instructions that can be executed by the computing unit.
- Such device 300 can also comprise a dedicated unit, referenced 303, constituting an input-output interface to allow the device 300 to communicate with other devices.
- this dedicated unit 303 can be connected with an antenna (in order to perform communication without contacts), or with serial ports (to carry communications by the use of physical contacts). It should be noted that the arrows in Figure 3 signify that the linked unit can exchange data through buses for example together.
- some or all of the steps of the method previously described can be implemented in hardware in a programmable FPGA ("Field Programmable Gate Array") component or ASIC ("Application-Specific Integrated Circuit") component.
- the previously mentioned means correspond to a dedicated circuit (such as a FPGA component or an ASIC component).
Landscapes
- Engineering & Computer Science (AREA)
- Computer Security & Cryptography (AREA)
- Computer Networks & Wireless Communication (AREA)
- Signal Processing (AREA)
- Machine Translation (AREA)
Abstract
In one embodiment, it is proposed a method for generating a quasi-adaptive non- interactive zero-knowledge proof, said proof assessing a membership of a first vector to a hard language, which is a subspace of G n , where G is a group and n is an integer. The method is executed by an electronic device, and is remarkable in that it comprises: generating a derived linearly homomorphic signature on a second vector, said second vector being defined as a function of said first vector, from a linearly homomorphic signatures comprised in a common reference string and a witness associated with said first vector; and generating a non-malleable element by using a public evaluation function of a smooth projective hash function, in combination with a hash function, said first vector, said witness and elements comprised in said common reference string, said proof being a combination of said derived linearly homomorphic signature and said non-malleable element.
Description
Method for generating a quasi-adaptive non-interactive zero-knowledge proof and corresponding electronic device
Technical Field
The disclosure relates to cryptography, and more specifically, with the development of efficient non-interactive zero-knowledge (e.g. "NIZK") proofs of membership in hard languages.
Background
This section is intended to introduce the reader to various aspects of art, which may be related to various aspects of the present invention that are described and/or claimed below. This discussion is believed to be helpful in providing the reader with background information to facilitate a better understanding of the various aspects of the present invention. Accordingly, it should be understood that these statements are to be read in this light, and not as admissions of prior art. In the rest of the document, the following acronyms, which are well known for one skilled in the art of cryptography, are used: PPT means Probabilistic polynomial time; CRS means Common Reference String; NIZK means Non-interactive zero-knowledge (as already mentioned); QA-NIZK means Quasi-adaptive non-interactive zero-knowledge; DLIN means Decision Linear; SDP means Simultaneous Double Pairing; /c-SDP means Simultaneous k -wise Pairing; SXDH means Symmetric external Diffie-Hellman; GS means Groth-Sahai and SPHF means Smooth Projective Hash Function. Some reminders on the concepts of Quasi-Adaptive NIZK Proofs, Simulation-Soundness and Relative Soundness, Bilinear Maps and Hardness Assumptions, Linearly Homomorphic Structure-Preserving Signatures, Smooth Projective Hash functions are described in the section "Detailed description of embodiments" of the present document, before the description of the figures.
Non-interactive zero-knowledge (NIZK) proofs play a central role in cryptography. Until recently, the most efficient way to non-interactively prove membership in the linear subspace spanned by vectors of group elements was to use the Groth-Sahai proof systems (the Groth-Sahai proof systems are detailed in the article "Efficient non-interactive proof systems for
bilinear groups" by J. Groth, and A. Sahai, published in the conference proceedings of Eurocrypt'08, LNCS 4965, pp. 415-432, 2008).
Indeed, \f A E ΈρΧη is a matrix of rank t < n (where t and n are integers, and Έρ is the additive group of integers modulo a prime number p), in order to prove membership in the language L = E Gn \ 3x E Έρ s. t. v* = gx A], where G is a group, and g an element of G , using NIZK proofs, the Groth-Sahai techniques require 0(n + t) group elements in their basic form.
They can be made simulation-sound by using techniques suggested in the following articles: "Simulgtion-sound NIZK proofs for g prgcticgl Igngugge gnd constgnt size group signgtures" , by J. Groth, published in the conference proceedings of Asiacrypt 2006, LNCS 4284, pp. 444-459, 2006, "A public key encryption scheme secure ggginst key dependent chosen plgintext gnd gdgptive chosen ciphertext gttgcks" by J. Camenisch et al., published in the conference proceedings of Eurocrypt'09, LNCS 5479, pages 351-368, 2009, and "Tightly Secure Public-Key Encryption" , by D. Hofheinz, T. Jager., published in the conference proceedings of Crypto 2012, LNCS series, pp. 590-607,2012.
However, these techniques involve Groth-Sahai proofs for quadratic pairing product equations, which results in rather long proofs. One-time simulation-soundness can be more efficiently achieved using techniques suggested in the following articles: "Round-Optimgl Pgssword-Bgsed Authenticgted Key Exchgnge", by J. Katz and V. Vaikuntanathan, published in the conference proceedings of TCC'll, LNCS 6597, pp. 293-310, 2011, and "Non-Interactive CCA2-Secure Threshold Cryptosystems with Adgptive Security: New Fmmework gnd Constructions" , by B. Libert, M. Yung, published in the conference proceedings of TCC 2012, LNCS 7194, pp. 75-93, Springer, 2012.
However, in recent results, Jutla and Roy gave significantly more efficient solutions for quasi-adaptive NIZK proofs (OA-NIZK), where the common reference string (CRS) may depend on the language of which membership is being proved. While malleable in their original form (just like the Groth-Sahai proofs), the Jutla Roy OA-NIZK proofs can be modified to achieve a
weak form of non-malleability called relative simulation-soundness, which is sufficient for many applications like password-authenticated key exchange protocols and chosen-ciphertext-secure non-interactive threshold encryption.
Indeed, Jutla and Roy suggested an even more efficient way to achieve single-theorem relative soundness in the article : "Relatively-Sound NIZKs and Password-Based Key-Exchange" by C. Jutla and A. Roy published in the conference proceedings of PKC'12, LNCS series, pp. 485- 503, 2012. More recently in the article "Shorter Quasi-Adaptive NIZK Proofs for Linear Subspaces" , by C. Jutla, A. Roy, published in the conference proceedings of Asiacrypt'13, LNCS series, 2013 and in the Cryptology ePrint Archive: Report 2013/109, 2013, C. Jutla and A. Roy showed how to make the proofs more compact at the expense of settling for computational soundness (rather than perfect soundness described in the previous mentioned article "Efficient non-interactive proof systems for bilinear groups"). Still, in their most efficient variant, the Jutla-Roy proofs still require 0(n— t) group elements, which remains linear in n and results in long proofs when t « n. Hence, to prove membership in a linear subspace of dimension t spanned by vectors of dimension n, the relatively sound Q.A-NIZK proofs of Jutla and Roy require 0(n— t) group elements.
The proposed technique aims to reduce the number of group elements in relatively sound Q.A-NIZK proofs. More precisely, the proposed technique aims to obtain a size of a proof that does not depend on the dimension of a considered subspace.
Indeed, the proposed technique aims to construct a relatively Q.A-NIZK proof system for a language corresponding to the following set: [v* E Gn \ x E Έρ s. t. v* = gxA] by using proofs made of a constant number of group elements. In other words, one goal of the proposed technique is to obtain a size of the proof that should not depend on the number of equations n or on the number of variables t. At first, this goal seems very difficult to achieve given that it would even outperforms Fiat-Shamir-like proofs derived from∑ protocols in the random oracle
model, as explained in the article "Random oracles are practical: A paradigm for designing efficient protocols" by M. Bellare and P. Rogaway, and published in the ACM CCS, pp. 62-73, 1993. Indeed, the Fiat-Shamir heuristic would give 0(t) size proofs here, as the length of proofs is inevitably linear in the number of variables. Summary of invention
References in the specification to "one embodiment", "an embodiment", "an example embodiment", indicate that the embodiment described may include a particular feature, structure, or characteristic, but every embodiment may not necessarily include the particular feature, structure, or characteristic. Moreover, such phrases are not necessarily referring to the same embodiment. Further, when a particular feature, structure, or characteristic is described in connection with an embodiment, it is submitted that it is within the knowledge of one skilled in the art to affect such feature, structure, or characteristic in connection with other embodiments whether or not explicitly described.
The present invention is directed to a method for generating a quasi-adaptive non- interactive zero-knowledge proof, said proof assessing a membership of a first vector to a hard language, which is a subspace of Gn, where G is a group and n is an integer. The method is executed by an electronic device, and it comprises: generating a derived linearly homomorphic signature on a second vector, said second vector being defined as a function of said first vector, a linearly homomorphic signatures comprised in a common reference string and a witness associated with said first vector; and generating a non-malleable element by using a public evaluation function of a smooth projective hash function, in combination with a hash function, said first vector, said witness and elements comprised in said common reference string, said proof being a combination of said derived linearly homomorphic signature and said non-malleable element. In a preferred embodiment, the method for generating is remarkable in that said hard language corresponds to a set which is equal to E Gn \ x E Έρ s. t. v* = gx A], where p is a
prime number, t is an integer, g is a generator of said group G, and A is a t x n matrix of rank t whose elements are comprised in Έρ.
In a preferred embodiment, the method for generating according is remarkable in that said witness x belongs to Έρ, and is associated with said first vector ~v by a relationship ~v = gxA.
In a preferred embodiment, the method for generating is remarkable in that said linearly homomorphic signatures comprised in a common reference string comprise 2t elements, each element being defined by a vector (z, rlt ... , rk) , where k is a integer greater or equal to two, corresponding to a linearly homomorphic signature on independent vectors, which are obtained from rows of a matrix gA.
In a preferred embodiment, the method for generating according is remarkable in that generating a derived linearly homomorphic signature, and generating a non-malleable element further use a label.
In another embodiment, it is proposed a method for ciphering in an non-interactive and adaptively secure threshold cryptosystems with chosen-ciphertext security. Such method is executed by an electronic device, and is remarkable in that it comprises executing a method for generating a quasi-adaptive non-interactive zero knowledge proof as mentioned previously.
According to an exemplary implementation, the different steps of the method are implemented by a computer software program or programs, this software program comprising software instructions designed to be executed by a data processor of a relay module according to the disclosure and being designed to control the execution of the different steps of this method.
Consequently, an aspect of the disclosure also concerns a program liable to be executed by a computer or by a data processor, this program comprising instructions to command the execution of the steps of a method as mentioned here above.
This program can use any programming language whatsoever and be in the form of a source code, object code or code that is intermediate between source code and object code, such as in a partially compiled form or in any other desirable form.
The disclosure also concerns an information medium readable by a data processor and comprising instructions of a program as mentioned here above.
The information medium can be any entity or device capable of storing the program. For example, the medium can comprise a storage means such as a ROM (which stands for "Read Only Memory"), for example a CD-ROM (which stands for "Compact Disc - Read Only Memory") or a microelectronic circuit ROM or again a magnetic recording means, for example a floppy disk or a hard disk drive.
Furthermore, the information medium may be a transmissible carrier such as an electrical or optical signal that can be conveyed through an electrical or optical cable, by radio or by other means. The program can be especially downloaded into an I nternet-type network.
Alternately, the information medium can be an integrated circuit into which the program is incorporated, the circuit being adapted to executing or being used in the execution of the method in question.
According to one embodiment, an embodiment of the disclosure is implemented by means of software and/or hardware components. From this viewpoint, the term "module" can correspond in this document both to a software component and to a hardware component or to a set of hardware and software components.
A software component corresponds to one or more computer programs, one or more sub-programs of a program, or more generally to any element of a program or a software program capable of implementing a function or a set of functions according to what is described here below for the module concerned. One such software component is executed by a data processor of a physical entity (terminal, server, etc.) and is capable of accessing the hardware resources of this physical entity (memories, recording media, communications buses, input/output electronic boards, user interfaces, etc.).
Similarly, a hardware component corresponds to any element of a hardware unit capable of implementing a function or a set of functions according to what is described here below for the module concerned. It may be a programmable hardware component or a component with an integrated circuit for the execution of software, for example an integrated circuit, a smart card, a memory card, an electronic board for executing firmware etc.
It should also be noted that a step of obtaining an element/value in the present document can be viewed either as a step of reading such element/value in a memory unit of an electronic device or a step of receiving such element/value from another electronic device via communication means. In another embodiment, the present invention is directed to an electronic device comprising a module configured to generate a quasi-adaptive non-interactive zero-knowledge proof, said proof assessing a membership of a first vector to a hard language, which is a subspace of Gn, where G is a group and n is an integer. Such electronic device comprises: a module configured to generate a derived linearly homomorphic signature on a second vector, said second vector being defined as a function of said first vector, a linearly homomorphic signatures comprised in a common reference string and a witness associated with said first vector;
a module configured to generate a non-malleable element by using a public evaluation function of a smooth projective hash function, in combination with a hash function, said first vector, said witness and elements comprised in said common reference string, said proof being a combination of said derived linearly homomorphic signature and said non-malleable element.
In a preferred embodiment, the electronic device is remarkable in that said hard language corresponds to a set which is equal to E Gn \ x E Έρ s. t. v* = gx A], where p is a prime number, t is an integer, g is a generator of said group G, and A is a t x n matrix of rank t whose elements are comprised in TLV .
In a preferred embodiment, the electronic device is remarkable in that said witness x belongs to Έρ, and is associated with said first vector ~v by a relationship ~v = gxA.
In a preferred embodiment, the electronic device is remarkable in that said linearly homomorphic signatures comprised in a common reference string comprise 2t elements, each element being defined by a vector (z, rlt ... , rk) , where k is a integer greater or equal to two, corresponding to a linearly homomorphic signature on independent vectors, which are obtained from rows of a matrix gA.
In a preferred embodiment, the electronic device is remarkable in that the module configured to generate a derived linearly homomorphic signature, and the module configured to generate a non-malleable element further use a label.
In another embodiment, the present invention is directed to an, an electronic device comprising a module configured to cipher in an non-interactive and adaptively secure threshold cryptosystems with chosen-ciphertext security. The electronic device comprises a module configured to generate a quasi-adaptive non-interactive zero-knowledge proof, said proof assessing a membership of a first vector to a hard language, which is a subspace of Gn, where G is a group and n is an integer, that comprises: a module configured to generate a derived linearly homomorphic signature on a second vector, said second vector being defined as a function of said first vector, a linearly homomorphic signatures comprised in a common reference string and a witness associated with said first vector; and
a module configured to generate a non-malleable element by using a public evaluation function of a smooth projective hash function, in combination with a hash function, said first vector, said witness and elements comprised in said common reference string, said proof being a combination of said derived linearly homomorphic signature and said non-malleable element.
Brief description of the figures
The above and other aspects of the invention will become more apparent by the following detailed description of exemplary embodiments thereof with reference to the attached drawings in which: - Figures l(a)-(d) present a relatively sound QA-NIZK proof system according to one embodiment of the invention;
Figures 2(a)-(f) present a non-interactive threshold cryptosystem according to one embodiment of the invention;
Figure 3 presents an example of an electronic device that can be used to perform one or several steps of methods disclosed in the present document.
Detailed description of embodiments
First of all, before describing in details some embodiments of the invention, some reminders related to concepts related to the background of the present technique are detailed: a) Reminders on Quasi-Adaptive NIZK Proofs Let l be a relation that takes as input a statement x and a witness w such that l(x, w) = 1 if and only if x belongs to the language £. It should be noted that only languages £ where it may be hard to distinguish random elements of £ from elements outside £ are considered for cryptographic purposes. For example, consider an abelian group G =< g > of prime order p where the discrete logarithm problem is hard. If A E Ί η is a matrix of rank t < n, deciding the membership of a linear subspace gA E Gtxn is believed to be hard for carefully chosen groups: in other words, the language
L = {v* E Gn \ 3x E TLv t s. t. 'v = gi A] is not efficiently recognizable. For such languages, proving the membership of a candidate x E £ is non-trivial. Whenever x E £, any element w such that l(x, w) = 1 is called a witness for the membership of x in £.
A non-interactive zero-knowledge (NIZK) proof for a relation R " usually consists of three algorithms or methods noted (K, P, V), where K is a randomized algorithm (or method) that takes as input a security parameter 1 £ N (in unary) and outputs a common reference string (CRS); P is a randomized algorithm (or method) used by the prover on input of a statement x and a witness w such that l(x, w) = 1 to generate a proof for the statement x E L; and the algorithm (or method) V is a deterministic algorithm (or method) which is run by the verifier to output a binary value (which is 1 if and only if the verifier is convinced that E L; and 0 otherwise) on input of the CRS, a statement x and a proof π. The CRS should be seen as a set of common public parameters generated by some trusted party. The zero-knowledge property usually refers to the existence of a simulator S that takes as input a true statement x E L but no witness. Instead of a witness, the simulator S uses a trapdoor τ associated with the CRS to generate simulated proofs π whose distribution is indistinguishable from real proofs π produced by the actual algorithm P using the witness. The intuition is that a proof π leaks nothing beyond the validity of the statement x E L. Quasi-Adaptive NIZK (Q.A-NIZK) proofs are NIZK proofs where the CRS is allowed to depend on the specific language for which proofs have to be generated. The CRS is divided into a fixed part Γ, produced by an algorithm K0, and a language-dependent part ψ, produced by an algorithm However, there should be a single simulator for the entire class of languages.
More formally, let λ E N be a security parameter. For public parameters Γ produced by algorithm K0 , let T>r be a probability distribution over a collection of relations R = {ftp} parameterized by a string p with an associated language Lp = [x\ 3w s. t. lp (x, w) = l).
In the following, it is considered proof systems where the prover and the verifier both take a label Ibl as additional input. For example, this label can include the message-carrying part (gr, M. hr) of an Elgamal-like encryption. A tuple of algorithms (KQ, Klt P, V) is a Q.A-NIZK proof system for R if there exists a PPT simulator (Slt S2), such that, for any PPT adversaries Λ1, Λ2 and /Z3, the properties hereunder stands.
In short, quasi-adaptive completeness means that honestly generated proofs are always accepted by the verifier. Quasi-adaptive soundness captures that it should be computationally infeasible for the prover to trick the verifier into accepting a proof for a false statement. As for the quasi-adaptive zero-knowledge property, it requires the existence of a simulator (SltS2) that can emulate the behavior of the real prover P (which always generates proofs using the witnesses) without knowing the witnesses w: instead, (SltS2) uses a simulation trapdoor Tsim hidden in the CRS ψ to create simulated proofs. Yet, no probabilistic polynomial time (PPT) adversary should be unable to see the difference.
Quasi-Adaptive Completeness:
Pr[ Γ <- K0(A); ρ^νν;ψ ^ Κ^Γ,ρ);
(x,w,lbl) <- Λ^Υ,-φ,ρ); π <- P(ip,x,w,lbl) s.t. V(ip,x,n,lbl) = 1 ί!Μρ(χ, w) = 1] = 1.
Quasi-Adaptive Soundness:
Pr[ Γ <- K„(A); p <- Dr; ip <- Κ^Γ,ρ); {x,w,lbl) <- <A2(T,xp,p) s.t. V(xp,x,n,lbl) = 1 Λ -i (3w s. t. Kp(x, w) = 1] Enegl( ) .
Quasi-Adaptive Zero-Knowledge:
Pr[ Γ <- K0(l) ; p <- 2)r ; ψ <-
 = 1] * ΡΓ[Γ <- Κ„(λ) ; ρ <- Dr; (ip,Tsim) <- S^p) s. t «Ζ3 ¾(ψ'τ*™'-'^,^ρ) = 1, where:
Ρ(ψ,.,.) emulates the actual prover and outputs a proof π on input of (x,w) £ lp, and ZM.
S2(ip,Tsim,.,.) is an oracle that takes as input x E Lp (i.e. for which there exists w such that (x,w) £ 52p ) as well as a label Ibl , and outputs a simulated proof π <- Ο/'» Tst?m x,lbfy.
It is assumed that the CRS ψ contains an encoding of p, which is thus available to V. The definition of Quasi-Adaptive Zero-Knowledge requires a single simulator for the entire family of relations R. b) Reminders on Simulation-Soundness and Relative Soundness It is often useful to have a property called simulation-soundness, which requires that the adversary be unable to prove false statements even after having seen simulated proofs for possibly false statements.
Unbounded Simulation-Soundness: For any PPT adversary Λ , it holds that
Pr[ r ^ K0(l) ; ^ 2)Γ ; (ψ, τείιη) <- S1(r, p) ; {x, w, Ibl) <- Λ^τ - r, xp, p) s. t. V(ip, x, π, Ibl) = 1 Λ -i (3w s. t. Jlp (x, w) = 1) A(x, π, Ibl) g Q] E negl( ) . where the adversary is allowed unbounded access to an oracle S2 ( p, Tsirn, . , . ) that takes as input statement-label pairs x, Ibl) (where x may be outside Lp) and outputs simulated proofs π <- S2 (ip, Tsim, x, Ibl), before updating the set Q = Q\J{(x, n, Ibl)} which is initially empty. In the weaker notion of one-time simulation-soundness, only one query to the S2 oracle is allowed. In some applications (such as password-authenticated key exchange and chosen- ciphertext secure public-key encryption with publicly verifiable ciphertexts), one may settle for a weaker notion, called relative soundness by Jutla and Roy and described in the previous mentioned article entitled: "Relatively-Sound NIZKs and Password-Based Key-Exchange" , which allows for more efficient proofs, especially in the single theorem case. Informally, relatively sound proof systems involve both a public verifier and a private verification algorithm, which has access to a trapdoor. For hard languages, the two verifiers should almost always agree on any adversarially-created proof.
Moreover, the private verifier should not accept a non-trivial proof for a false statement, even if the adversary has already seen proofs for false statements.
A labeled single-theorem relatively sound Q.A-NIZK proof system is comprised of a quasi- adaptive labeled proof system (Ko,KltP, V) along with an efficient private verifier W and an efficient simulator (SltS2). Moreover, the following properties should hold for any PPT adversaries (Λ1,Λ2,Λ3,,Λ ). Quasi Adaptive Relative Single-Theorem Zero-Knowledge:
Pr[ Γ <- K„(A);p <- Z>r; ψ <-

P x ,p,x,w,lbl) s.t^2 -:) i,s = 1] « Pr[T <- K„(A); p <- Dr;
(ψ,τ) <- SiCr. ) ; (x,w,ZM,s) <- Λ ^^^'^ίΥ,ψ,ρ ; = 1;
π <- 52 p, τ, x, ZM) s. t. ,/^ ^·-) s) = i], Quasi Adaptive Relative Single-Theorem Simulation-Soundness:

S2 (^,p, τ, x, IbQ s. t. (χ', M, π') <- «^«^-Ό with (χ,π,ΙΜ) ≠ (χ',π',ΙΜ') A3w's.t.¾(i ') = 1 AW(xp,T,x' ,ΙΜ' ,π') = 1] Enegl(X). c) Reminders on Bilinear Maps and Hardness Assumptions For simplicity, symmetric bilinear maps e: G x G→ GT over groups of prime order p are used, but extensions to the asymmetric setting e: G x G→ GT are possible if an efficiently computable isomorphism Ψ: G→ G is available. Modulo slight changes, the proposed technique can also work without such an isomoprhism but, in this case, they rely on somewhat less standard cryptographic assumptions. The following definition of the Decision Linear Problem (DLIN) in the group G of order p, also described in the article "Short group signatures" , by D. Boneh et al., published in the conference proceedings of Crypto'04, LNCS 3152, pp.41-55, 2004, can be stated as follows: the Decision Linear Problem (DLIN) is to distinguish between the distributions
R R
{g>ga>gb>gac>gbd>gc+d) and {g,ga,gb,gac,gbd,gz), with a,b,c,d <- TLV, Z <- TLV, and g a generator of the group G.
The Decision Linear Assumption is the intractability of DLIN for any PPT distinguisher Ί .
The DLIN problem can be viewed as the problem of deciding whether three vectors (ga> 1G> 9 > G> 9b> g)> (gab> gcd> gz) f°rm a subspace of dimension two (which is the case when z = c + d) or three. Sometimes it is used in the present document the notion of Simultaneous Double
Pairing (SDP) assumption, which is weaker than DLIN. As noted in the article "Group Encryption: Non-Interactive Realization in the Standard Model" by J. Cathalo et al., and published in the conference proceedings of Asiacrypt'09, LNCS 5912, pp. 179-196, 2009, any algorithm solving SDP immediately yields a DLIN distinguisher. The following definition of the Simultaneous Double Pairing problem (SDP) in (G, GR) can be formulated as follows: given group elements (gz, gr , hz, hu) E G4, the SDP problem is to find a non-trivial triple {z, r, u) E G3\{(1Gj 1Gj such that e(gz, z). e(gr, r) = 1G and e(hz, z). e hu, u) = lGr.
The DLIN and the SDP problems can both be generalized to dimensions higher than three.
Indeed, as described in the article "A Cramer-Shoup encryption scheme from the linear assumption and from progressively weaker linear variants" by H. Shacham, published in the Cryptology ePrint Archive: Report 2007/074, 2007, the k -Linear Problem (/ -LIN) in G is the problem of distinguishing the distributions
£>i = {(gi> - > gk> g> giai> - , #/ , g^=1 i ) e G2k+2 \glt ... , gk, g *- G, ¾, ... , ak t- zp} and
£>2 = {(gi> - , gu> g. giai> - , guak. gz ) &2k+2
 TLV j.
For each k≥ 2, the k -Linear Problem is known to remain generically hard even in the presence of an oracle that solves the (/c— 1) linear problem. The following assumption which is implied by the k -LIN assumption can be stated:
The Simultaneous k -wise Pairing ( k -SDP) problem is, given a random tuple ({di,z'— ' 9k,z> 9i,r>— ' 9k,r ) es <^2/£ > t0 find a non-trivial vector (z, rlt ... , rk ) E Gk+1 such that e(gj>z,z).e(gj>r,rj) = lGr with £ {1, ...,k}, and z ≠ 1G.
Considerer a /c-linar instance (glir,—,gk,r>9i,rai >—>9k ,ra > V ) e G2k+1 , where the goal is to decide if η = t. For any non-trivial tuple z,r, ...,rk ) E Gk+1 satisfying the equalities e(gjiZ aj,
 = 1G for each j E {1, ... ,k], the following relationship stands:
Hence, any algorithm solving k -SDP with non-negligible probability immediately implies a k -linear distinguisher. d) Linearly Homomorphic Structure-Preserving Signatures
Linearly homomorphic SPS schemes are homomorphic signatures where messages and signatures live in the domain group G of a bilinear map. The authors of this report recently described in the article "Linearly Homomorphic Structure-Preserving Signatures and their Applicgtions" by B. Libert et al., and published in the conference proceedings of Crypto 2013, the following one-time construction and proved its security under the SDP assumption.
Keygen(A, n): given a security parameter and the dimension n E N of vectors to be
, R
signed, (G,GT) of prime order p > 2 . Choose gz,gr,hz,hu <-G. Then, for i = 1 to n, pick Χί,Υί,δι <-Έρ, and compute gi = gz Xigr Yi and ht = hz lhu 1. The private key sk = (fey SJUi) while the public key is pk =

Sign(sfc, (Afi,
compute and return
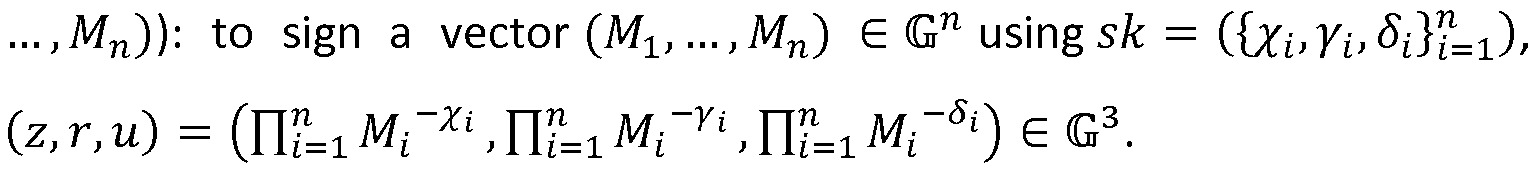 SignDerive(p/c, {ο)(,σ^}._ι ): given a public key p/c as well as £ pairs (ω£, σ^), where ω£ ε Έρ for each i, parse σ*·1-1 as σ*·1-1 = (z£jr£j £) £ G3 for i £ {1, ...,- }. Then, compute and return σ = {z,r,u), where z =

Verify(p/c, σ, (Μ1; ...,Mn)): given a purposed signature σ = {z,r,u) £ G3, and a vector (M1; ...,Mn), return 1 if and only if (M1; ...,Mn)≠ (1G, ...,1c)/ and (z,r, ) satisfy
IGT = e(^z,z).e(^r,r).nf=ie(^,Mi);and lGr = e{hz,z).e hu,u).\[l=1e{hi,Mi).
One particularity of this scheme is that, even if the private key is available, it is difficult to find two distinct signatures on the same vector if the SDP assumption holds: by dividing out the two signatures, one obtains the solution of an SDP instance (gz, gr, hz, hu) contained in the public key.
Under the /c-SDP assumption, the one-time linearly homomorphic structure-preserving signature previously described can be extended as follows.
Keygen(A, n): given a security parameter and the dimension n E N of vectors to be
, R signed, (G, GT) of prime order p > 2 . For j = 1 to k, choose generators gj z, gj r <- G. Then,
R
fori = lton, = 1 to k pick χι,Υα <- Έρ, and compute gji = gjiZ Xigj,rYi,i- The private key sk =

Sign( sk,(Mlt ...,Mn) ): to sign a vector ( 1; ...,Mn) E Gn using sk = z,rlt ...,rk) E Gk+1, where
 with; £ {1, ...,/c}. SignDerive(p/c, {ωί(σ^} ): given a public key p/c as well as £ pairs (ω£, σ^), where ω£ £ Έρ for each ί, parse as = (zit ri lt ... , ri k) E Gk+1 for i E {1, ... , £}. Then, compute and return σ = {z,r ,—,rk), where z =
 for j E {1, ...,k}.
Verify(p/c, σ, (M1} ...,Mn)): given σ = (z,r1} ...,rk)) E Gk+1, and a vector (M1; ...,Mn), return 1 if and only if (Μ1; ... , Mn)≠ ... , and, for each j E {1, ... , k], the following equation holds:
IGT = ε(¾ζ- e(.9j,r>ri)- Π?=ι e(gj,i,Mi). ej Smooth Projective Hash functions
Introduced by Cramer and Shoup, in the article "Universal Hash Proofs and a Paradigm for Adaptive Chosen Ciphertext Secure PublicKey Encryption" . published in the conference proceedings of Eurocrypt'02, LNCS 2332, pp.45-64, 2002, smooth projective hash functions (SPHF) are primitives where a secret key sk is mapped to a projective hashing key pk = ^λ:). Such a function involves two distinct hashing algorithms (Asfc(. ),Apfc(.)) such that, for any element* £ L, the action of Ask(.) on x is completely determined bγpk = μ sk). In particular, the witness w such that l(x, w) = 1 allows publicly computing Ask(x) as
Ask(x) = Apk(x,w) using the public evaluation algorithm Apk(. ). However, for any x g L, the action of Ask(. ) on x is completely undetermined. For anyx g L, given pk = ^λ:), the value Asfc(x) should be statistically indistinguishable from a random value. The intuition is that, for a given pk = ^λ:), there are many equally likely private keys sk, each of which gives a different private evaluation ASk(x) when x g L.
A simple example of SPHF based on the DLIN assumption works as follows. The private key is of the form sk = (x0,x1,x2 ) E Έρ 3 and the projective key is
 where f,g,h E G are public generators. The language LDLIN is the set of
£DLIN = {(fr,hs,gr+s) E G3\r,s Έρ}
of vectors that live in a two-dimensional subspace. Under the DLIN assumption, this language is clearly indistinguishable from random vectors of G3. For any (Vlt V2, V3) E LDLIN, the private evaluation is computed as Ask(ylt V2, V3) = V1 XlV2 X2V3 x° . This private evaluation is publicly computable by anyone who knows the witness w = (r, s) E Έρ 2 such (fr, hs, gr+s) E G3. Indeed, it equals Λ^, Ι^) = Α3Μ,ν2, ν3, (r, s)) = Y^Y S .
In contrast, if (V1, V2, V3 £ £>DLIN > tne private evaluation Λ^Ι^, V2, V3) = V^ ^W 0 is completely undetermined from pk = μθ/c) = (Y1, Y2 ) = (fXlgx°, hX2gx°) , because pk leaks no information about x. The latter SPHF readily extends to the language of k - linear tuples.
As in the Cramer-Shoup cryptosystem, described in the article "A practical public key cryptosystem provably secure against adaptive chosen ciphertext attack", published in the conference proceedings of Crypto'98, LNCS 1462, pp. 13-25, 1998, 2-universal SPHFs are used in the following: given pk = ^λ:) , for any distinct χ, χ' g £ the joint distribution of {Ask(x), Ask (x')} is statistically indistinguishable from a pair of random values in the range of ASk (x)- This is typically achieved by combining an ordinary SPHF with a collision-resistant hash function. f) After having given some reminders that are going to ease the understanding of embodiments of the invention, gnd before describing the Figures, the genergl concept of the invention can be described gs follows:
In the previous mentioned article "Relgtively-Sound NIZKs gnd Pgssword-Bgsed Key- Exchgnge", Jutla and Roy described a single-theorem relatively sound NIZK proof system that combines the Groth-Sahai proofs and the smooth projective hash functions of Cramer and Shoup. Smooth projective hash functions can be seen as designated verifier non-interactive zero-knowledge proofs: while they are only convincing to a specific verifier (as the verification algorithm requires the knowledge of the private verification trapdoor), they do provide a form of onetime simulation-soundness. In contrast, the Groth-Sahai (GS) proofs are publicly verifiable but they are malleable and do not provide relative soundness. However, Jutla and Roy
showed that GS proofs become relatively sound if they are suitably combined with a smooth- projective hash function. The relatively sound proofs can thus be seen as a clever combination of malleable publicly verifiable proofs and privately verifiable non-malleable proofs. The proposed technique relies on the idea of modifying the Jutla-Roy relatively sound proofs described in the previous mentioned articles "Relatively-Sound NIZKs and Password-Based Key- Exchange" and "Shorter Quasi-Adaptive NIZK Proofs for Linear Subspaces" , by modifying their underlying malleable components and replacing them by one-time linearly homomorphic signatures. However, combining one-time linearly homomorphic signatures and smooth projective hash functions is non-trivial, as explained in the present document. The present technique is built on the homomorphic signature as the ones depicted in the section "d) Linearly Homomorphic Structure-Preserving Signgtures" in the present document. Specifically, the language-dependent CRS contains one-time linearly homomorphic signatures on the rows of the matrix p E Gtxn. For each vector v E Lp, the prover can use the witness x E TL^ to derive a one-time homomorphic signature {z, r, u) on v. I n order to obtain the sought-after relative simulation-soundness property, the difficulty is that it is necessary to combine two seemingly conflicting requirements: first, the prover should be able to publicly derive a homomorphic signature {z, r, u) on v from signatures that are available in the CRS; second, one should prevent unwanted manipulations in the derived signature. In particular, for a given honestly generated proof of some statement v = gx A, no one should be able to derive a proof for a related statement (ρ', ν') or a new proof for the same statement.
To achieve this, properties of a 2-universal SPHF should be used : each proof of membership (z, r, u, nQ) E G4 consists of a derived linearly homomorphic signature {z, r, u) on some vector that depends on v and a non-malleable part π0 consisting of a SPHF public evaluation which is calculated as a function of the language p and the statement !?. More precisely, the SPHF evaluation π0 calculated as a function of a hash value = H(p, v) E Έρ of the pair (p, v) where H: {0,1}*→ Έρ is an ordinary collision-resistant hash function. The relative soundness property is guaranteed by the properties of the underlying SPHF as it implies that, even if the adversary is allowed to see exactly one simulated proof for a
false statement, it will be unable to prove a false statement by itself. Indeed, the 2-universal property of the underlying SPHF guarantees that, for any two distinct vectors v, v' E Gn outside the linear span of gA E Gtxn , the private evaluation algorithm Ask (. ) yields pairwise independent private evaluations: given pk = ^λ:), the joint distribution {Ask (v), Ask (v')} is statistically indistinguishable from random. Hence, even if the adversary is given Ask(v) as part of a simulated proof of membership for i;, it is unable to predict the proof π0' = Ask (v') that would make the private verifier accept π0' in a proof of membership for i?'. Since the private verifier and the public verifier almost always agree if the DLIN assumption holds, the proof system is guaranteed to be as sound to the public verifier as it is to the private one. Finally, in order to prevent anyone from turning a proof for some statement (p, v) into a different proof of the same statement, the following property also described, in the section "d) Linearly Homomorphic Structure-Preserving Signatures" in the present document, that two distinct signatures on the same vector immediately give a solution to the SDP problem, is used.
By having the prover carefully embed a = H(p, v) E Έρ in the vector for which it computes a derived signature, it can be made sure that:
(i) The correctness of the public SPHF evaluation π0 becomes publicly verifiable;
(ii) The adversary cannot falsely prove the membership of a vector outside the row space of gA E Gtxn even after having seen one such simulated proof; (iii) The adversary will be unable to maul an observed proof in order to obtain a proof for some related statement.
Figures l(a)-(d) present a relatively sound QA-NIZK proof system according to one embodiment of the invention.
In the following, vectors are always considered as row vectors unless stated otherwise. If .4 £ ZpXnis a matrix, ^ E Gtxndenotes the matrix obtained by exponentiating g using the entries of A.
We consider public parameters Γ = (G, GT, g) consisting of bilinear groups (G, GT) with a generator g E G. Like in the article "Shorter Quasi-Adaptive NIZK Proofs for Linear Subspaces" , we consider languages
Lp = {g*A E I x £ ¾ } that are parameterized by p = gA E Gtxn, where A E Zpxnis a t x n matrix such that t < n.
As in the article "Shorter Quasi-Adaptive NIZK Proofs for Linear Subspaces" , it is assumed that the distribution T>r is efficiently samplable: namely, there exists a PPT algorithm which outputs a pair (p, A) describing a relation ^ and its associated language Lp according to the
R
distribution T)v. One such distribution is obtained by picking a uniform matrix .4 <- Zp and computing = gA E Gtxn.
Under the DLIN assumption, it can be constructed a relatively sound Q.A-NIZK proof system where each proof only requires 4 group elements. Under the k -linear assumption, the proof length amounts to 0 (/c) elements for a CRS of size 0(/cn).
As in the article "Relatively-Sound NIZKs and Password-Based Key-Exchange" , relative soundness (using smooth projective hash functions) is achieved. To this end, it is needed to encode the matrix p = gA E Gtxn as a It x (2n + 1).
The initialization method (see Figure 1(a)) aims at obtaining from a security parameter l, some parameters that are used in the other methods described in Figures 1(b) -
(e).
More precisely, in a step, referenced 101, an electronic device obtain a symmetric bilinear groups (G, GT) of prime order p > 2λ with g a randomly chosen element in the group G. Then, it is outputted the set of parameters Γ = (G, GT, g).
Again, the dimensions A E Ζρ χη can be either fixed or part of £p so that t, n can be given as input to the CRS generation method described in Figure 1(b).
The CRS generation method (see Figure 1(b)), executed or implemented by an electronic device, takes as input the set of parameters Γ as well as a parameter = (Gi;)1≤i≤t 1≤;≤n E Gtxn.
In a step referenced 102, the electronic device obtains/chooses randomly two n-vectors d and e defined as follows: d = (dlt ... , dn) E ¾, and e = (elt ... , en) E ¾, in order to define
the elements W = (Wlt...,Wt) = gAAT £ Gf and Ϋ = (Ylt...,Yt) = gA§T £ Gf . These elements are used later to define a projective hash function.
Then, in a step referenced 103, the electronic device generates a key pair (pkots,skots) for the one-time linearly homomophic signature, depicted in the section "d) Linearly Homomorphic Structure-Preserving Signatures" in the present document, in order to sign vectors in G2n+1. Let pkots = (G,GT),gz,gr,hz,hu,{gi,hi} ^1) be the public key and let skots = (_{Xi,Yi,
 be the corresponding private key. For simplicity, the generation of (pkots,skots) can re-use the generator g produced in output of step 101.
Then, in a step referenced 104, the electronic device uses the secret key skots in order to generate one-time linearly homomorphic signatures {(z^r^ ιΐ;)}2^ on the following independent vectors, which are obtained from the rows of the matrix p = (Gi;)1≤i≤t 1≤;≤n:
Hi = (G , ... , G n, Yi} 1, ... ,1) £ G2n+1 with i £ {1, ... , t}
Ft = (1, ... X W Gi , ... , G n) £ G2n+1 with i £ {1, ... , t}.
Then, in a step referenced 105, the electronic device obtains a collision-resistant hash function H: {0,1}*→ Έρ to be used.
Then, in a step referenced 106, the electronic device determines the CRS i/> which comprises a first part CRSi that is only used by the prover and a second part CRS2whch is only used by the verifier. These are defined as
CRS1 = (p,pkots,W,Y, {^, ,η^^,Η),
CRS2 = (pkots,W,Y,H).
The simulation trapdoor Tsim is skots = {{χι,Υί, ^J2^1) and the private verification trapdoor is τν = [d, e .
The proof generator method (see Figure 1(c)), executed or implemented by an electronic device, takes as input a candidate vector v being equal to ( lt ... , vn) £ Gn, a witness x being equal to (xlt ...,xt) £ Έρ such that v = gxA , a label Ibl and elements Γ and ψ previously defined.
In a step referenced 107, the electronic device determines the value of a = H(p,v,lbl) £ Zp.
Then, in a step referenced 108, the electronic device, using the linearly homomorphic signatures {(zi; r^ ii;)}2^ comprised in the CRS, derives a one-time linearly homomorphic signature {z, r, u) on the vector v = ( lt ... , vn, nQ, v a, ... , vn a) E G2n+1 , where π0 =

Then, the electronic device outputs the proof π which is equal to (z, r, u, π0) E G4.
Hence, the generator method system delivers a relatively sound QA-NIZK proof that only requires 0(1) group elements. The size of the proof does not depend on the dimension of the considered subspace.
The public verification method (see Figure 1(d)) executed or implemented by an electronic device, takes as input a vector v being equal to ( lt ... , vn) E Gn, a proof π , the CRS ψ previously defined, the witness x being equal to (x1; ... , xt) E Έρ such that v = gx A , a label Ibl and element Γ = (G, <&T, g).
In a step, referenced 109, the electronic device verifies that the format of the received/obtained parameters is compliant with the expected one (i.e. each coordinate of the vector v must belong to the group G, the proof should have the following format (z, r, u, π0) E G4, etc.).
Then, in a step, referenced 110, the electronic device determines the following value: a = H(p, v, lbl) E Έρ, and, it determines the vector v = ( lt ... , vn, nQ, v a , ... , vn a) E G2n+1.
Then, in a step, referenced 111, the electronic device determines if the elements
{z, r, u) comprised in said received/obtained proof π corresponds to a valid one time linearly homomorphic signature on the vector v = ( lt ... , vn, π0, v a, ... , vn a) E G2n+1 .
The electronic device outputs an information (such as a value equal to 1) if the one time linearly homomorphic signature is valid. In the step 111, the electronic device verifies if the following equations stand (where
 are obtained from the public key pkots generated in step 103 and comprised in the CRS ψ)
1<GT = e{gz, z). e{gr, r) e{gt. gf+n+1, Vi ). e(gn+1, n0);
1<GT = e{hz, z). e{hu, u) .Π?=ι β(¾ΐ. /ι"+η+1, νΐ ). e(/in+1, 7r0).
If the verification fails, the electronic device outputs a value equal to 0.
The private verification method (see Figure 1(e)) executed or implemented by an electronic device, takes as a vector v being equal to ( lt ... , vn) E Gn, a proof π , a label Ibl and elements Γ and ψ previously defined, and the element τν which corresponds to the verification trapdoor comprising the vectors d and e : d = (dlt ... , dn) E Έρ, and e = (elt ... , en) E Έρ .
In a step, referenced 112, the electronic device determines that the format of the parameters provided as input fulfill the expected rule.
Then, in a step, referenced 113, the electronic device determines the value of a = H(p, v, lbl) E TLV.
In a step referenced 114, the electronic device checks if the following equations stand (where
 are obtained from the public key pkots generated in step 103):
1<GT = e(gz, z). e(gr,
 e(gi. gi+n+1, vi ). e(gn+1, n0); lGr = e(hz, z). e(hu, u) W^ e ii. h +^ Vt ). e(hn+1, n0).
If the check fails (i.e. at least one of the equation is not verified), the electronic device delivers an output value equals to zero.
Then, in a step referenced 115, the electronic device determines if π0 =
Π;=ι v. 1 .The electronic device delivers an output value equals to zero if the equation is not verified. Otherwise, it delivers an output value equals to one.
The proposed relatively sound QA-NIZK proof system readily extends to rest on the k - SDP assumption with /c > 2 . The only required modification is to replace the linearly homomorphic signature based on the SDP assumption by the second linearly homomorphic signature described in the section "d) Linearly Homomorphic Structure-Preserving Signatures" in the present document. In each proof, the {z, r, u) part is thus replaced by a signature of the form (z, rlt ... , rk) while the smooth projective hash value remains unchanged. In this case, the
proof requires k + 2 group elements whereas combining the techniques of the articles "Relatively-Sound NIZKs and Password-Based Key-Exchange" and "Shorter Quasi-Adaptive NIZK Proofs for Linear Subspaces" requires k(n + 1— t) elements per proof. From a security standpoint, the following result can be proven: the proposed proof system is a relatively sound Q.A-NIZK proof system if the SDP assumption holds in (G, GT) and if H is a collision-resistant hash function.
Figures 2(a)-(f) present a non-interactive threshold cryptosystem according to one embodiment of the invention.
Indeed, as detailed in the present section, it can be constructed an adaptively secure CCA2-secure non-interactive threshold cryptosystem based on the DLIN assumption. Adaptively secure threshold cryptosystems with chosen-ciphertext security (in the sense of article "Non-
 C. Rackoff, D. Simon, and published in the conference proceedings of Crypto'91, LNCS 576, pp. 433-444, 1991) were previously proposed in the article "Adgptively Secure Threshold Cryptogrgphy: Introducing Concurrency, Removing Erasures" by S. Jarecki, A. Lysyanskaya, in the conference proceedings of Eurocrypt'OO, LNCS 1807, pp. 221-242, 2000, and in the article "Adgptively Secure Feldmgn VSS gnd Applicgtions to Universglly-Composgble Threshold Cryptogrgphy" by M. Abe, S. Fehr, published in the conference proceedings of Crypto'04, LNCS 3152, pp. 317- 334, 2004, but they require some interaction during the decryption process. Non-interactive solutions were put forth in the three following articles: "Threshold Public-Key Encryption with
 B. Qjn et al., published in the conference proceedings of ICICS'10, LNCS 6476, pp. 62-76, 2010, "Adgptively Secure Non-Interactive Threshold Cryptosystems" by B. Libert and M. Yung, published in the conference proceedings of ICALP 2011, LNCS 6756, pp. 588-600, 2011, and "Non-Interactive CCA2-Secure Threshold Cryptosystems with Adaptive Security: New Framework and Constructions" \i by B. Libert and M. Yung, published in the conference proceedings TCC 2012, LNCS 7194, pp. 75-93, Springer, 2012.
But, as detailed in the following, they are less efficient than the proposed technique. Under the /c-linear assumption, if compared to previous constructions based on the same
assumption, the proposed technique (related to Figures 2(a)-(f)) shortens ciphertexts by O (/c) group elements. This result is important as non-interactive threshold schemes can potentially serve as building blocks for protocols in the multi-linear setting (see the article "Candidate Multilinear Maps from Ideal Lattices" b S. Garg et al., published in the conference proceedings of Eurocrypt 2013, LNCS series, pp. 1-17, 2013, and the article "Practical Multilinear Maps over the Integers" by J.-S. Coron et al., published in the conference proceedings of Crypto 2013). Indeed, the (/c— l)-linear problem is easy in groups equipped with a k -linear map (as shown in the article "An Algebraic Framework for Diffie-Hellman Assumptions" \i A. Escala et al., published in the conference proceedings of Crypto 2013, LNCS 8043, pp. 129-147, 2013) but instantiations where the k -linear assumption holds (as seems to be the case in the previous mentioned article "Pmcticgl Multilinegr Mgps over the Integers") can be used.
The proposed threshold scheme is fully non-interactive: namely, decryption servers never have to talk to each other during the decryption process and they only send one message to a dedicated entity, called combiner, that gather the decryption shares in order to recover the plaintext.
The key generation method (see Figure 2(a)) executed or implemented by an electronic device, takes a security parameter λ, a number t, and a number N enabling to define a (t, N)- threshold encryption scheme (where t parties (or electronic devices) are required to perform the deciphering).
In a step referenced 201, the electronic device obtains a bilinear group (G, Gr) of prime order p > 2λ.
In a step referenced 202, the electronic device obtains three elements (randomly
R
generated) that belong to the group G: g, f, h <- G.
In a step referenced 203, the electronic device obtains nine random elements in Έρ :
R R R
Q, \, X2 <- TLV , Ύθ' Ύΐ' Ύ2 *~ ¾ a r,d wo> wlt w2 <- Έρ . Then, it determines the six following elements: Xi =
 # Wi = fwl gWo a nd W2 = hW2gw° .
In a step referenced 204, the electronic device obtains Groth-Sahai CRS (flt f2 , f3), to be used for providing the validity of decryption shares. More precisely, the electronic device
R
obtains two elements chosen randomly in the group G:fx,f <- G, as well as two elements chosen randomly in Έρ: φ1, φ2 <- Zp. Then the Groth-Sahai CRS ( j, /2 , f3) are determined as follows:

In a step referenced 205, the electronic device obtains three random polynomials
P0[Z],P1[Z],P2[Z] E Zp[Z]of degree t - 1, such that P„(0) = x0, ^ι(Ο) = *i and P2(0) = x2- Then, the following elements are determined: Xtl =

fori = ltoN.
In a step referenced 206, the electronic device obtains a collision-resistant hash function H: {0,1}*→ Έρ.
In a step referenced 207, the electronic device generates/obtains a key pair for the one time linearly homomorphic signature depicted in the section "d) Linearly Homomorphic Structure-Preserving Signatures" in the present document, with n = 7. The public key is equal to (gz, gr,hz,hu,{gi,hi}7 i=1) and the corresponding private key is {χι,Ύι, 5J7 =1.
In a step referenced 208, the electronic device generates/determines/obtains one-time linearly homomorphic signatures [Zj, Rj, Uj ^ on the following linearly independent vectors: hi = (f, 1, g, Y1} 1, 1, 1) E G7X2 = (1, h, g, Y2, 1, 1, 1) £ G7,
hi= (1,1,1, Wi,/, l,g E G7 = (1,1, 1, W2,l, h, g) E G7.
In a step referenced 209, the electronic device determines the vector of private key shares as being SK = SKlt ...,SKN) with SKt = {P0{i),P1{i),P2{i)) e 1p 3 for each i E {1, ...,N}.The corresponding vector VK = VKlt ...,VKN) of verification keys is defined in such way that VKi = (Χι^,Χι^) E G2, for each i E {1, ...,N}. The public key is defined to be:
PK = {g> 7i> T2, h, Xi, X2, Yi, Y2, Wlt W2, gz, gr, hz, hu, {g /j7 =1, {Zjt Rjt Uj j=i> H) .
The encryption method (see Figure 2(b)) executed or implemented by an electronic device, takes as input a message M E Gand a public key being defined as follows: PK =
{g> 7i> T2, h> Xi> X2> Yi> Y2, Wi, W2, gz, gr, hz, hu, {gb /ij7 =1, {Zj, Rj, Uj† , H).
Then, in a step referenced 210, the electronic device obtains two random elements in
R
Έρ: θχ, θ2 <- Zp. It determines the following elements:
C0 = M.X^.X^, C = f9 C2 = he C3 = g9^ and
C4 = (W^Y^ (W2 aY2)9^, where a = H(C0, Clt C2, C3) £ Zp.
Then, in a step referenced 211, the electronic device determine a linearly homomorphic signature (Z,R,U) on the vector C1,C2,C3,C4,C1 a,C2 a,C3 a) E G7. More precisely, it determines such signature as follows:
z— Δ1 .z2 z3 z4 ;
p _ ηθι ηθ2 ηθι-α ηθ2-α. υ = υ υ2 2υ ιαυ 2α.
Then, the electronic device delivers the ciphertext C = (C0, Clt C2, C3, C , Z, R, U) E G8.
The ciphertext verify method (see Figure 2(c)) executed or implemented by an electronic device, takes in input a public key PK and a ciphertext C.
The electronic device checks, in a step referenced 212, if the ciphertext comprises eight elements of G (i.e. the ciphertext C can be represented by (C0, Clt C2, C3, C ,Z,R, U) EG8).
The electronic device determines the value of a = H(CQ, Clt C2, C3) E Έρ.
The electronic device outputs a value equal to 1 if and only if the following equations are verified:
1<GT = e(gz,Z).e(gr,R) .i\=1 e(gt.gf+ , Ct ). e(g4, C4); lGr = e(hz,Z).e(hu,U) .nLi
 Q).
Hence, (Z, R, U) must be a valid linearly homomorphic signature on the vector
(Clt C2, C3, C , C^, C2 a , C3 a) E G7. Otherwise, the electronic device outputs a value equal to zero.
The share decrypt method (see Figure 2(d)) executed or implemented by an electronic device, takes as input a public key PK, a value i, a secret key S/Q and a ciphertext C. The secret key must be represented as follows: S/Q =
 e ¾3·
In a step, referenced 214, the electronic device executes the method described in Figure 2(c). In the case that the result is equal to zero, then, the electronic device outputs the value i and an information, noted 1, indicating that the ciphertext is malformed. Otherwise, the electronic device executes the step referenced 215 which comprises the step of determining fit = ( i,Cpi,Cp2,Cp0, v.), which consists of a partial decryption vt =

commitments CPQ, CPI, C?2 respectively to Ρ0(ί),Ρ1(ί),Ρ2(0' anc' a proof πν. that the following equations are satisfied:
Vi = Cfl(0. C2 ¾( . °ω, X 1 = fWlgW) and Xi>2 = hp \gp^\
The commitments CPI,CP2, CPQ and the proof πν. are generated using the CRS
The share verify method (see Figure 2(e)) executed or implemented by an electronic device, takes as input a public key PK, a verification key VKit a ciphertext C and the following value (i, fli) (corresponding to the output of the share decrypt method).
In a step referenced 216, the electronic device parses the ciphertext C as (C0, Clt C2, C3, C ,Z, R, U) E G8, and VKi as (Χι^,Χι^) ε <£>2· If the έ is equal to 1, or if έ can not be parsed properly as ( i,CPi,Cp2,CPo,nVi), then it outputs a value equal to 0. Otherwise it outputs a value equal to 1 if πν. is a valid proof. In other situation, it outputs a value equal to 0.
The combine method (see Figure 2(f)) executed or implemented by an electronic device takes as input PK, VK, C, { i, fii )}έ eS.
In a step referenced 217, for each i E S, the electronic device parses the corresponding decryption share έ as (yi,CPl,Cp2,Cp0,nv '), and return 1, if the share verify method described in Figure 2(e) outputs a value equal to zero. Otherwise, the electronic device determines v = Πί ES Ν£ΔΊ,5(·0')) which equalsv = C^.C^.C^0 = X^.X^and in turn reveals the plaintext M = C0/v.
The threshold encryption scheme of Figures 2(a)-(f) can be proved chosen-ciphertext secure under adaptive corruptions if the DLIN assumption holds. Moreover, the security reduction is tight as, up to negligible terms, the adversary's advantage is bounded by a constant multiplied by the maximal probability of breaking the underlying assumptions.
The following theorem can be set up: the above threshold cryptosystem is IND-CCA secure against adaptive corruptions assuming that: (i) H is collision-resistant; (ii) The DLIN assumption holds in G. More precisely, the advantage of any PPT adversary /Zis at most
Αάν{Λ)≤ AdvCR-hash{X) + 3. AdvDLIN (X) +

where the first term of the right-hand-side member accounts for the maximal advantage of any PPT collision-finding algorithm for H.
If each element has a 256-bit representation on BN curves (as in the article "Pairing- Friendly Elliptic Curves of Prime Order" by P. Barreto, M. Naehrig, published in the conference proceedings of SAC'05, LNCS 3897, pp. 319-331, 2005) at the 128-bit security level, the ciphertext overhead amounts to 1792 bits. The DLIN-based scheme described in the previous mentioned article "Non-Interactive CCA2-Secure Threshold Cryptosystems with Adaptive Security: New Framework and Constructions" has a ciphertext overhead comprised of 14 group elements and a one-time signature with its verification key (or 4864 bits using Groth's one-time signature; see the article "Simulation-sound NIZK proofs for a practical language and constant size group signgtures" by J. Groth, published in the conference proceedings of Asiacrypt 2006, LNCS 4284, pp. 444-459, 2006). The recent results of Escala et al. (in the previous mentioned article "An Algebmic Fmmework for Diffie-Hellmgn Assumptions" allow reducing this overhead to 3328 bits. The very recent techniques of Jutla and Roy (in the previous mentioned article "Shorter Qugsi-Adgptive NIZK Proofs for Linegr Subspgces") - which also work in the threshold setting although it was not explicitly stated in the previous mentioned article "Shorter Qugsi- Adgptive NIZK Proofs for Linegr Subspgces"- lead to ciphertexts comprised of 9 group elements under the DLIN assumption and 3k + 3 under the /c-linear assumption. Under DLIN, ciphertexts are further compressed by 11% while relying on the same assumption and retaining tight security. Under the /c-linear assumption, the improvement provided by the present technique becomes more important as the ciphertext reduces to 2k + 4 group elements. Specifically, it is needed k + 1 elements for the second homomorophic signature described in the section "d) Linegrly Homomorphic Structure-Preserving Signgtures" in the present document, another
(/c + 1) elements to contain the /c-linear instance, one element for the Cramer-Shoup-like proof π0 and one element to carry the plaintext. This allows saving 0 (/c) group elements with respect to the techniques described in the previous mentioned article "Relatively-Sound NIZKs and Password-Based Key-Exchange" , which require 3k + 3 group elements per ciphertext. In addition to this, the present technique may find applications in other protocols where decryption capabilities should be shared among several parties. Examples include auction protocols and privacy-preserving targeted advertising protocols (see the article "Targeted Advertising . . . And Privacy Too" by A. Juels, published in the conference proceedings of CT- RSA'01, LNCS 2020, pp. 408-424, 2001, for example). Figure 3 presents an example of a device that can be used to perform one or several steps of methods disclosed in the present document.
Such device referenced 300 comprises a computing unit (for example a CPU, for "Central Processing Unit"), referenced 301, and one or more memory units (for example a RAM (for "Random Access Memory") block in which intermediate results can be stored temporarily during the execution of instructions a computer program, or a ROM block in which, among other things, computer programs are stored, or an EEPROM ("Electrically-Erasable Programmable Read-Only Memory") block, or a flash block) referenced 302. Computer programs comprise instructions that can be executed by the computing unit. Such device 300 can also comprise a dedicated unit, referenced 303, constituting an input-output interface to allow the device 300 to communicate with other devices. In particular, this dedicated unit 303 can be connected with an antenna (in order to perform communication without contacts), or with serial ports (to carry communications by the use of physical contacts). It should be noted that the arrows in Figure 3 signify that the linked unit can exchange data through buses for example together. In an alternative embodiment, some or all of the steps of the method previously described, can be implemented in hardware in a programmable FPGA ("Field Programmable Gate Array") component or ASIC ("Application-Specific Integrated Circuit") component. In
another embodiment of the invention, the previously mentioned means correspond to a dedicated circuit (such as a FPGA component or an ASIC component).
In an alternative embodiment, some or all of the steps of the method previously described, can be executed on an electronic device comprising memory units and processing units as the one disclosed in the Figure 3.
Claims
1. Method for generating a quasi-adaptive non-interactive zero-knowledge proof, said proof assessing a membership of a first vector to a hard language, which is a subspace of Gn, where G is a group and n is an integer, said method being executed by an electronic device, and being characterized in that it comprises:
generating a derived linearly homomorphic signature on a second vector, said second vector being defined as a function of said first vector, a linearly homomorphic signatures comprised in a common reference string and a witness associated with said first vector; and
generating a non-malleable element by using a public evaluation function of a smooth projective hash function, in combination with a hash function, said first vector, said witness and elements comprised in said common reference string, said proof being a combination of said derived linearly homomorphic signature and said non-malleable element.
2. Method for generating according to claim 1, characterized in that said hard language corresponds to a set which is equal to E Gn \ x E Έρ s. t. v* = gxA], where p is a prime number, t is an integer, g is a generator of said group G, and A is a t x n matrix of rank t whose elements are comprised in Έρ .
3. Method for generating according to claim 2, characterized in that said witness x belongs to Έρ, and is associated with said first vector ~v by a relationship
4. Method for generating according to any claims 2 to 3, characterized in that said linearly homomorphic signatures comprised in a common reference string comprise 2t elements, each element being defined by a vector (z, rlt ... , rk) , where k is a
integer greater or equal to two, corresponding to a linearly homomorphic signature on independent vectors, which are obtained from rows of a matrix gA.
Method for generating according to any claims 1 to 4, characterized in that generating a derived linearly homomorphic signature, and generating a non- malleable element further use a label.
Method for ciphering in an non-interactive and adaptively secure threshold cryptosystems with chosen-ciphertext security, said method being executed by an electronic device, and being characterized in that it comprises executing a method for generating a quasi-adaptive non-interactive zero knowledge proof according to claims 1 to 5.
A computer-readable and non-transient storage medium storing a computer program comprising a set of computer-executable instructions to implement a method for cryptographic computations when the instructions are executed by a computer, wherein the instructions comprise instructions, which when executed, configure the computer to perform a method for generating a quasi-adaptive non- interactive zero-knowledge proof of claims 1 to 5, and/or to perform a method ciphering in an non-interactive and adaptively secure threshold cryptosystems with chosen-ciphertext security of claim 6.
Electronic device comprising a module configured to generate a quasi-adaptive non- interactive zero-knowledge proof, said proof assessing a membership of a first vector to a hard language, which is a subspace of Gn, where G is a group and n is an integer, said electronic device being characterized in that it comprises:
a module configured to generate a derived linearly homomorphic signature on a second vector, said second vector being defined as a function of said first vector, a linearly homomorphic signatures comprised in a common reference string and a witness associated with said first vector; and
a module configured to generate a non-malleable element by using a public evaluation function of a smooth projective hash function, in combination with a hash function, said first vector, said witness and elements comprised in said common reference string, said proof being a combination of said derived linearly homomorphic signature and said non-malleable element.
9. Electronic device according to claim 8, characterized in that said hard language corresponds to a set which is equal to E Gn\ x Ε ρ s. t. v* = gx A], where p is a prime number, t is an integer, g is a generator of said group G, and A is a t x n matrix of rank t whose elements are comprised in Έρ.
10. Electronic device according to claim 9, characterized in that said witness x belongs to Έρ, and is associated with said first vector ~v by a relationship ~v = gxA.
11. Electronic device according to any claims 8 to 9, characterized in that said linearly homomorphic signatures comprised in a common reference string comprise 2t elements, each element being defined by a vector (z, rlt ... , rk) , where k is a integer greater or equal to two, corresponding to a linearly homomorphic signature on independent vectors, which are obtained from rows of a matrix gA.
12. Electronic device according to any claims 8 to 11, characterized in that the module configured to generate a derived linearly homomorphic signature, and the module configured to generate a non-malleable element further use a label.
13. Electronic device comprising a module configured to cipher in an non-interactive and adaptively secure threshold cryptosystems with chosen-ciphertext security, said electronic device being characterized in that it comprises a module configured to generate a quasi-adaptive non-interactive zero-knowledge proof, said proof
assessing a membership of a first vector to a hard language, which is a subspace of Gn, where G is a group and n is an integer, that comprises:
a module configured to generate a derived linearly homomorphic signature on a second vector, said second vector being defined as a function of said first vector, a linearly homomorphic signatures comprised in a common reference string and a witness associated with said first vector; and
a module configured to generate a non-malleable element by using a public evaluation function of a smooth projective hash function, in combination with a hash function, said first vector, said witness and elements comprised in said common reference string, said proof being a combination of said derived linearly homomorphic signature and said non-malleable element.
Applications Claiming Priority (2)
| Application Number | Priority Date | Filing Date | Title |
|---|---|---|---|
| EP13306419.6 | 2013-10-16 | ||
| EP13306419 | 2013-10-16 |
Publications (1)
| Publication Number | Publication Date |
|---|---|
| WO2015055765A1 true WO2015055765A1 (en) | 2015-04-23 |
Family
ID=49709578
Family Applications (1)
| Application Number | Title | Priority Date | Filing Date |
|---|---|---|---|
| PCT/EP2014/072222 Ceased WO2015055765A1 (en) | 2013-10-16 | 2014-10-16 | Method for generating a quasi-adaptive non-interactive zero-knowledge proof and corresponding electronic device |
Country Status (1)
| Country | Link |
|---|---|
| WO (1) | WO2015055765A1 (en) |
Cited By (4)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| CN109245897A (en) * | 2018-08-23 | 2019-01-18 | 北京邮电大学 | A kind of node authentication method and device based on noninteractive zero-knowledge proof |
| CN116112181A (en) * | 2023-01-17 | 2023-05-12 | 中国科学院软件研究所 | A general non-interactive zero-knowledge proof method and system |
| US20240154811A1 (en) * | 2022-10-27 | 2024-05-09 | QPQ Ltd. | System and method for proving membership of subset from given set and linear operation therefor |
| WO2024139196A1 (en) * | 2022-12-28 | 2024-07-04 | 声龙(新加坡)私人有限公司 | Matrix computation apparatus and method for marlin zero-knowledge proof protocol, and device |
-
2014
- 2014-10-16 WO PCT/EP2014/072222 patent/WO2015055765A1/en not_active Ceased
Non-Patent Citations (30)
| Title |
|---|
| "A practical public key cryptosystem provablv secure against adaptive chosen ciphertext attack", CONFERENCE PROCEEDINGS OF CRYPTO'98, LNCS 1462, 1998, pages 13 - 25 |
| "Universal Hash Proofs and a Paradiam for Adaptive Chosen Ciphertext Secure PublicKey Encrvption", CONFERENCE PROCEEDINGS OF EUROCRYPT'02, LNCS 2332, 2002, pages 45 - 64 |
| A. ESCALA ET AL.: "An Algebraic Framework for Diffie-Hellman Assumptions", CONFERENCE PROCEEDINGS OF CRYPTO 2013, LNCS 8043, 2013, pages 129 - 147 |
| A. JUELS: "Taraeted Advertising ... And Privacy Too", CONFERENCE PROCEEDINGS OF CT-RSA'01, LNCS 2020, 2001, pages 408 - 424 |
| B. LIBERT ET AL.: "Linearly Homomorphic Structure-Preservina Signatures and their Applications", CONFERENCE PROCEEDINGS OF CRYPTO, 2013 |
| B. LIBERT; M. YUNG: "Adaptively Secure Non-Interactive Threshold Crvptosvstems", CONFERENCE PROCEEDINGS OF ICALP 2011, LNCS 6756, 2011, pages 588 - 600 |
| B. LIBERT; M. YUNG: "conference proceedings of TCC 2012, LNCS 7194", 2012, SPRINGER, article "Non-Interactive CCA2-Secure Threshold Cryptosystems with Adaptive Security: New Framework and Constructions", pages: 75 - 93 |
| B. LIBERT; M. YUNG: "conference proceedings TCC 2012, LNCS 7194", 2012, SPRINGER, article "Non-Interactive CCA2-Secure Threshold Cryptosystems with Adaptive Security: New Framework and Constructions", pages: 75 - 93 |
| B. QIN ET AL.: "Threshold Public-Key Encryption with Adaptive Security and Short Ciphertexts", CONFERENCE PROCEEDINGS OF ICICS'10, LNCS 6476, 2010, pages 62 - 76 |
| C. JUTLA; A. ROY, CRYPTOLOGY EPRINT ARCHIVE: REPORT 2013/109, 2013 |
| C. JUTLA; A. ROY: "Relcitively-Sound NIZKs and Password-Based Key-Exchange", CONFERENCE PROCEEDINGS OF PKC'12, LNCS SERIES, 2012, pages 485 - 503 |
| C. JUTLA; A. ROY: "Shorter Quasi-Adaptive NIZK Proofs for Linear Subspaces", CONFERENCE PROCEEDINGS OF ASIACRYPT'13, LNCS SERIES, 2013 |
| C. RACKOFF; D. SIMON: "Non-Interactive Zero-Knowledae Proof of Knowledge and Chosen Ciphertext Attack", CONFERENCE PROCEEDINGS OF CRYPTO'91, LNCS 576, 1991, pages 433 - 444 |
| CHARANJIT JUTLA ET AL: "Relatively-Sound NIZKs and Password-Based Key-Exchange", INTERNATIONAL ASSOCIATION FOR CRYPTOLOGIC RESEARCH,, vol. 20120925:212556, 4 September 2012 (2012-09-04), pages 1 - 47, XP061006379 * |
| D. BONEH ET AL.: "Short aroup sianatures", CONFERENCE PROCEEDINGS OF CRYPTO'04, LNCS 3152, 2004, pages 41 - 55 |
| D. HOFHEINZ; T. JAGER.: "Tightly Secure Public-Key Encryption", CONFERENCE PROCEEDINGS OF CRYPTO 2012, LNCS SERIES, 2012, pages 590 - 607 |
| H. SHACHAM: "A Cramer-Shoup encryption scheme from the linear assumption and from progressively weaker linear variants", CRYPTOLOGY EPRINT ARCHIVE: REPORT 2007/074, 2007 |
| J. CAMENISCH ET AL.: "A public key encryption scheme secure against key dependent chosen plaintext and adaptive chosen ciphertext attacks", CONFERENCE PROCEEDINGS OF EUROCRYPT'09, LNCS 5479, 2009, pages 351 - 368 |
| J. CATHALO ET AL.: "Group Encryption: Non-Interactive Realization in the Standard Model", CONFERENCE PROCEEDINGS OF ASIACRYPT'09, LNCS 5912, 2009, pages 179 - 196 |
| J. GROTH: "Simulation-sound NIZK proofs for a practical language and constant size group sianatures", CONFERENCE PROCEEDINGS OF ASIACRYPT 2006, LNCS 4284, 2006, pages 444 - 459 |
| J. GROTH; A. SAHAI: "Efficient non-interactive proof systems for bilinear aroups", CONFERENCE PROCEEDINGS OF EUROCRYPT'08, LNCS 4965, 2008, pages 415 - 432 |
| J. KATZ; V. VAIKUNTANATHAN: "Round-Optimal Password-Based Authenticated Key Exchange", CONFERENCE PROCEEDINGS OF TCC'11, LNCS 6597, 2011, pages 293 - 310 |
| J.-S. CORON ET AL.: "Practical Multilinear Maps over the Inteaers", CONFERENCE PROCEEDINGS OF CRYPTO, 2013 |
| JUTLA CHARANJIT S ET AL LI XUE XUELIIOTATEE UQ EDU AU THE UNIVERSITY OF QUEENSLAND SCHOOL OF INFORMATION TECHNOLOGY AND ELECTRONIC: "Shorter Quasi-Adaptive NIZK Proofs for Linear Subspaces", 11 September 2013, LECTURE NOTES IN COMPUTER SCIENCE; [LECTURE NOTES IN COMPUTER SCIENCE], SPRINGER VERLAG, DE, PAGE(S) 1 - 20, ISSN: 0302-9743, XP047183040 * |
| M. ABE; S. FEHR: "Adaptively Secure Feldman VSS and Applications to Universallv-Composable Threshold Cryptoaraphy", CONFERENCE PROCEEDINGS OF CRYPTO'04, LNCS 3152, 2004, pages 317 - 334 |
| M. BELLARE; P. ROGAWAY: "Random oracles are practical: A paradiam for designing efficient protocols", ACM CCS, 1993, pages 62 - 73 |
| NUTTAPONG ATTRAPADUNG ET AL: "Efficient Completely Context-Hiding Quotable and Linearly Homomorphic Signatures", 26 February 2013, PUBLIC-KEY CRYPTOGRAPHY PKC 2013, SPRINGER BERLIN HEIDELBERG, BERLIN, HEIDELBERG, PAGE(S) 386 - 404, ISBN: 978-3-642-36361-0, XP047022603 * |
| P. BARRETO; M. NAEHRIG: "Pairing- - Friendly Elliptic Curves of Prime Order", CONFERENCE PROCEEDINGS OF SAC'05, LNCS 3897, 2005, pages 319 - 331 |
| S. GARG ET AL.: "Candidate Multilinear Maps from Ideal Lattices", CONFERENCE PROCEEDINGS OF EUROCRYPT 2013, LNCS SERIES, 2013, pages 1 - 17 |
| S. JARECKI; A. LYSYANSKAYA: "Adaptively Secure Threshold Cryptography: Introducing Concurrency, Removing Erasures", CONFERENCE PROCEEDINGS OF EUROCRYPT'00, LNCS 1807, 2000, pages 221 - 242 |
Cited By (6)
| Publication number | Priority date | Publication date | Assignee | Title |
|---|---|---|---|---|
| CN109245897A (en) * | 2018-08-23 | 2019-01-18 | 北京邮电大学 | A kind of node authentication method and device based on noninteractive zero-knowledge proof |
| CN109245897B (en) * | 2018-08-23 | 2020-06-19 | 北京邮电大学 | A node authentication method and device based on non-interactive zero-knowledge proof |
| US20240154811A1 (en) * | 2022-10-27 | 2024-05-09 | QPQ Ltd. | System and method for proving membership of subset from given set and linear operation therefor |
| US12401513B2 (en) * | 2022-10-27 | 2025-08-26 | QPQ Ltd. | System and method for proving membership of subset from given set and linear operation therefor |
| WO2024139196A1 (en) * | 2022-12-28 | 2024-07-04 | 声龙(新加坡)私人有限公司 | Matrix computation apparatus and method for marlin zero-knowledge proof protocol, and device |
| CN116112181A (en) * | 2023-01-17 | 2023-05-12 | 中国科学院软件研究所 | A general non-interactive zero-knowledge proof method and system |
Similar Documents
| Publication | Publication Date | Title |
|---|---|---|
| Camenisch et al. | Batch verification of short signatures | |
| Zhou et al. | Certificateless key‐insulated generalized signcryption scheme without bilinear pairings | |
| EP2860905A1 (en) | Method for ciphering a message via a keyed homomorphic encryption function, corresponding electronic device and computer program product | |
| KR20230024369A (en) | Creation of Secret Shares | |
| US10326602B2 (en) | Group signatures with probabilistic revocation | |
| US20150100794A1 (en) | Method for signing a set of binary elements, and updating such signature, corresponding electronic devices and computer program products | |
| WO2012115671A1 (en) | Digital signatures | |
| EP3627367B1 (en) | Subversion resilient attestation for trusted execution environments | |
| US9356783B2 (en) | Method for ciphering and deciphering, corresponding electronic device and computer program product | |
| CN102263639B (en) | Certification device, authentication method and signature creating device | |
| CN103444128B (en) | Key PV signature | |
| López-García et al. | A pairing-based blind signature e-voting scheme | |
| Asaar et al. | A short ID‐based proxy signature scheme | |
| Chen et al. | From σ-protocol based signatures to ring signatures: general construction and applications | |
| Chatterjee et al. | Mutual Authentication Protocol Using Hyperelliptic Curve Cryptosystem in Constrained Devices. | |
| Junru | The improved elliptic curve digital signature algorithm | |
| Zhang et al. | Short computational Diffie–Hellman‐based proxy signature scheme in the standard model | |
| Tan | An efficient pairing‐free identity‐based authenticated group key agreement protocol | |
| Fan et al. | Strongly secure certificateless signature scheme supporting batch verification | |
| CN104320778B (en) | The completeness protection method of long data flow in wireless sensor network | |
| Ren et al. | Code-based authentication with designated verifier | |
| Ammayappan et al. | An ECC-Based Two-Party Authenticated Key Agreement Protocol for Mobile Ad Hoc Networks. | |
| US9054861B2 (en) | Enhanced key agreement and transport protocol | |
| Canard et al. | Group signatures are suitable for constrained devices | |
| Huang et al. | Secure Data Delivery With Certificateless Homomorphic Network Coding Signature Scheme for Autonomous Aerial Vehicle Networks. |
Legal Events
| Date | Code | Title | Description |
|---|---|---|---|
| 121 | Ep: the epo has been informed by wipo that ep was designated in this application |
Ref document number: 14784480 Country of ref document: EP Kind code of ref document: A1 |
|
| NENP | Non-entry into the national phase |
Ref country code: DE |
|
| 122 | Ep: pct application non-entry in european phase |
Ref document number: 14784480 Country of ref document: EP Kind code of ref document: A1 |